AWS Config
AWS Config is a service that enables you to assess, audit, and evaluate the configurations of your AWS resources. AWS Config continuously monitors and records your AWS resource configurations and allows you to automate the evaluation of recorded configurations against desired configurations. With AWS Config, you can review changes in configurations and relationships between AWS resources and explore detailed resource configuration histories. You can also check compliance against the configurations your internal guidelines specify. These capabilities simplify compliance auditing, security analysis, change management, and operational troubleshooting.
AWS configuration
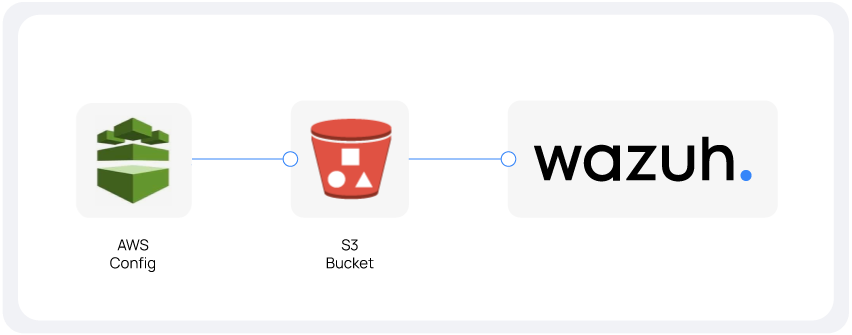
The following sections cover how to configure different services required to integrate AWS Config with Wazuh. The following diagram shows how AWS Config logs reach the Wazuh agent through an S3 bucket.
AWS Config configuration
On your AWS console, search for
aws configin the search bar, then on the AWS Config page, click Get started.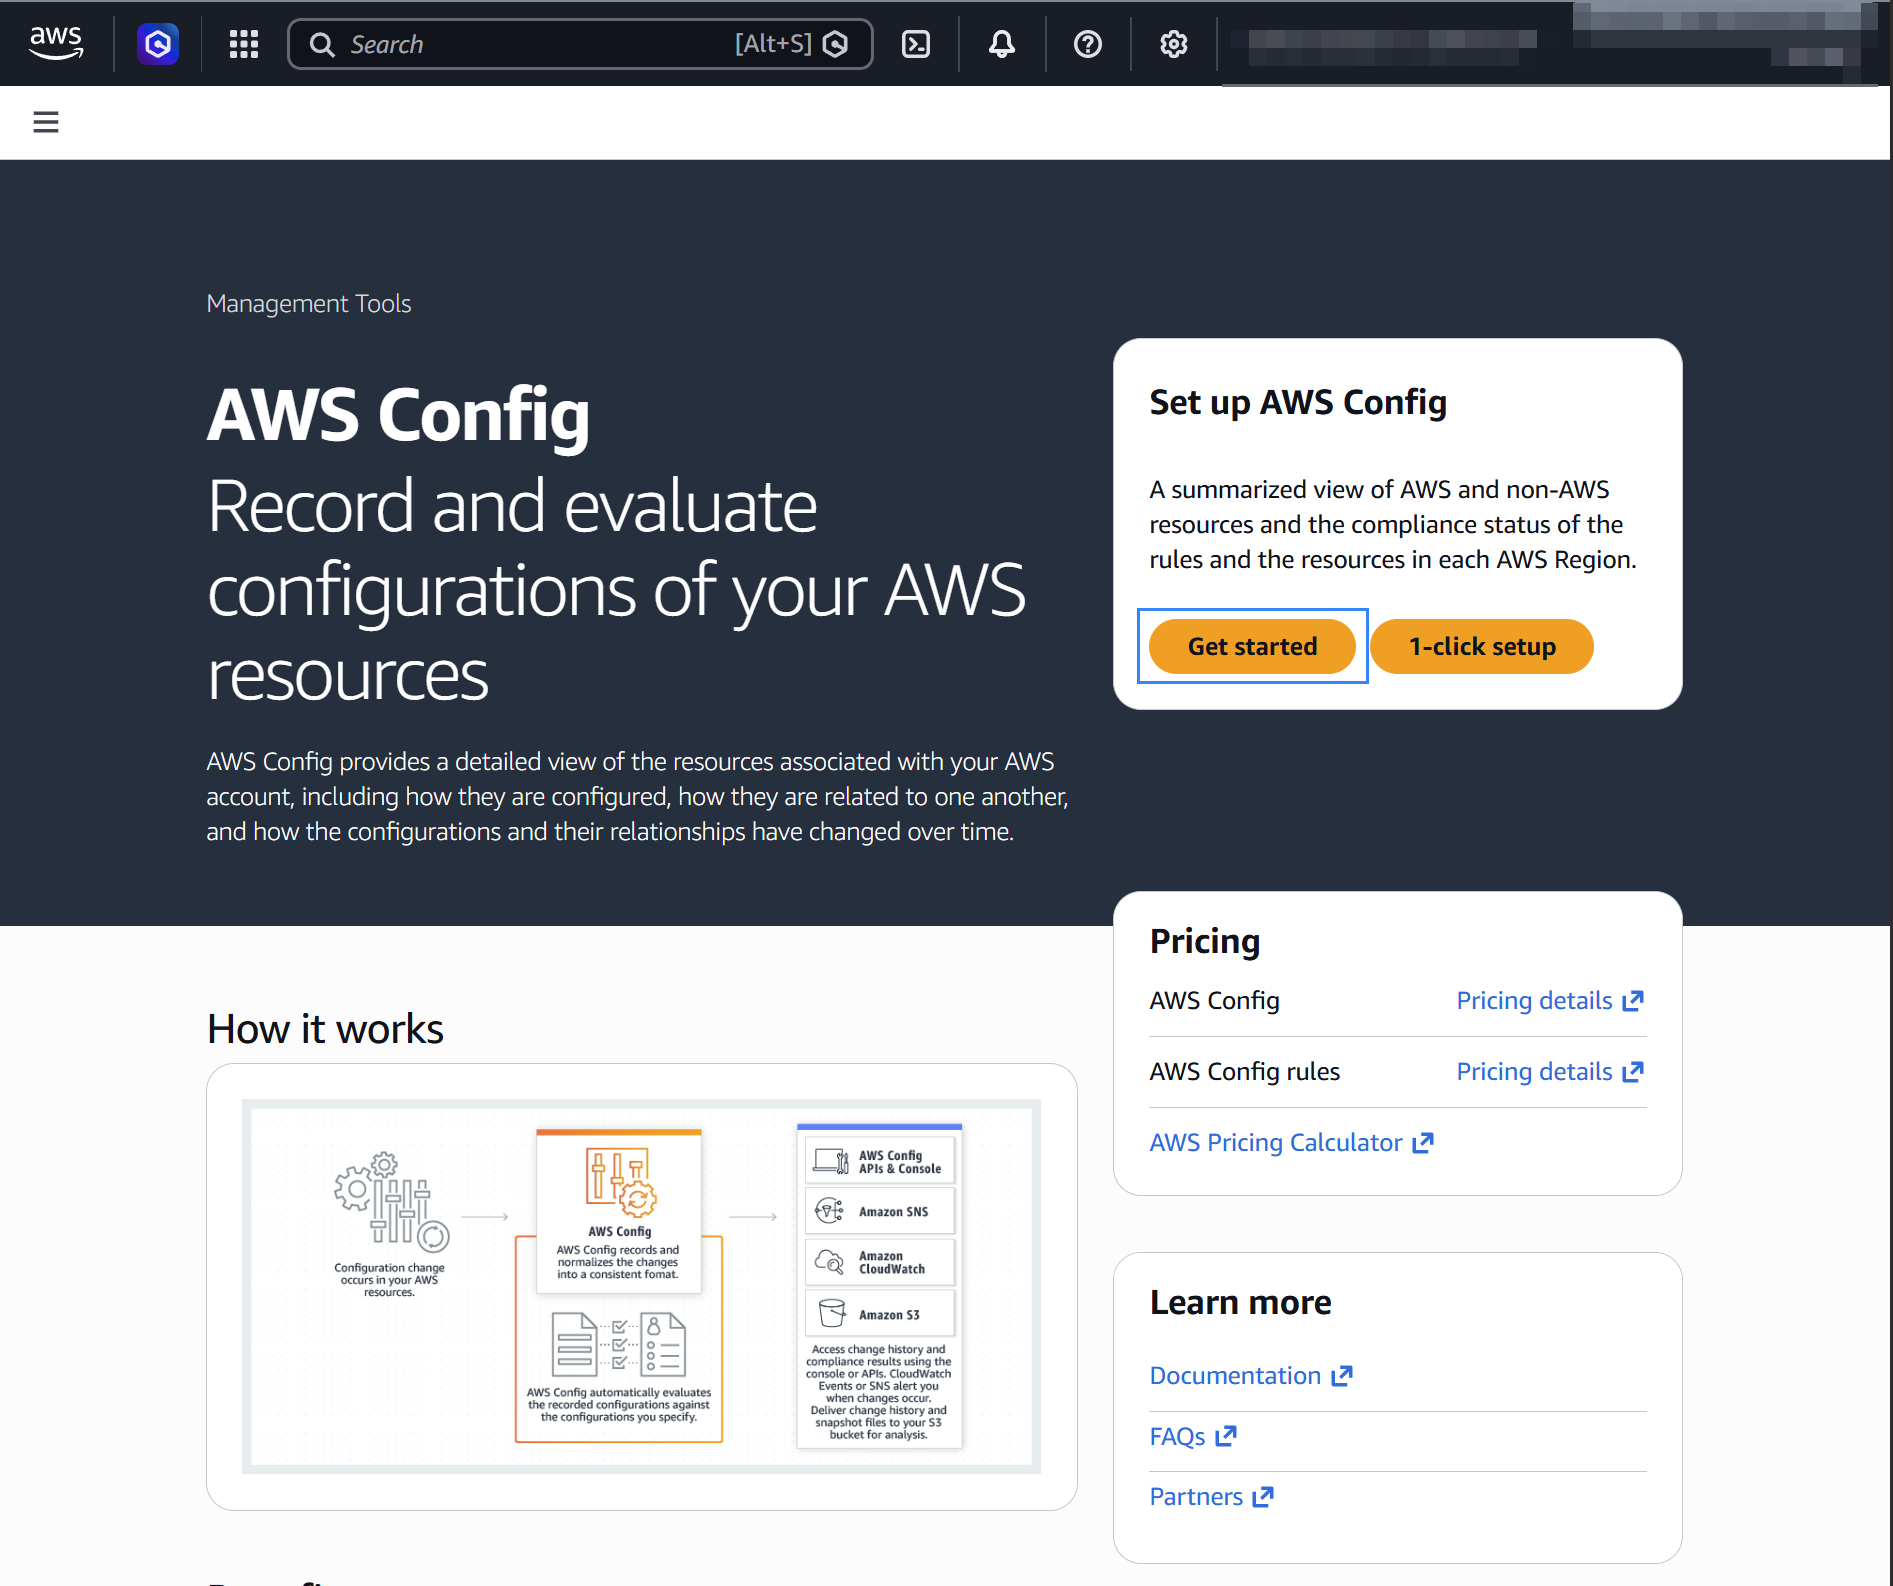
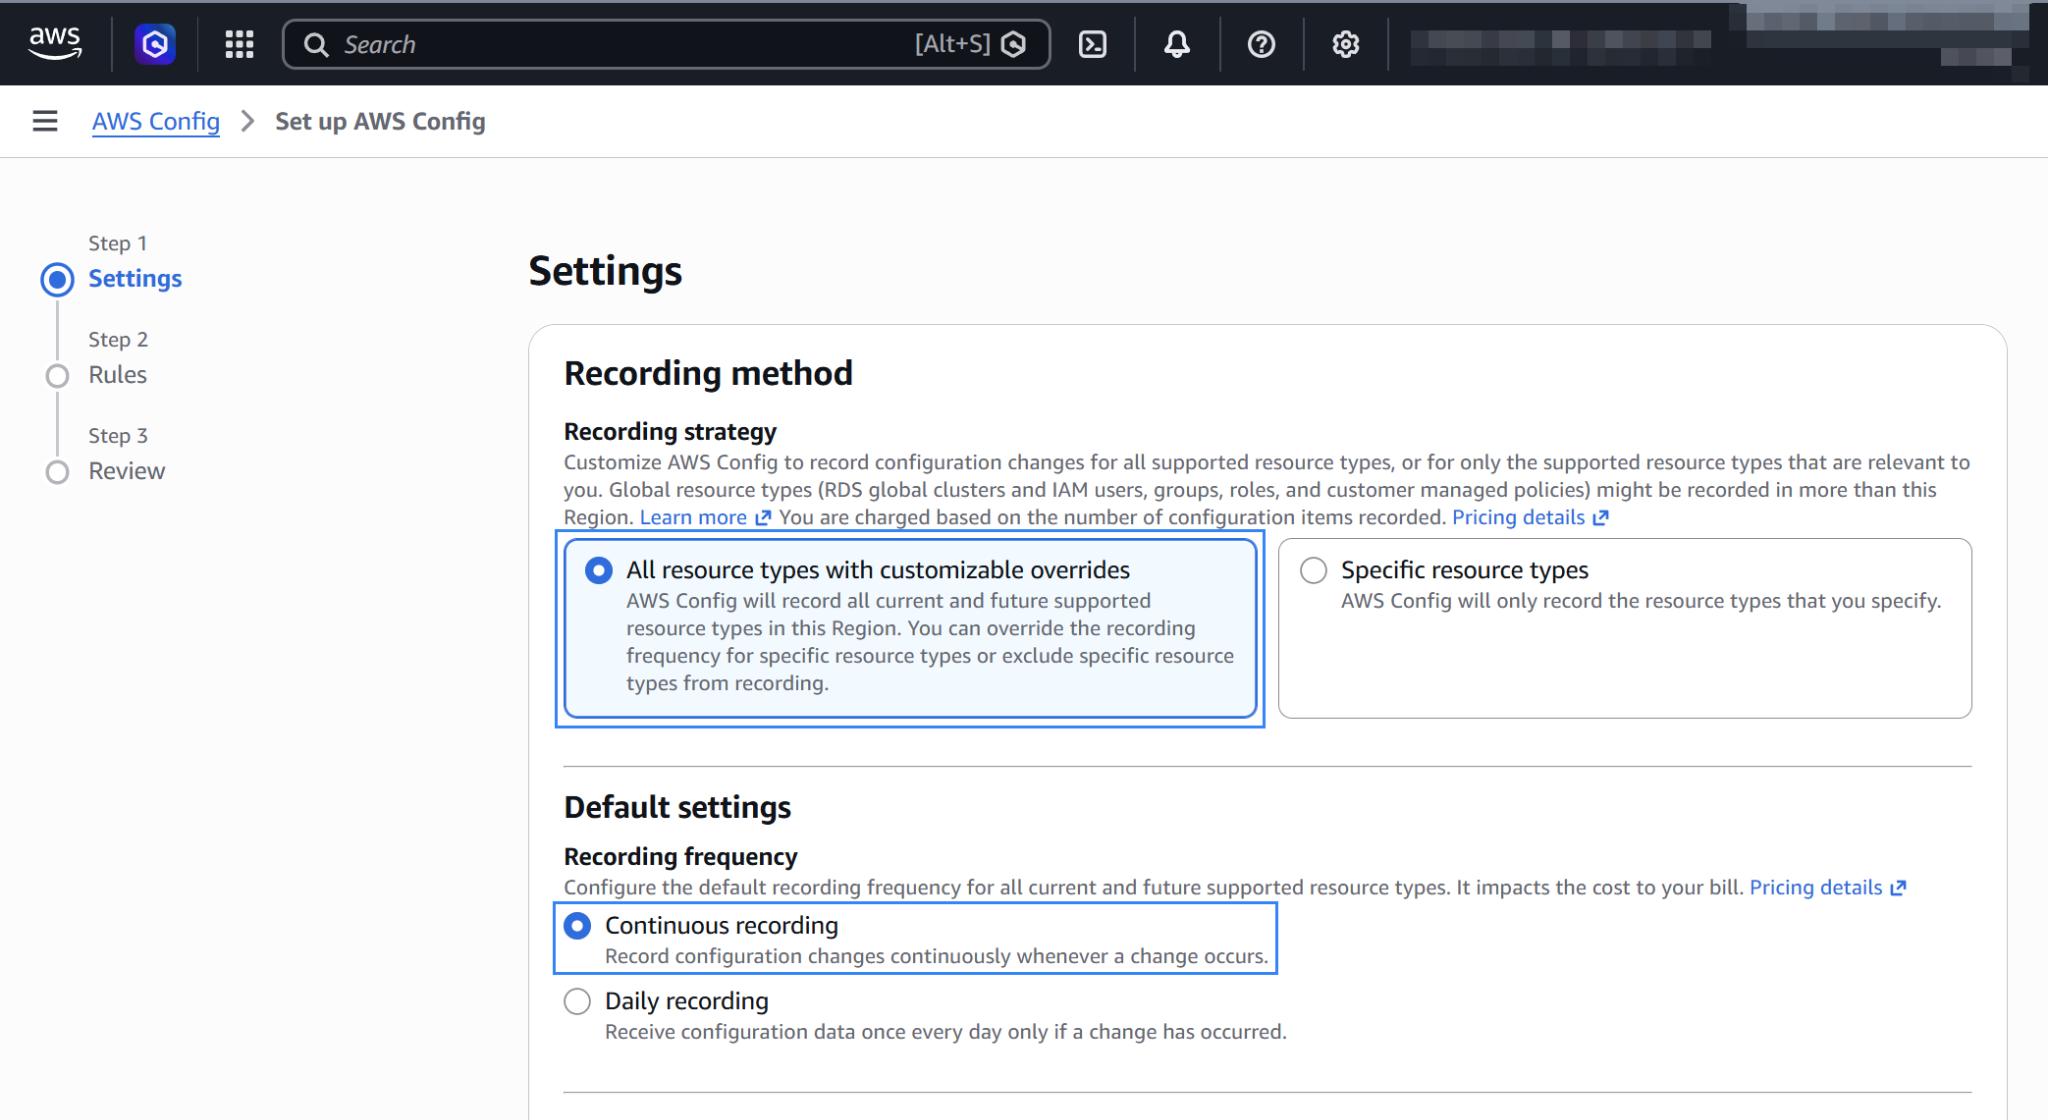
Under Recording strategy, specify the AWS resource types you want AWS Config to record:
All resource types with customizable overrides
Specific resource types
Note
For more information about these options, see selecting which resources AWS Config records.
Under IAM role for AWS Config, choose the AWS Config service-linked role or a role from your account.
Select an existing S3 bucket or create a new one, and enter a prefix, for example,
config. Then click Next through the remaining steps until you reach the Review page.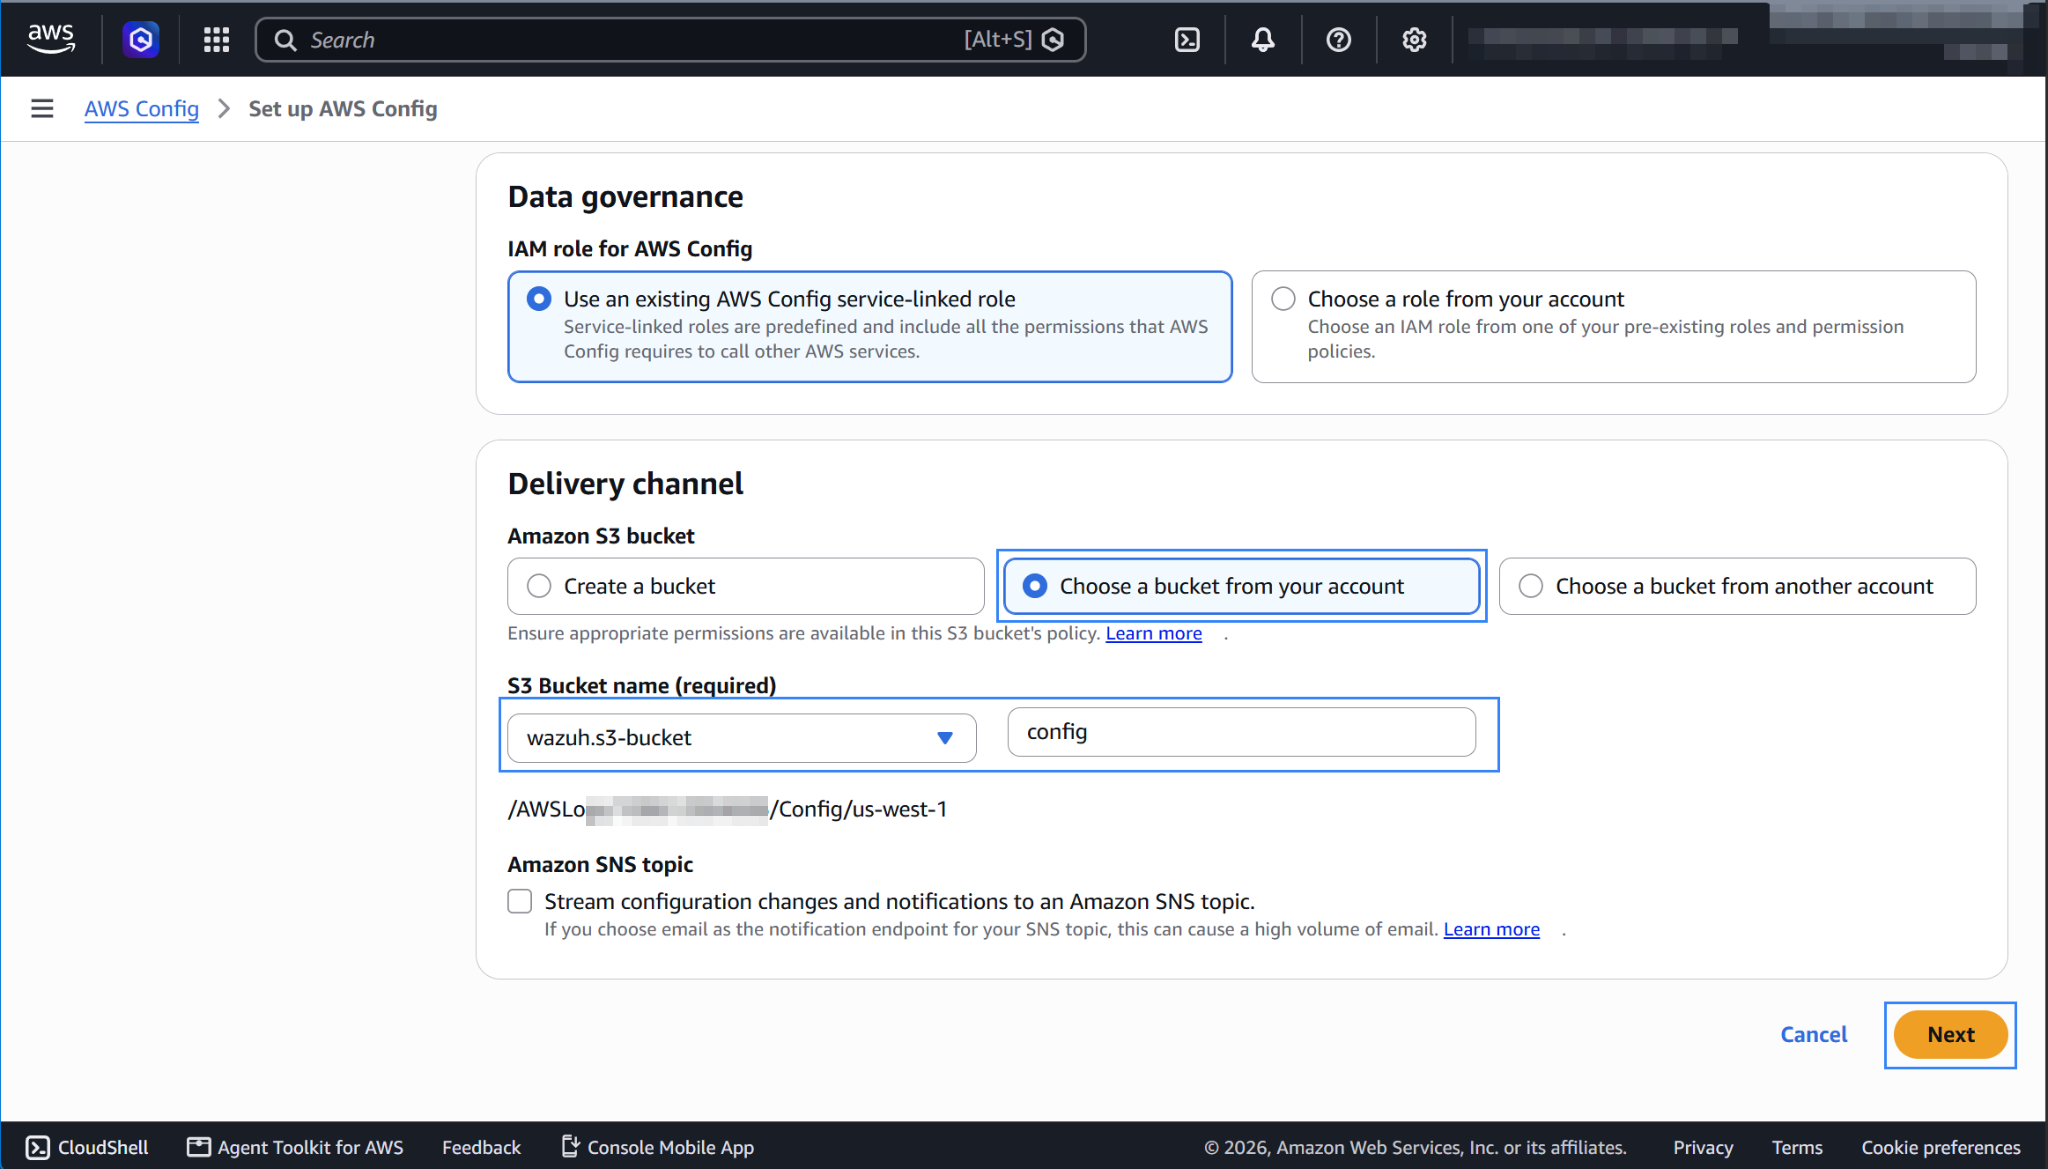
Review the configuration and click Confirm.
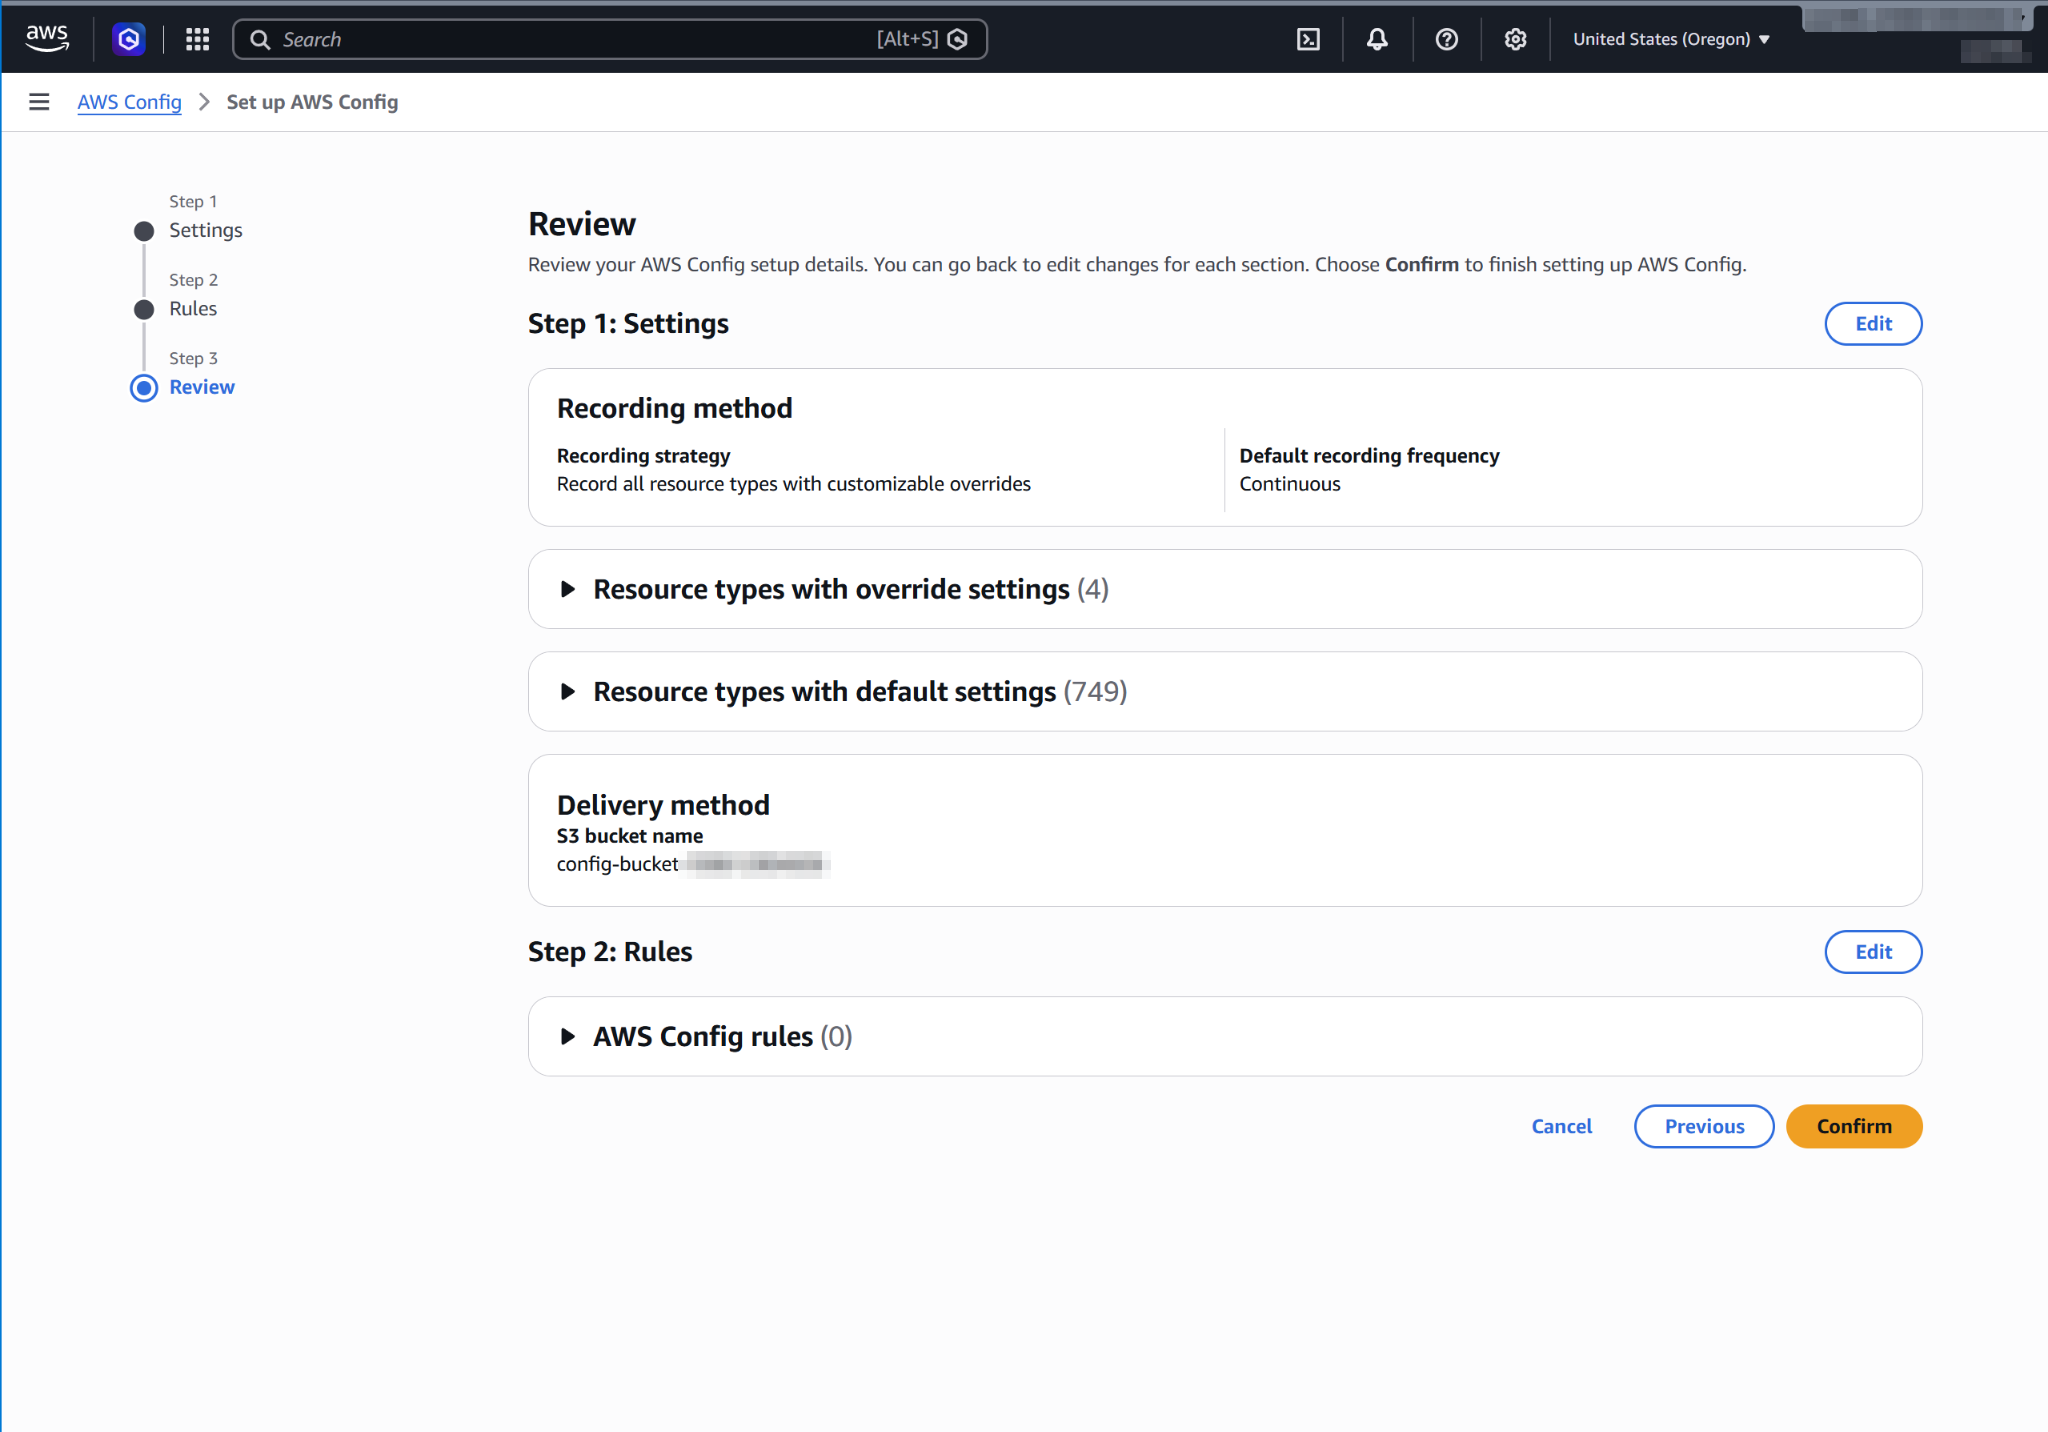
AWS Config delivers configuration history files to <WAZUH_AWS_BUCKET>/<PREFIX>/AWSLogs/<ACCOUNT_ID>/Config/<REGION>/ about every 6 hours, so the first events can take that long to appear.
Policy configuration
Follow the creating an AWS policy guide to create a policy using the Amazon Web Services console.
The policies below follow the principle of least privilege, so they give the AWS IAM user only the minimum permissions it needs.
To allow an AWS user to use the Wazuh module for AWS with read-only permissions, it must have a policy like the following attached:
{
    "Version": "2012-10-17",
    "Statement": [
        {
            "Sid": "VisualEditor0",
            "Effect": "Allow",
            "Action": [
                "s3:GetObject",
                "s3:ListBucket"
            ],
            "Resource": [
                "arn:aws:s3:::<WAZUH_AWS_BUCKET>/*",
                "arn:aws:s3:::<WAZUH_AWS_BUCKET>"
            ]
        }
    ]
}
To delete the log files after Wazuh collects them, use the following policy instead:
{
    "Version": "2012-10-17",
    "Statement": [
        {
            "Sid": "VisualEditor0",
            "Effect": "Allow",
            "Action": [
                "s3:GetObject",
                "s3:ListBucket",
                "s3:DeleteObject"
            ],
            "Resource": [
                "arn:aws:s3:::<WAZUH_AWS_BUCKET>/*",
                "arn:aws:s3:::<WAZUH_AWS_BUCKET>"
            ]
        }
    ]
}
Note
<WAZUH_AWS_BUCKET> is a placeholder. Replace it with the actual name of the bucket from which you want to retrieve logs.
Wazuh deletes the log files from the bucket only if you set remove_from_bucket to yes in the bucket configuration. This option is off by default and isn't in the sample configuration, so you need the second policy only if you turn it on.
After creating a policy, you can attach it directly to a user or to a group to which the user belongs. In attaching a policy to an IAM user group, you see how to attach a policy to a group. More information on how to use other methods is available in the AWS documentation.
Configure Wazuh to process AWS Config logs
Make sure that the AWS integrations are enabled on the Wazuh dashboard, as described in Enable AWS integration on the Wazuh dashboard.
Add the following Wazuh module for AWS configuration to the
/var/ossec/etc/ossec.conffile on the Wazuh agent. Set<path>to the prefix you entered in AWS Config and replace<WAZUH_AWS_BUCKET>with the name of the S3 bucket. If the file already has a<wodle name="aws-s3">block, add only the<bucket>section to it:<wodle name="aws-s3"> <disabled>no</disabled> <interval>10m</interval> <run_on_start>yes</run_on_start> <skip_on_error>yes</skip_on_error> <bucket type="config"> <name><WAZUH_AWS_BUCKET></name> <path>config</path> <aws_profile>default</aws_profile> </bucket> </wodle>
Note
This example uses the
aws_profileauthentication parameter. Check the Configure AWS credentials section to learn more about the different authentication options and how to use them.Save the changes and restart the Wazuh agent service to apply the changes:
# systemctl restart wazuh-agent
AWS Config use cases
AWS Config allows you to review changes in configuration and relationships between AWS resources. Below is an example of a use case for AWS Config.
Monitoring configuration changes
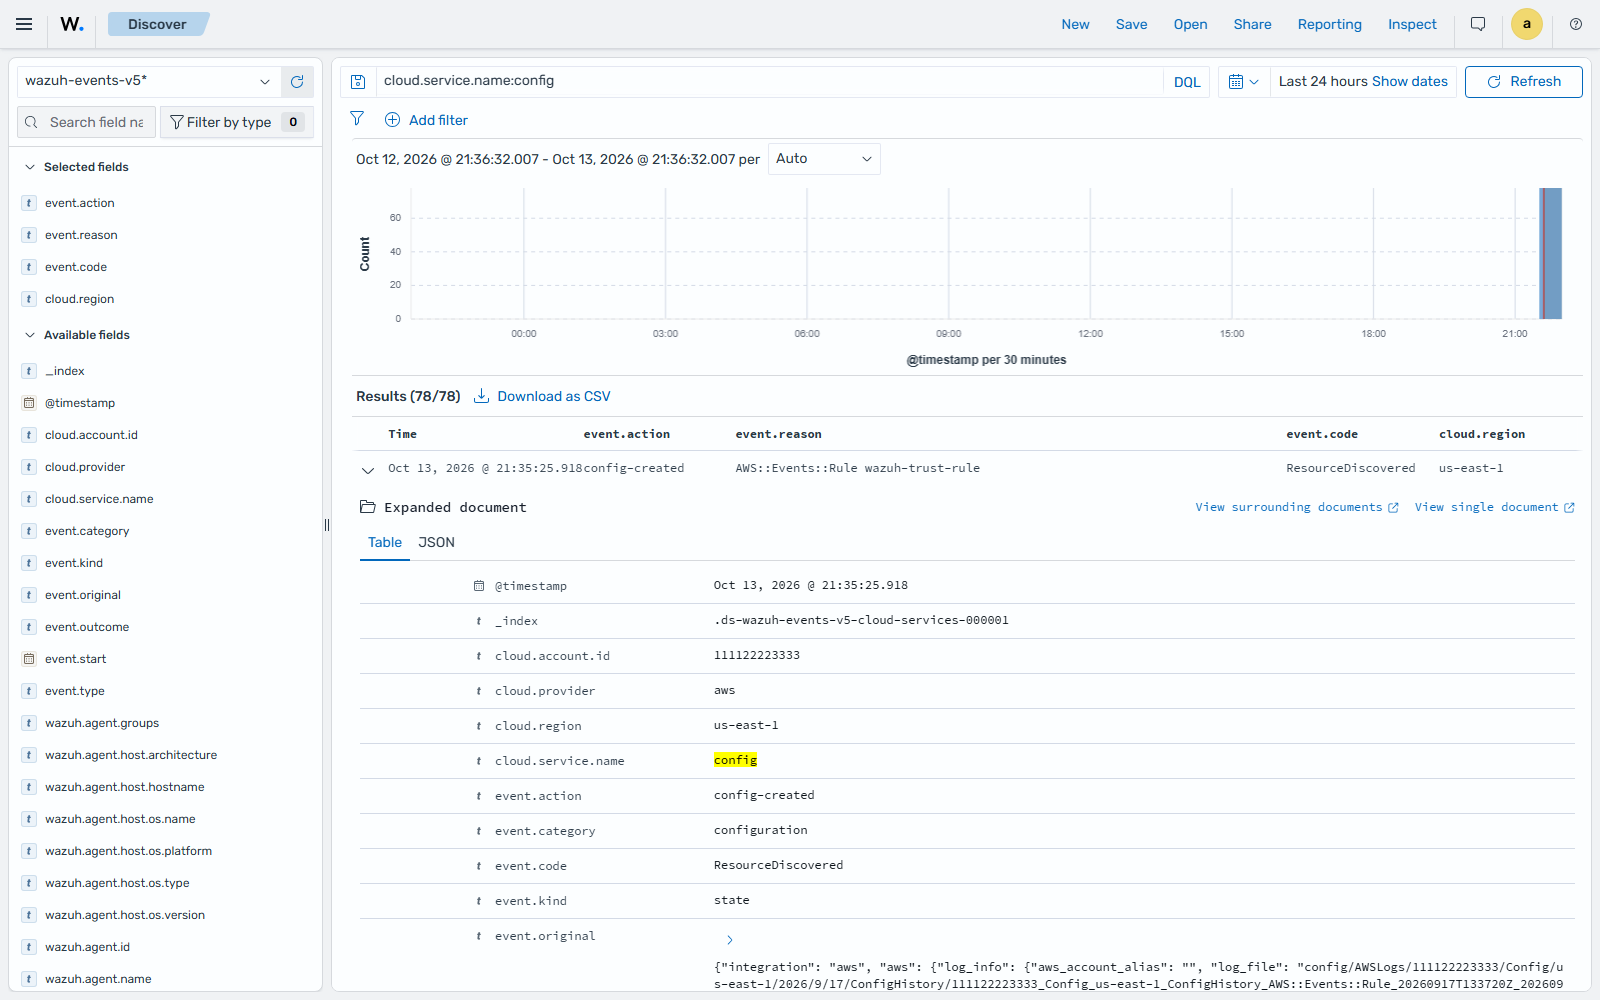
AWS Config configuration changes appear as events on the Wazuh dashboard. To see them, go to Explore > Discover, select the wazuh-events-v5* index pattern, and filter by cloud.service.name: config. These events don't raise findings.
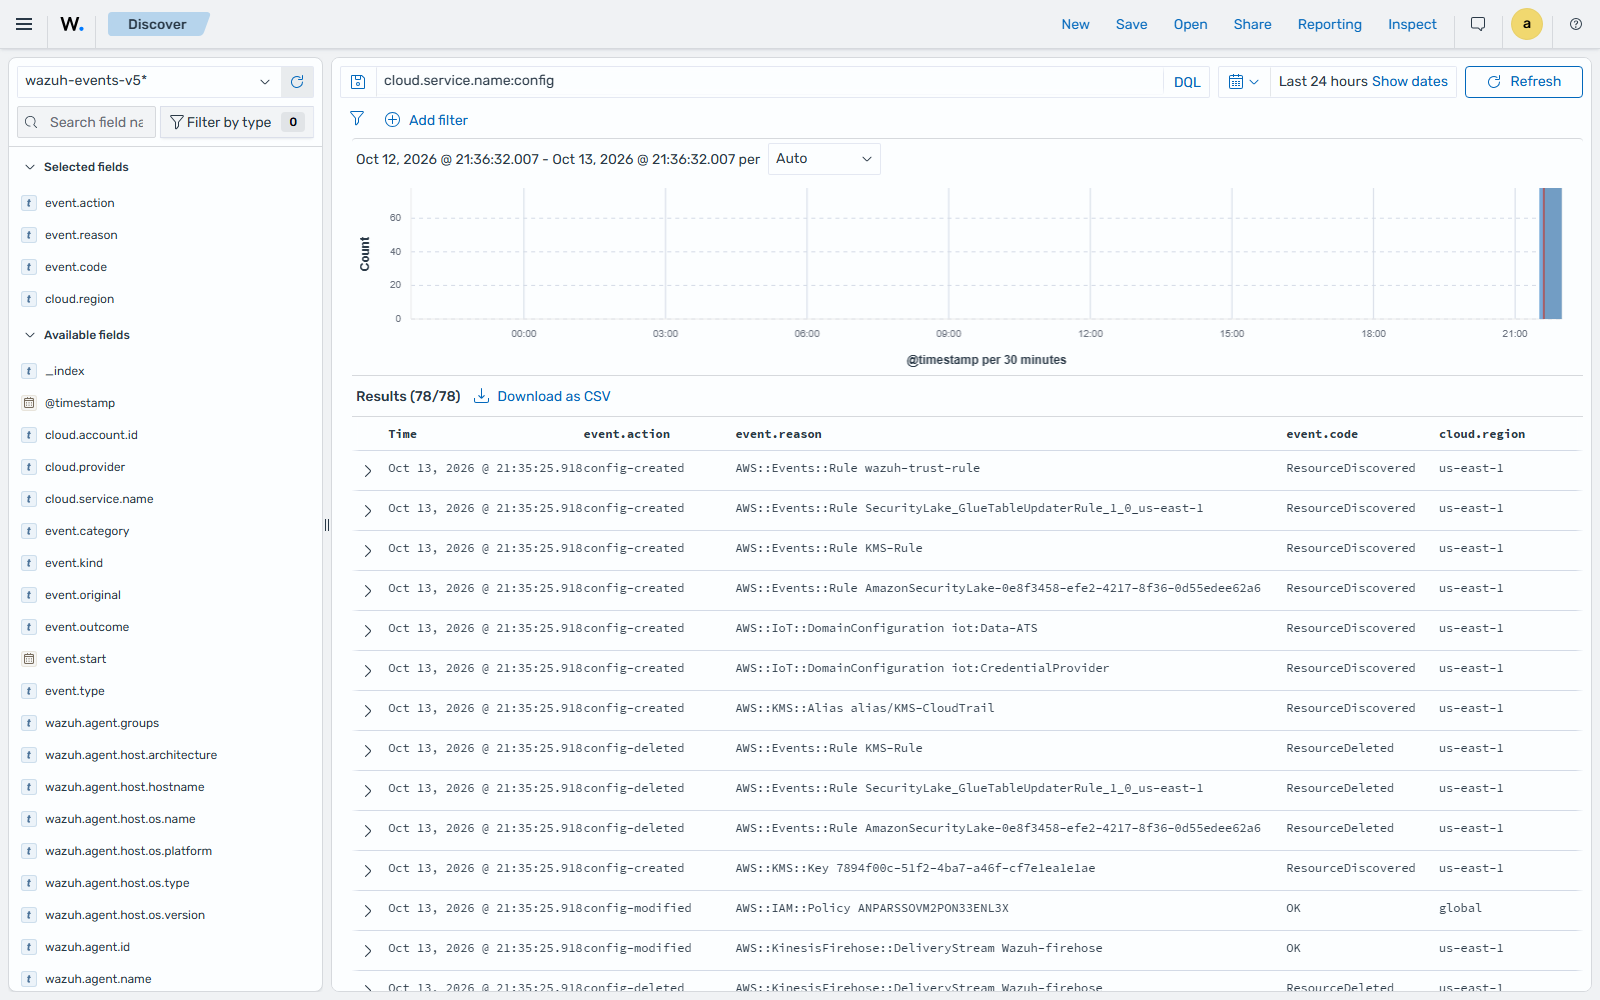
Expand an event to see its details:
Type of change (
event.action:config-created,config-modified, orconfig-deleted)Resource type and name (
event.reason, for exampleAWS::Events::Rulewazuh-trust-rule)Configuration item status (
event.code, for exampleResourceDiscovered)Time AWS Config recorded the change (
event.start)AWS account and region (
cloud.account.idandcloud.region)Full configuration item (
event.original)