Amazon Macie
Amazon Macie is a security service that uses machine learning to automatically discover, classify, and protect sensitive data in AWS. Macie recognizes sensitive data, such as personally identifiable information (PII) or intellectual property. It provides dashboards and alerts that show how this data is accessed or moved. The fully managed service continuously monitors data access activity for anomalies and generates detailed alerts when it detects potential unauthorized access or inadvertent data leaks.
AWS configuration
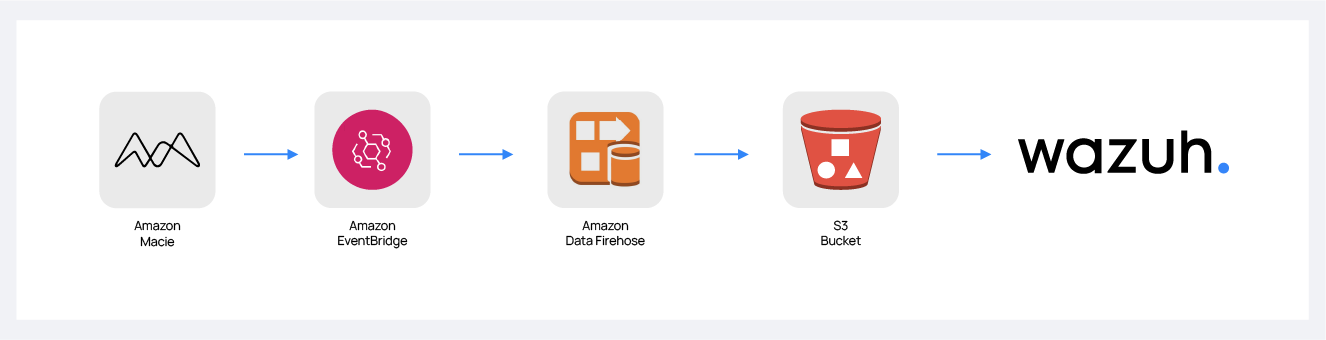
The following sections cover how to configure the services required to integrate Amazon Macie with Wazuh. The following diagram shows how Amazon Macie events reach the Wazuh agent through Amazon EventBridge, Amazon Data Firehose, and an S3 bucket.
Amazon Data Firehose configuration
Create an Amazon Data Firehose delivery stream to store the Amazon Macie events into the desired S3 bucket so Wazuh can process them.
Create a new S3 bucket, or skip this step to use an existing bucket.
On your AWS console, search for
amazon data firehosein the search bar or go to Services > Analytics > Amazon Data Firehose.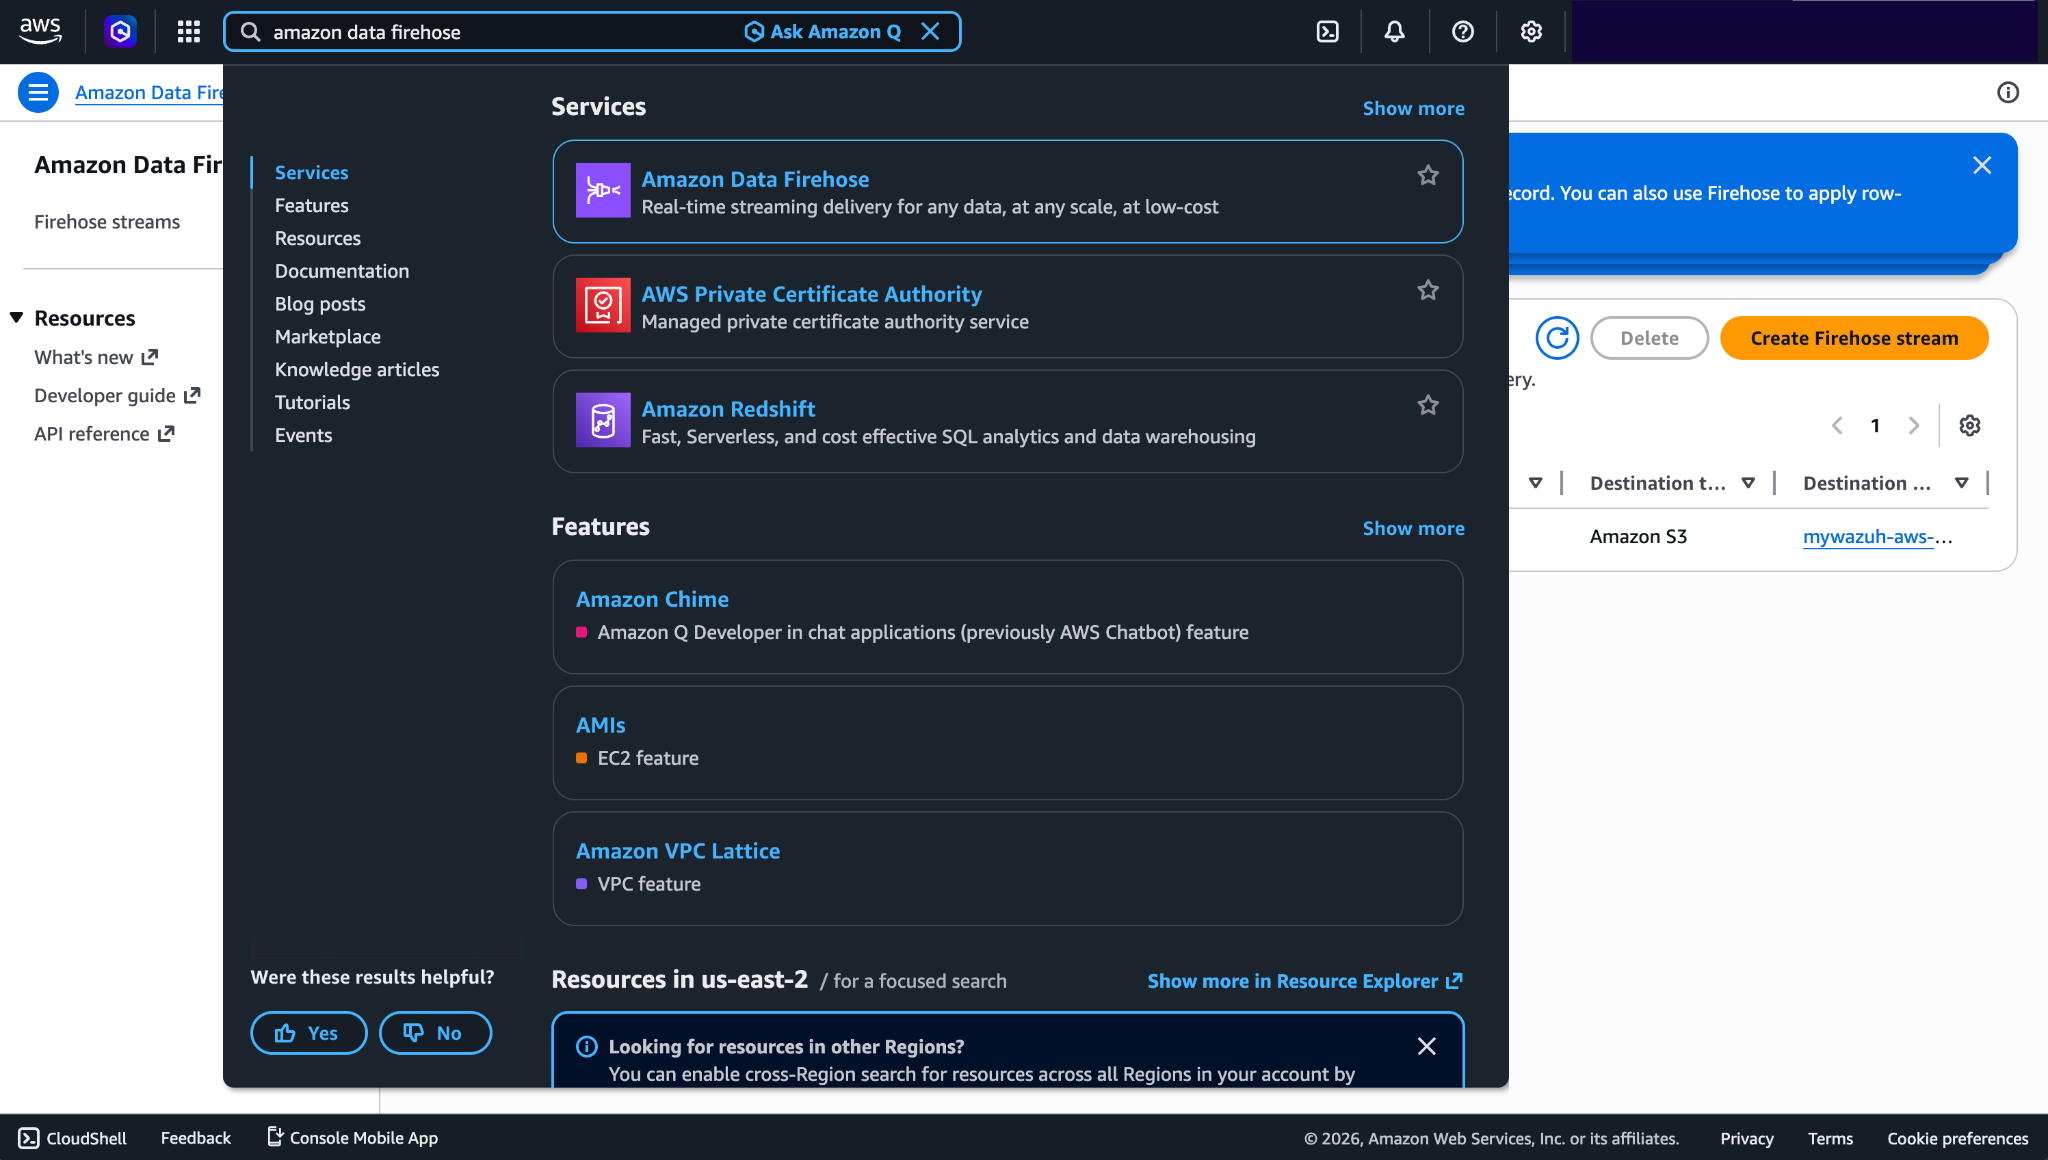
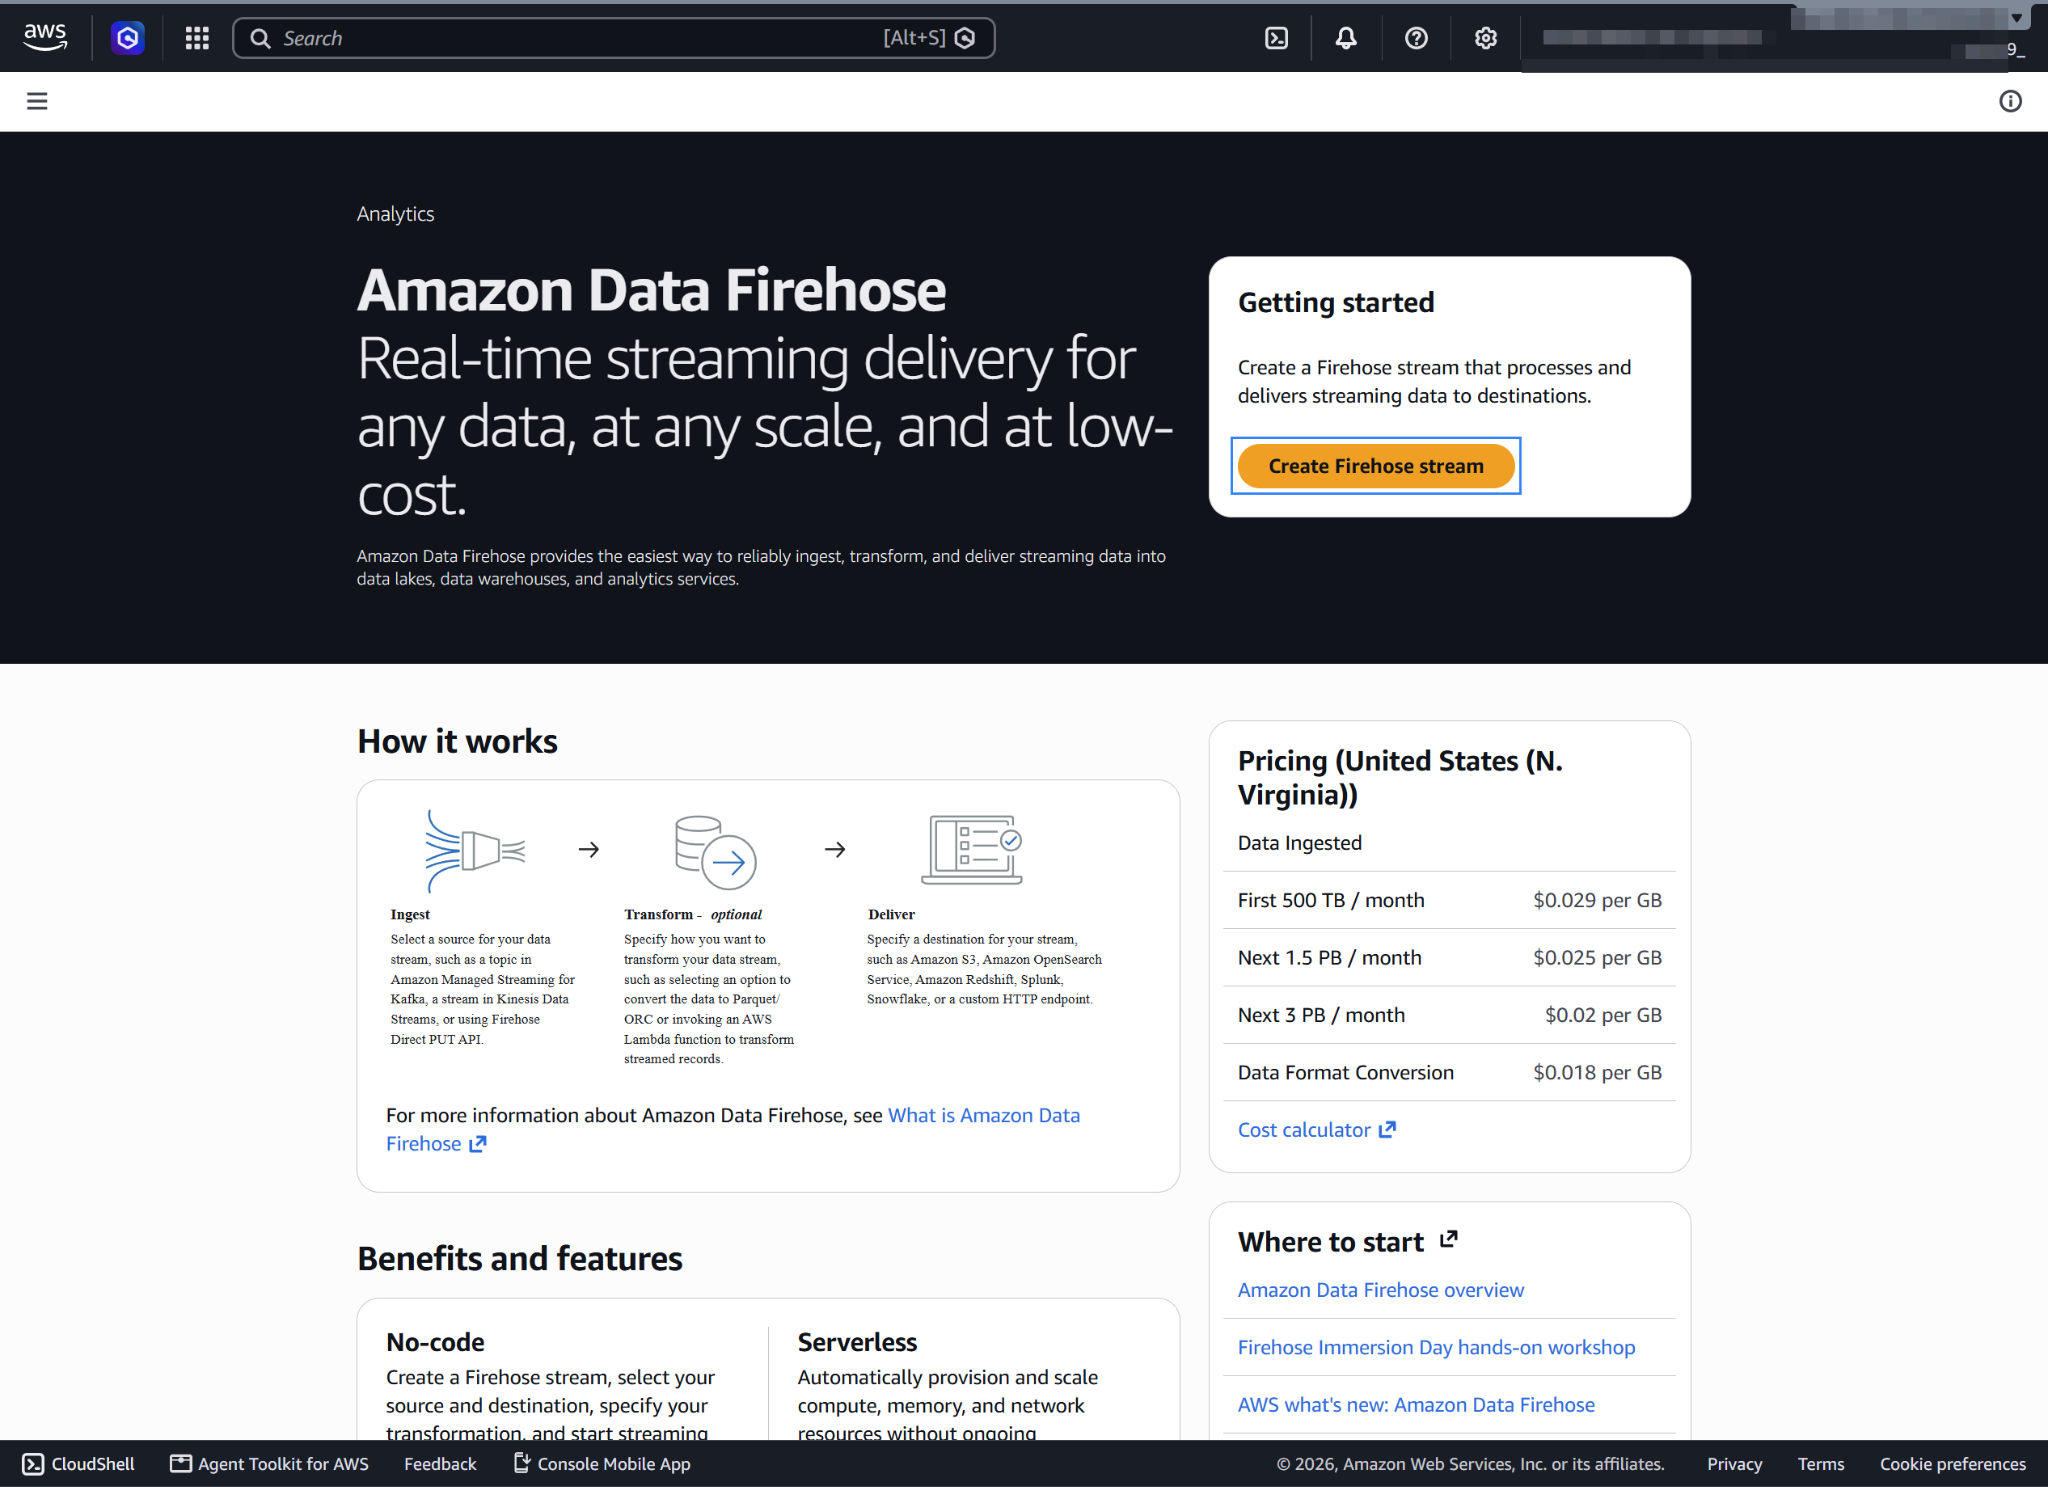
Click Create Firehose stream.
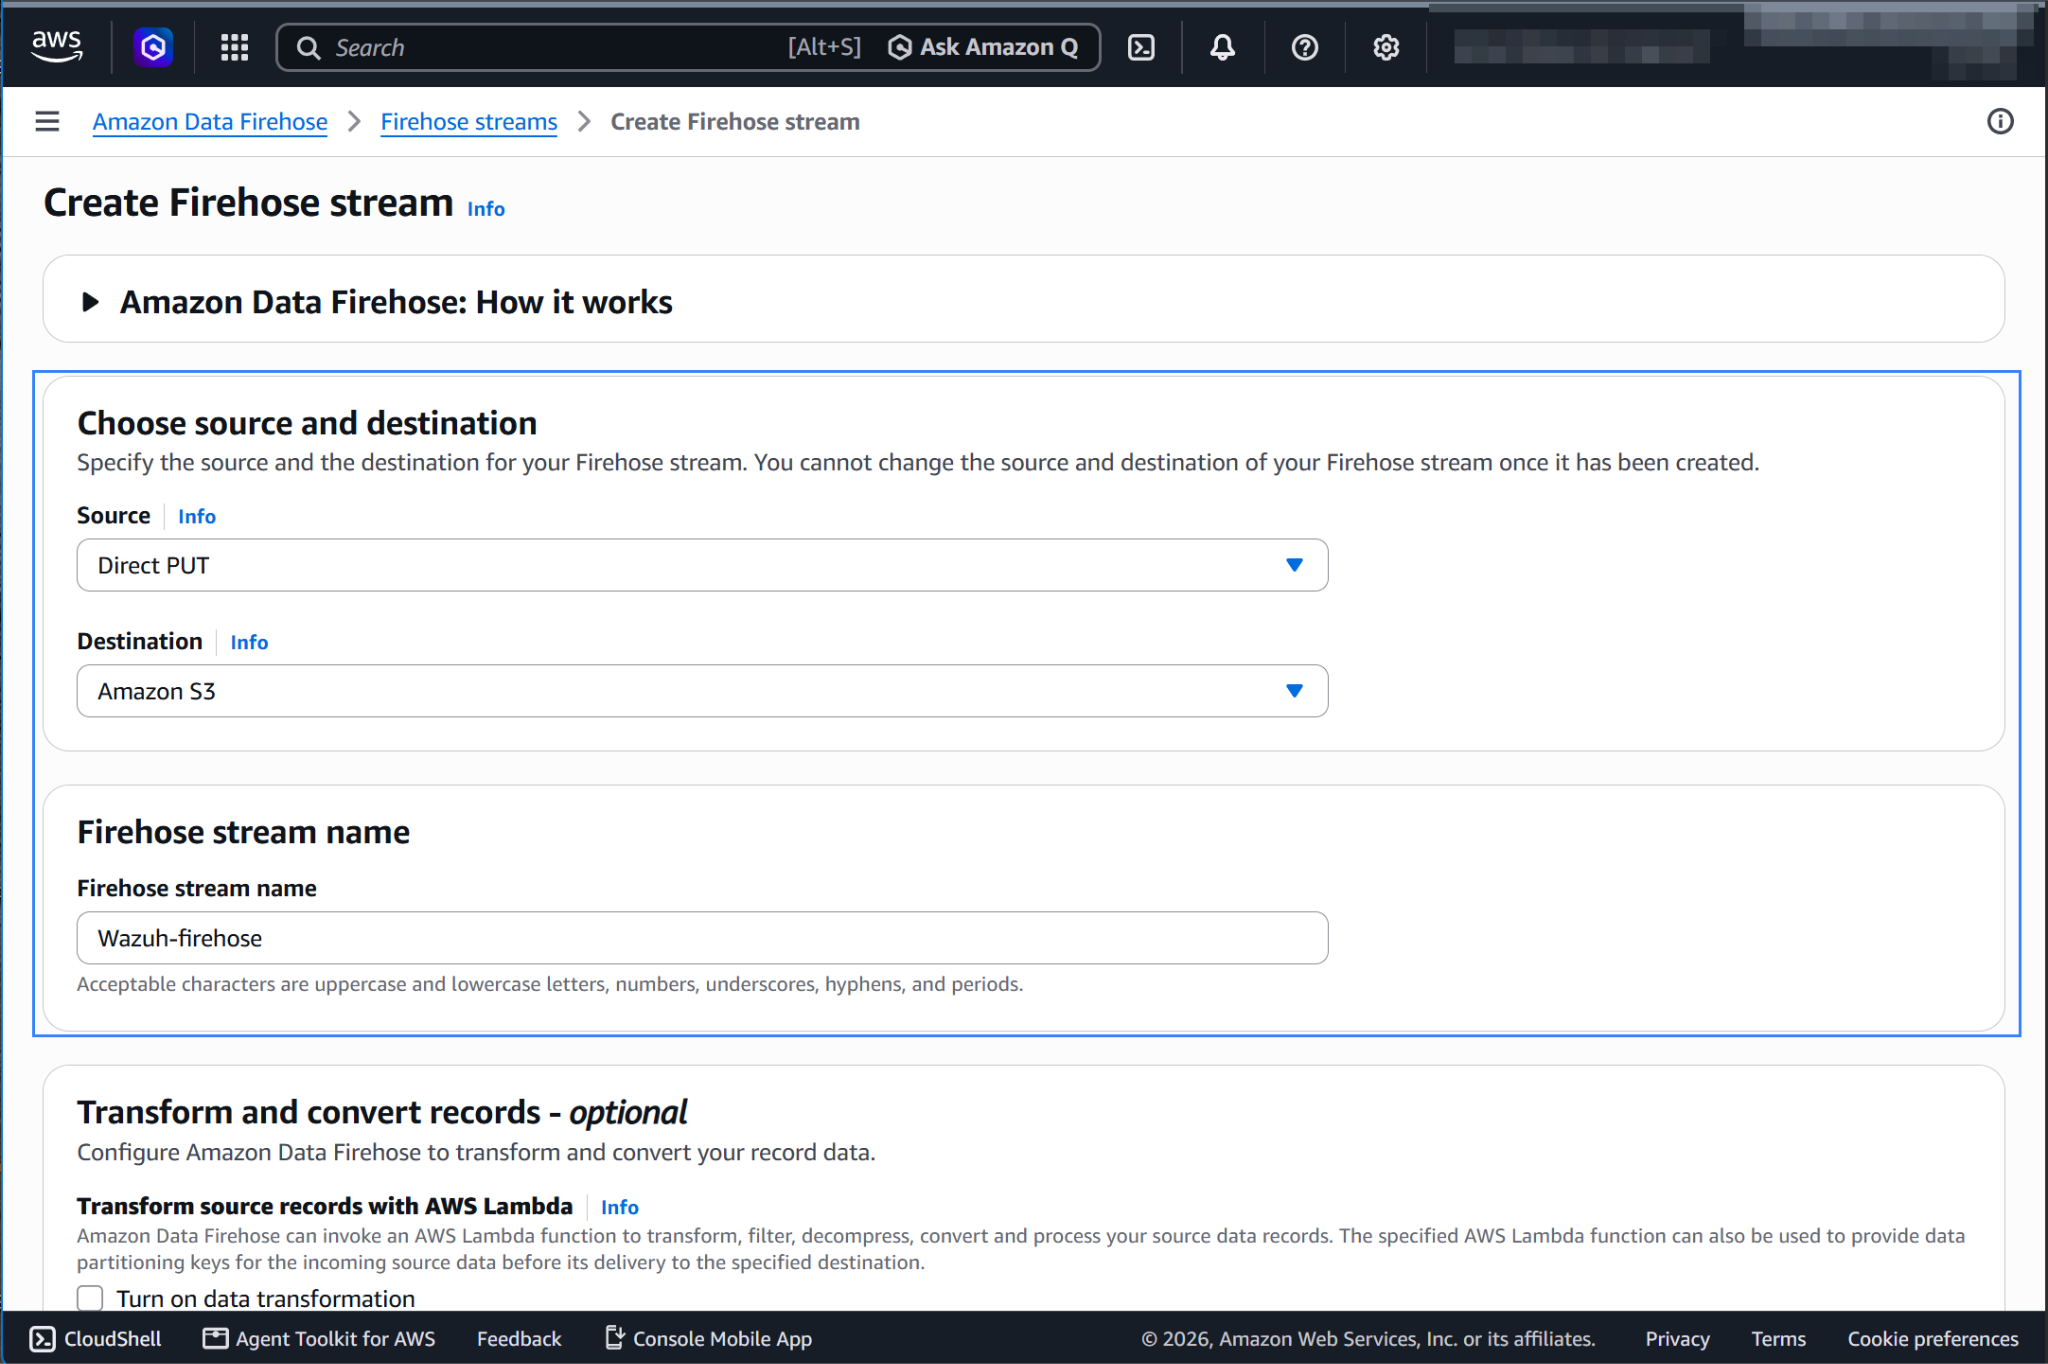
Select Direct PUT and Amazon S3 as the desired Source and Destination, respectively, and choose an appropriate Firehose stream name.
Select the desired S3 bucket as the destination. You can specify a custom prefix to change the path where AWS stores the logs. Amazon Data Firehose creates a file structure
YYYY/MM/DD/HH. If you use a prefix, the file structure isprefix-name/YYYY/MM/DD/HH, and you must specify the prefix under the Wazuh bucket configuration. In this example, the prefix ismacie/.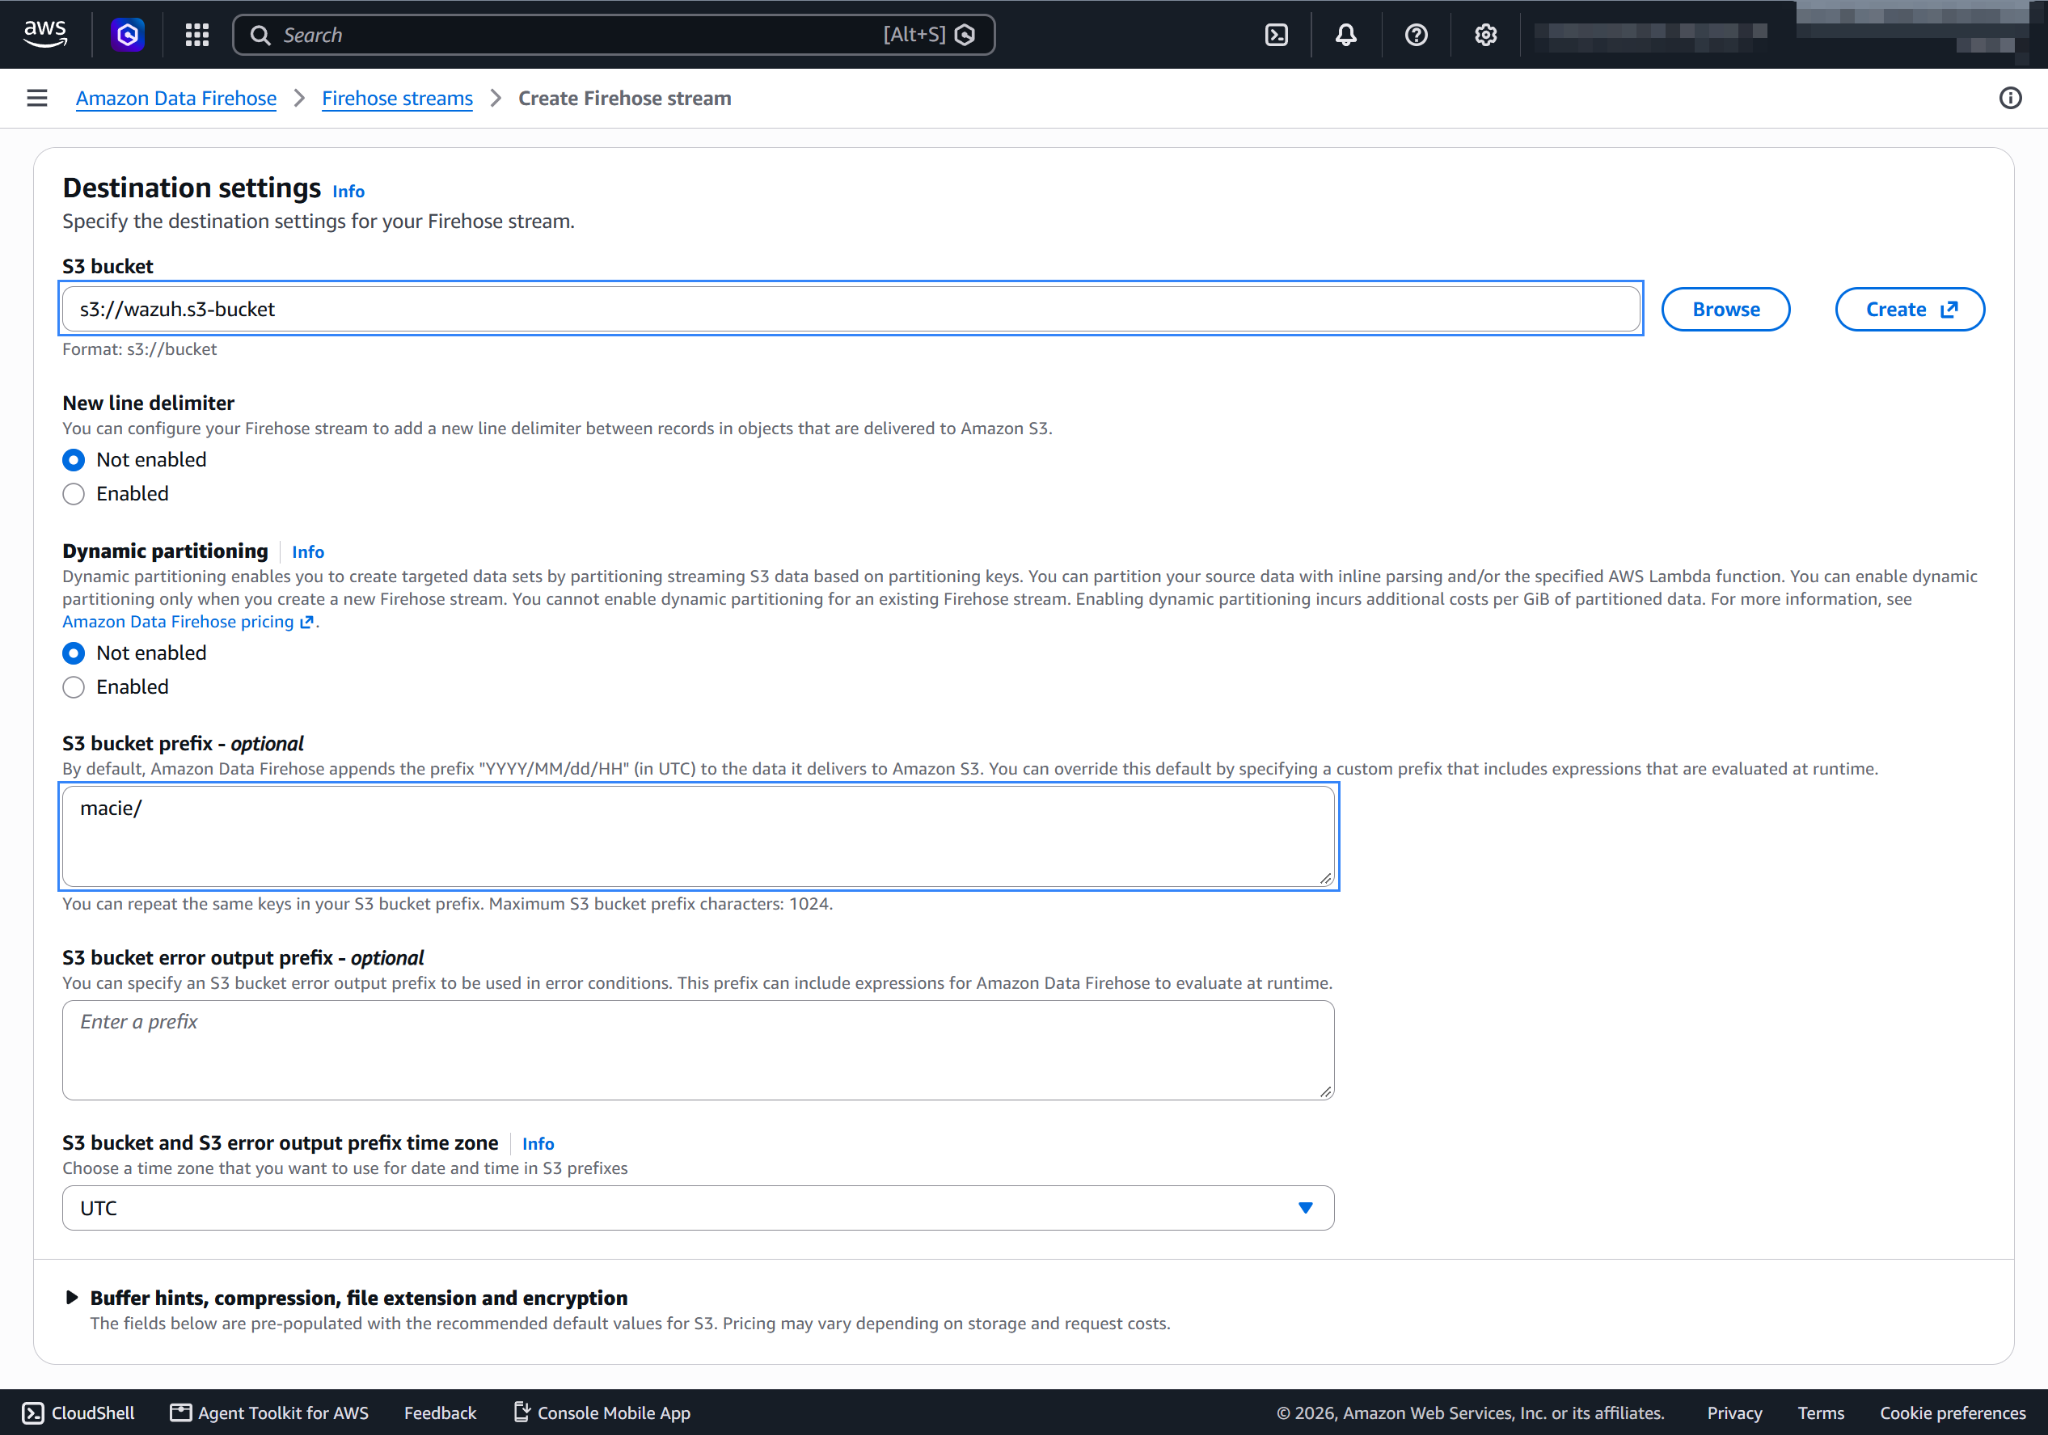
Create or choose an existing IAM role to be used by Amazon Data Firehose in the Advanced settings section.
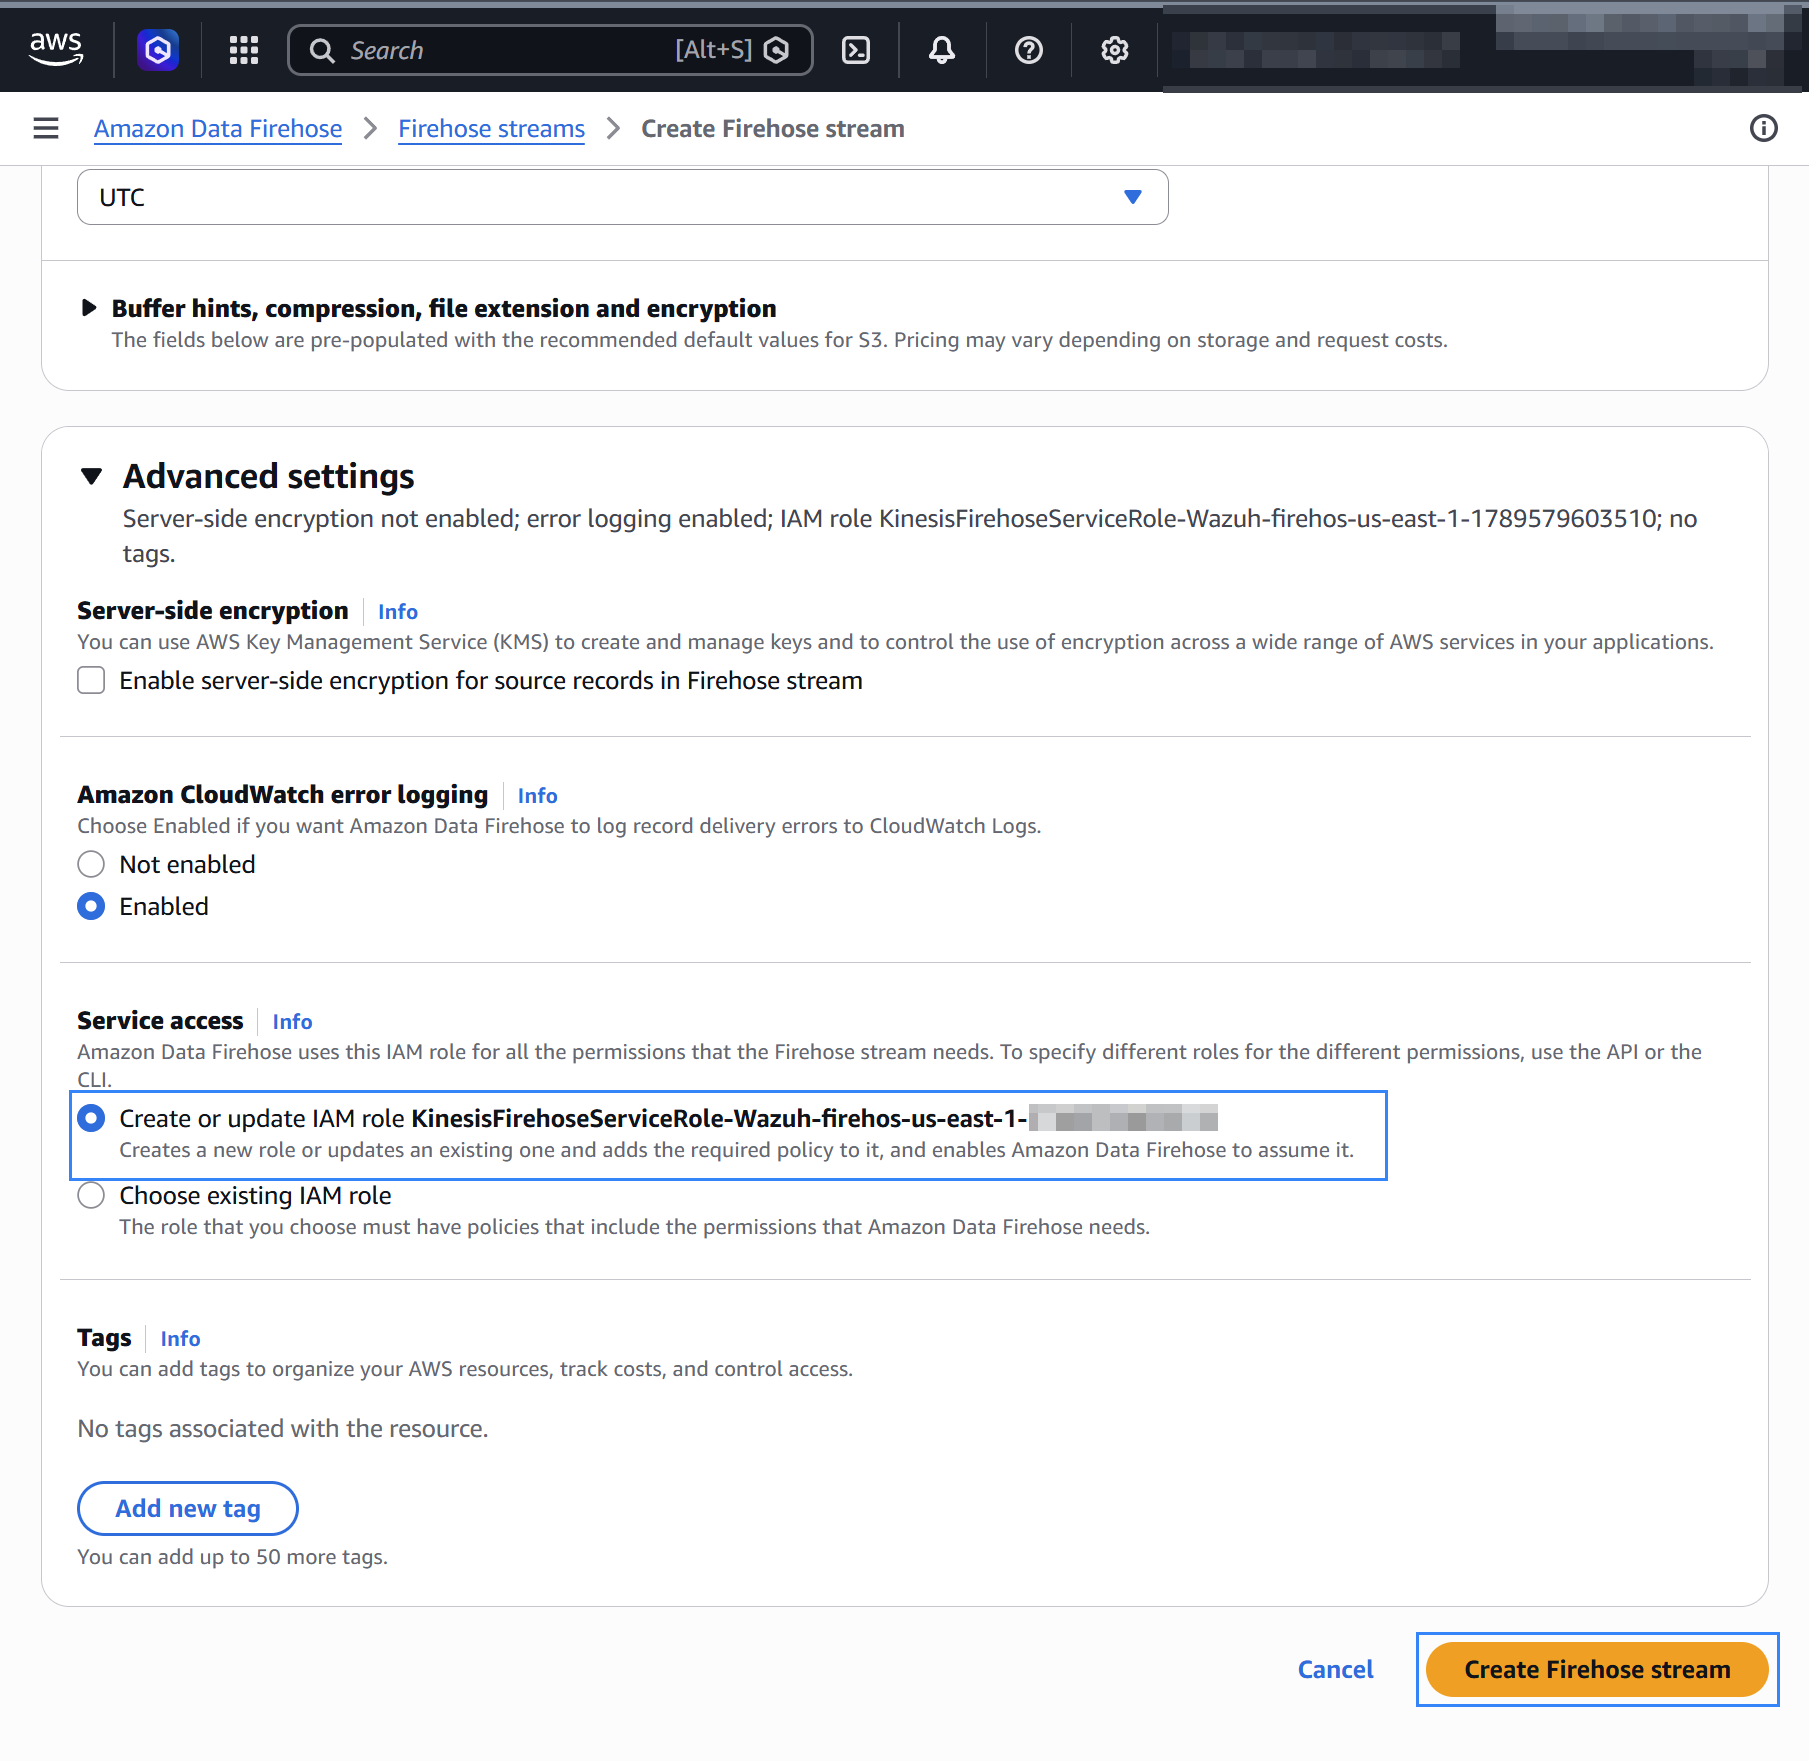
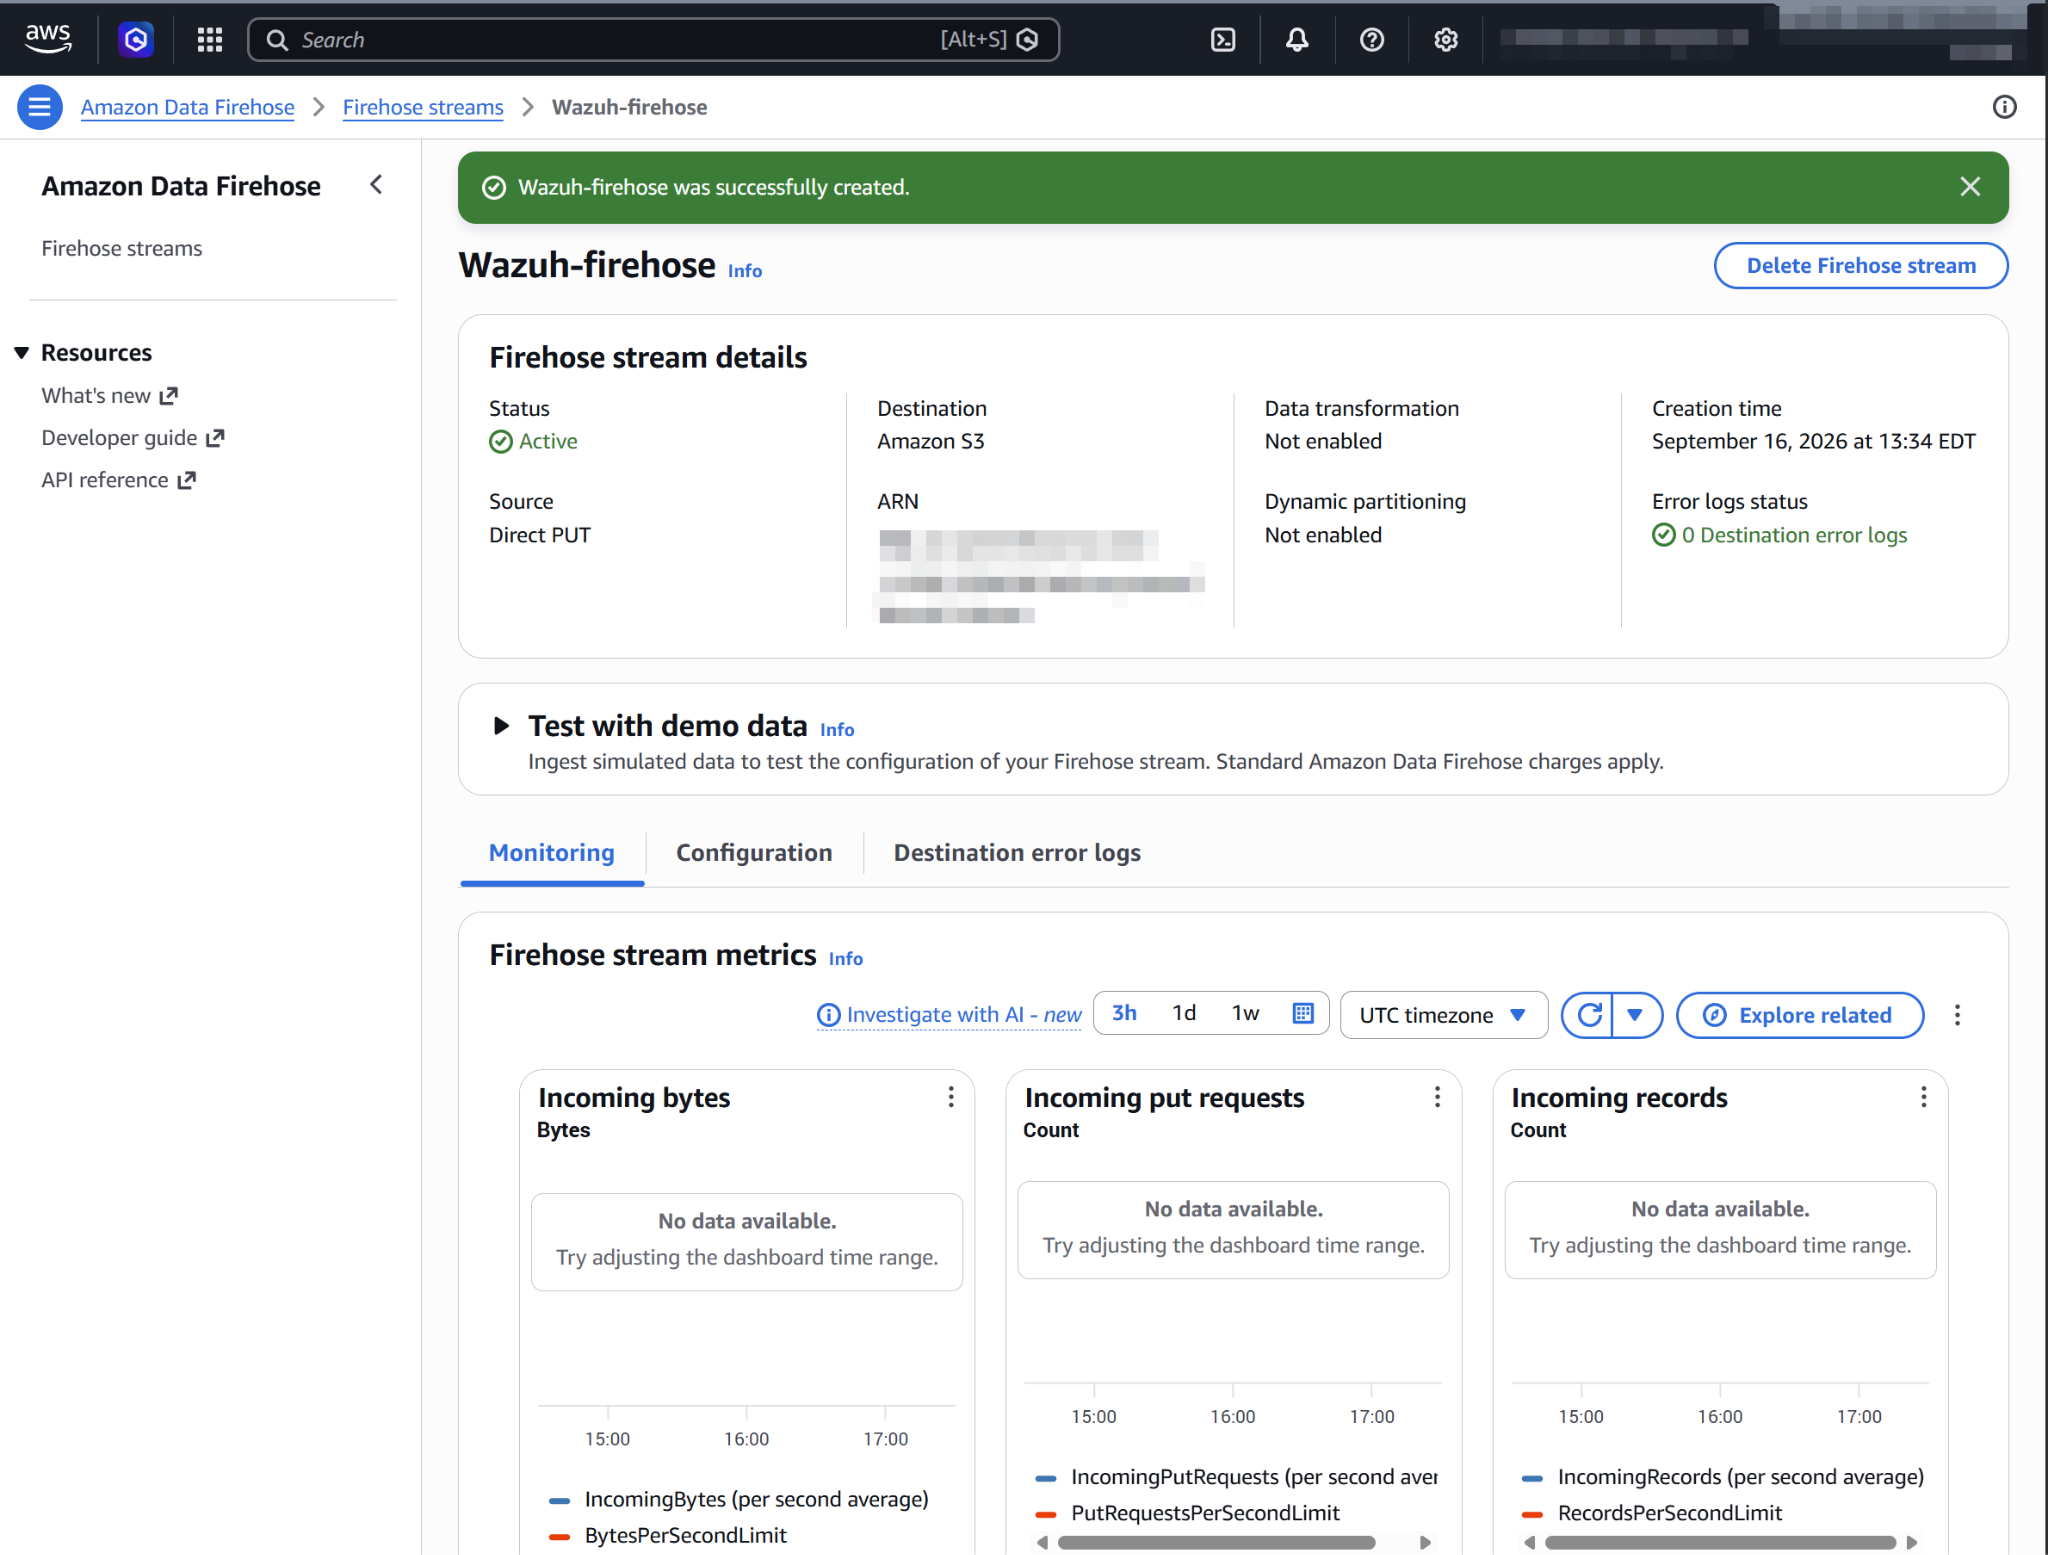
Click Create Firehose stream at the end of the page.
Amazon EventBridge configuration
Configure an Amazon EventBridge rule to send Macie events to the Amazon Data Firehose delivery stream created in the previous step.
On your AWS console, search for
eventbridgein the search bar or go to Services > Application Integration > Amazon EventBridge.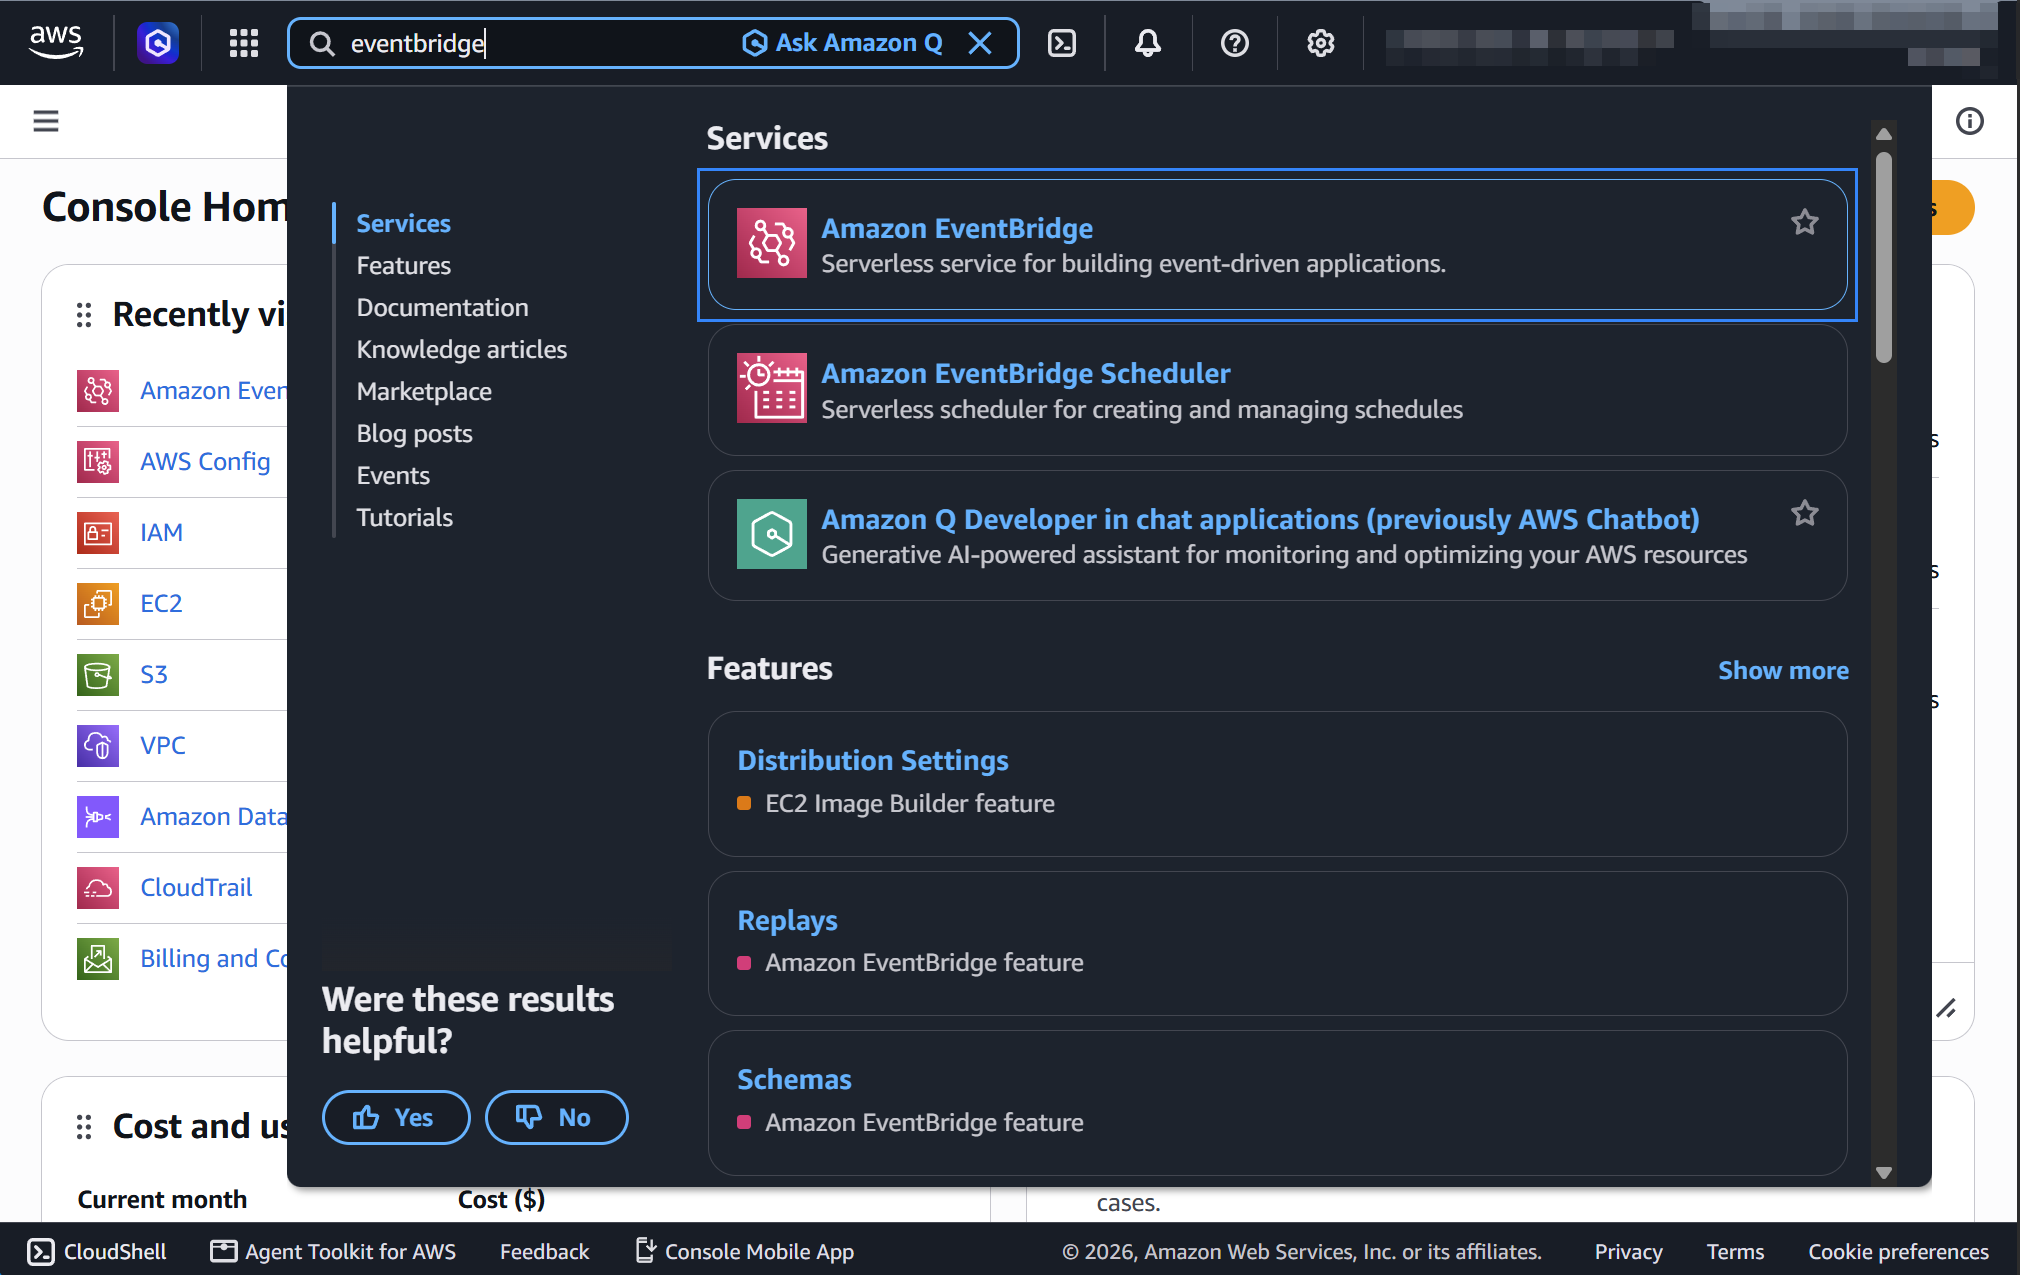
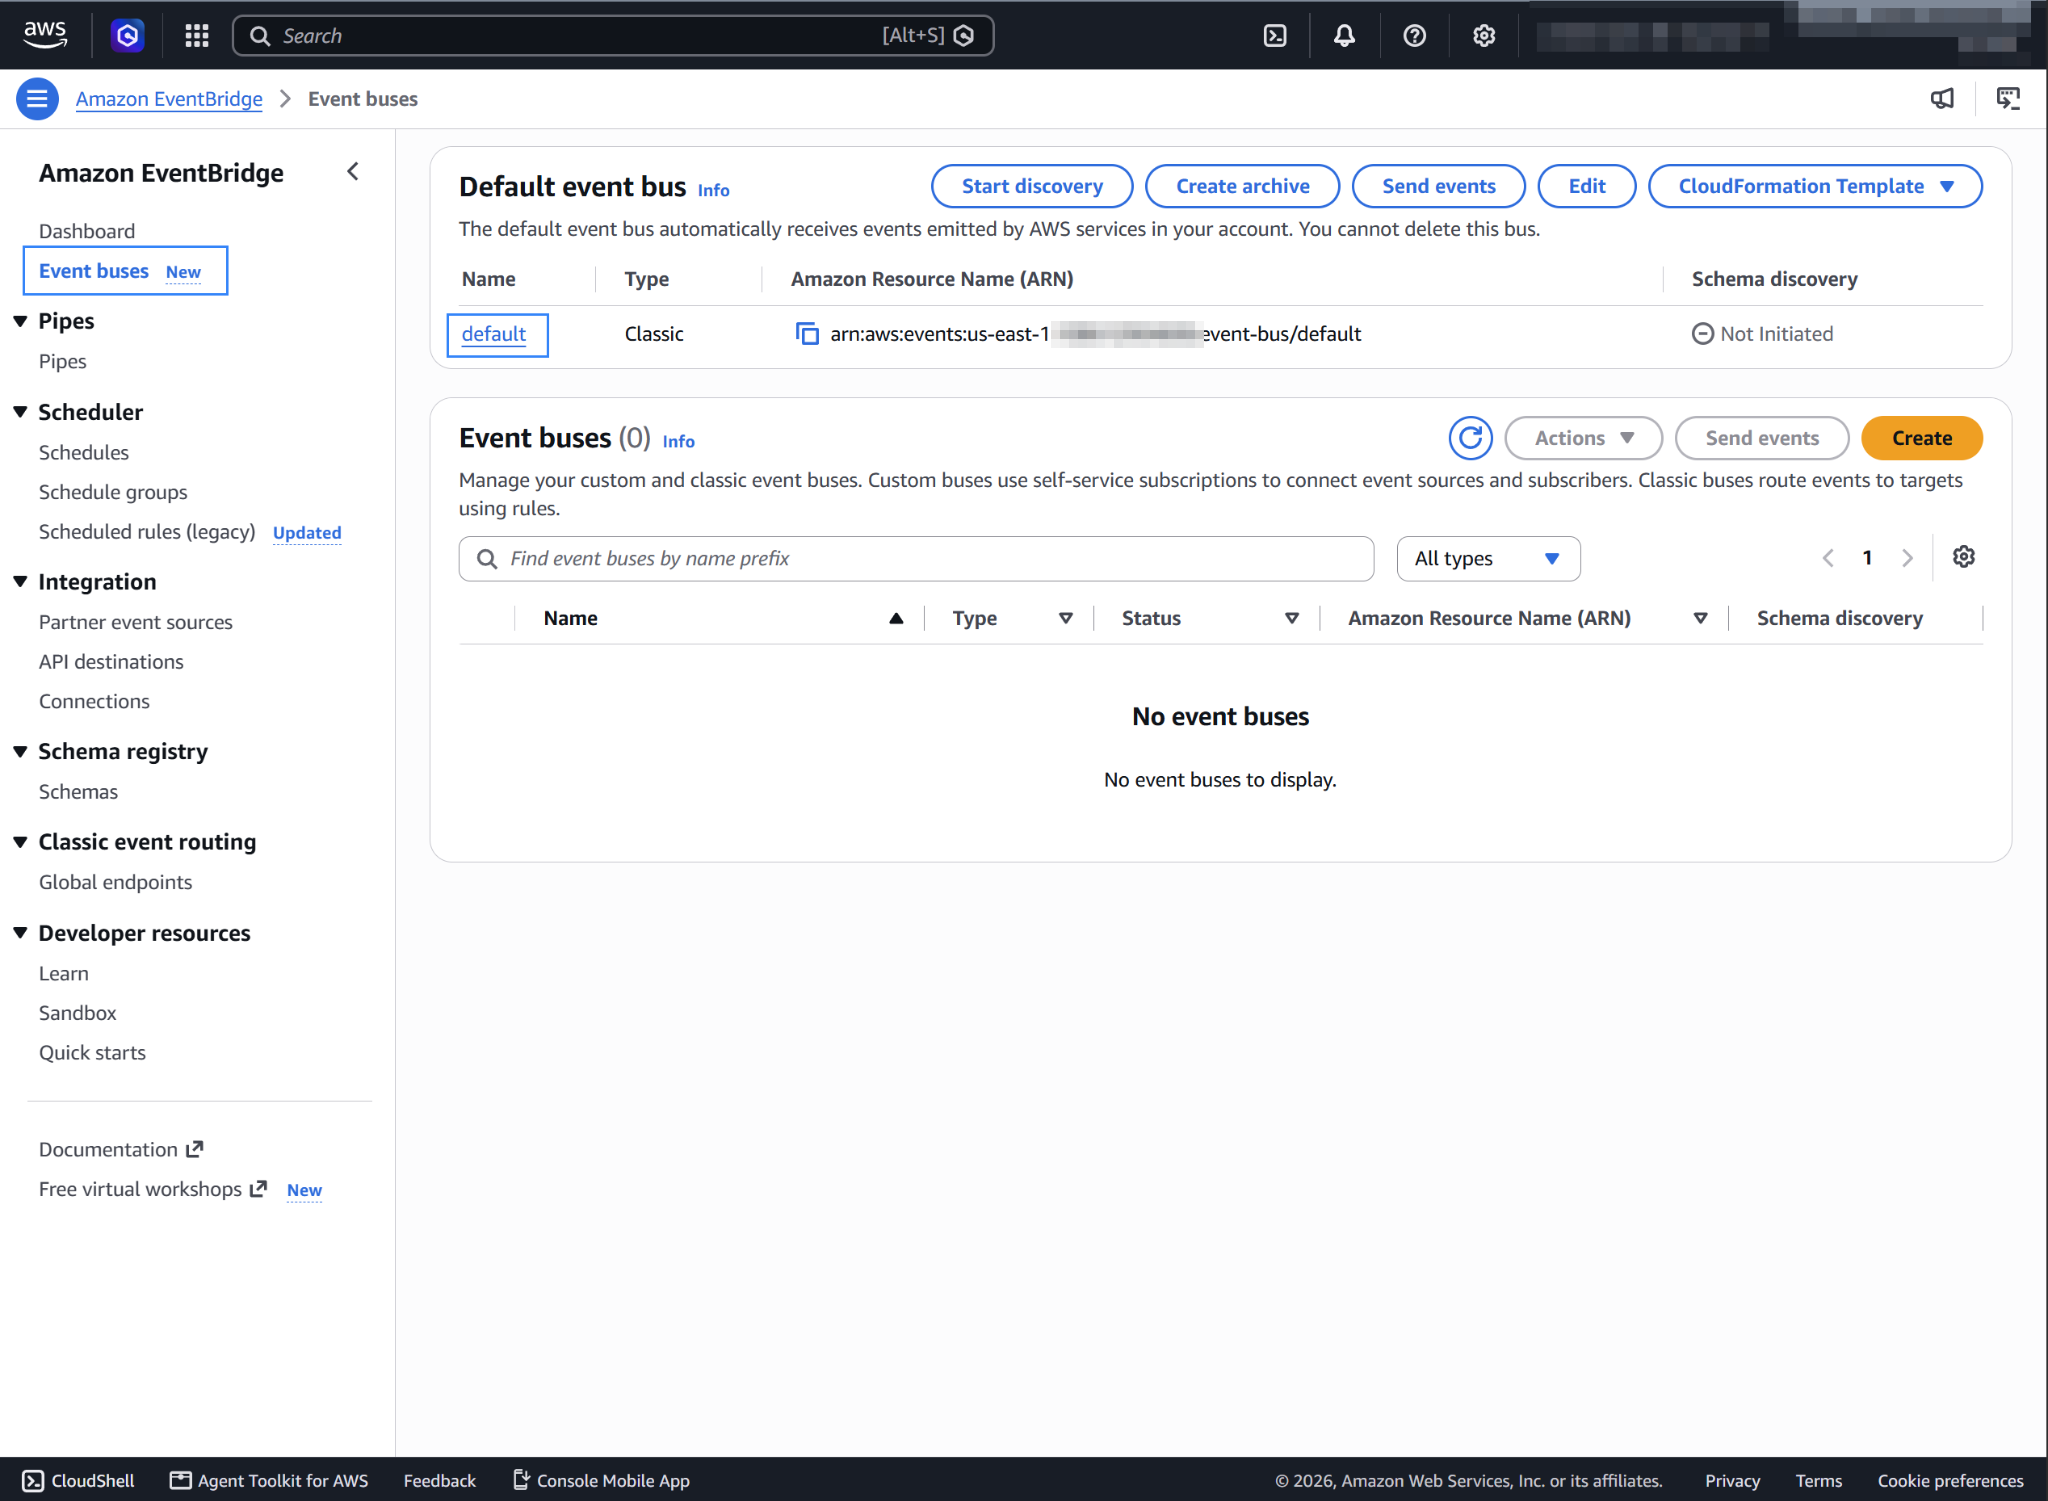
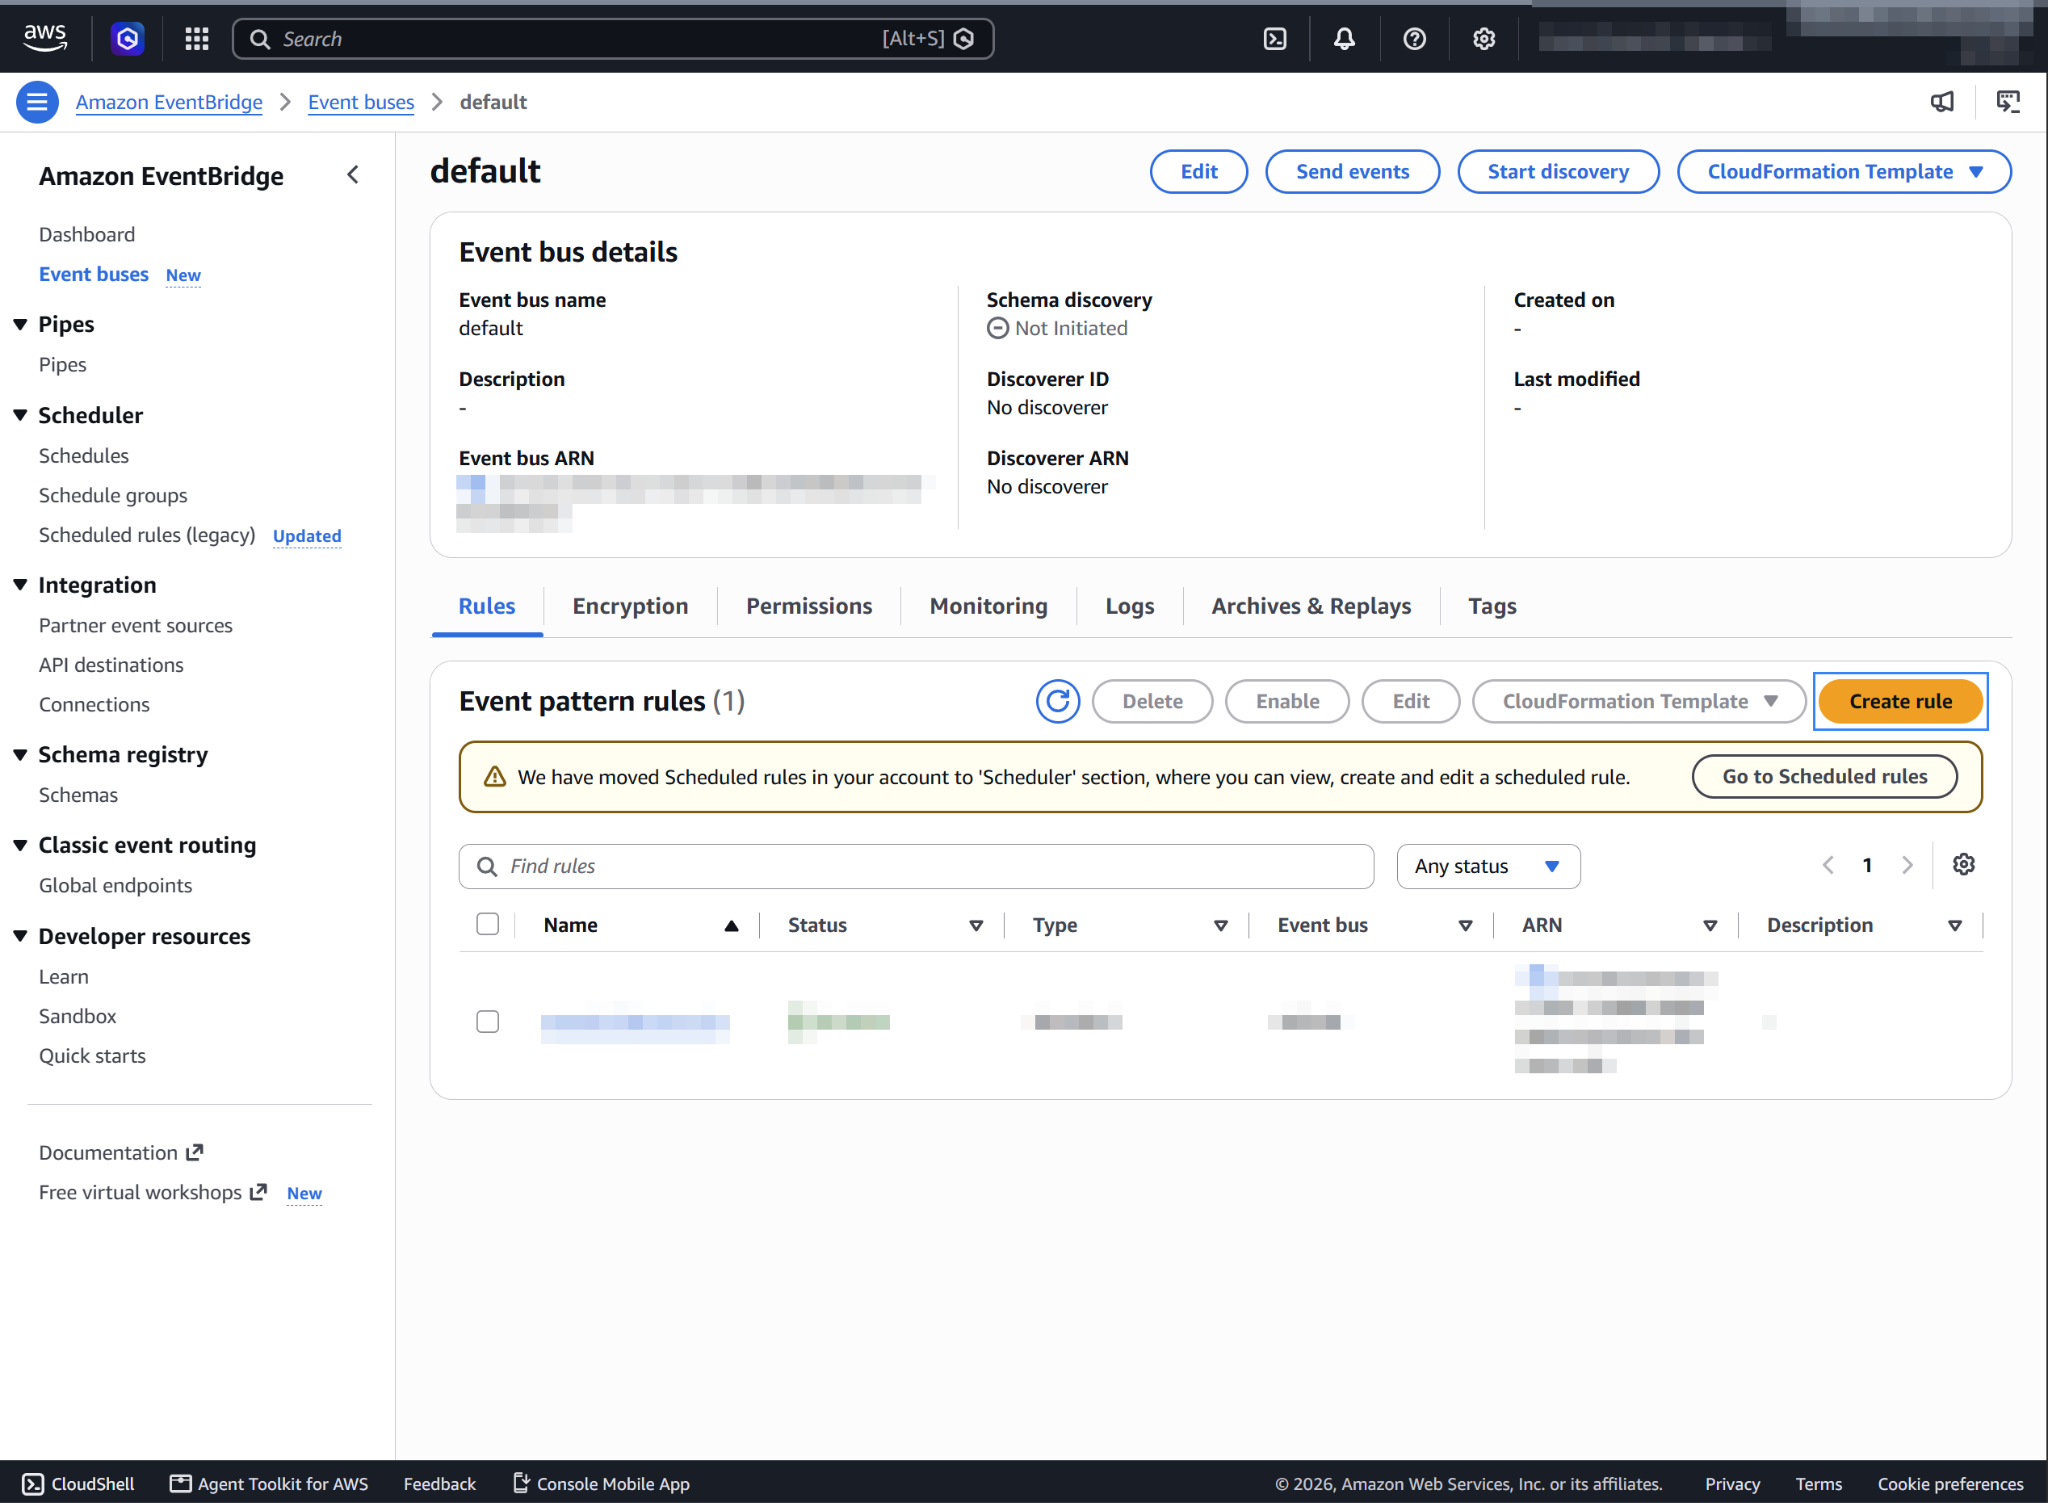
Select Event buses, under Default event bus, click default, then click Create rule.
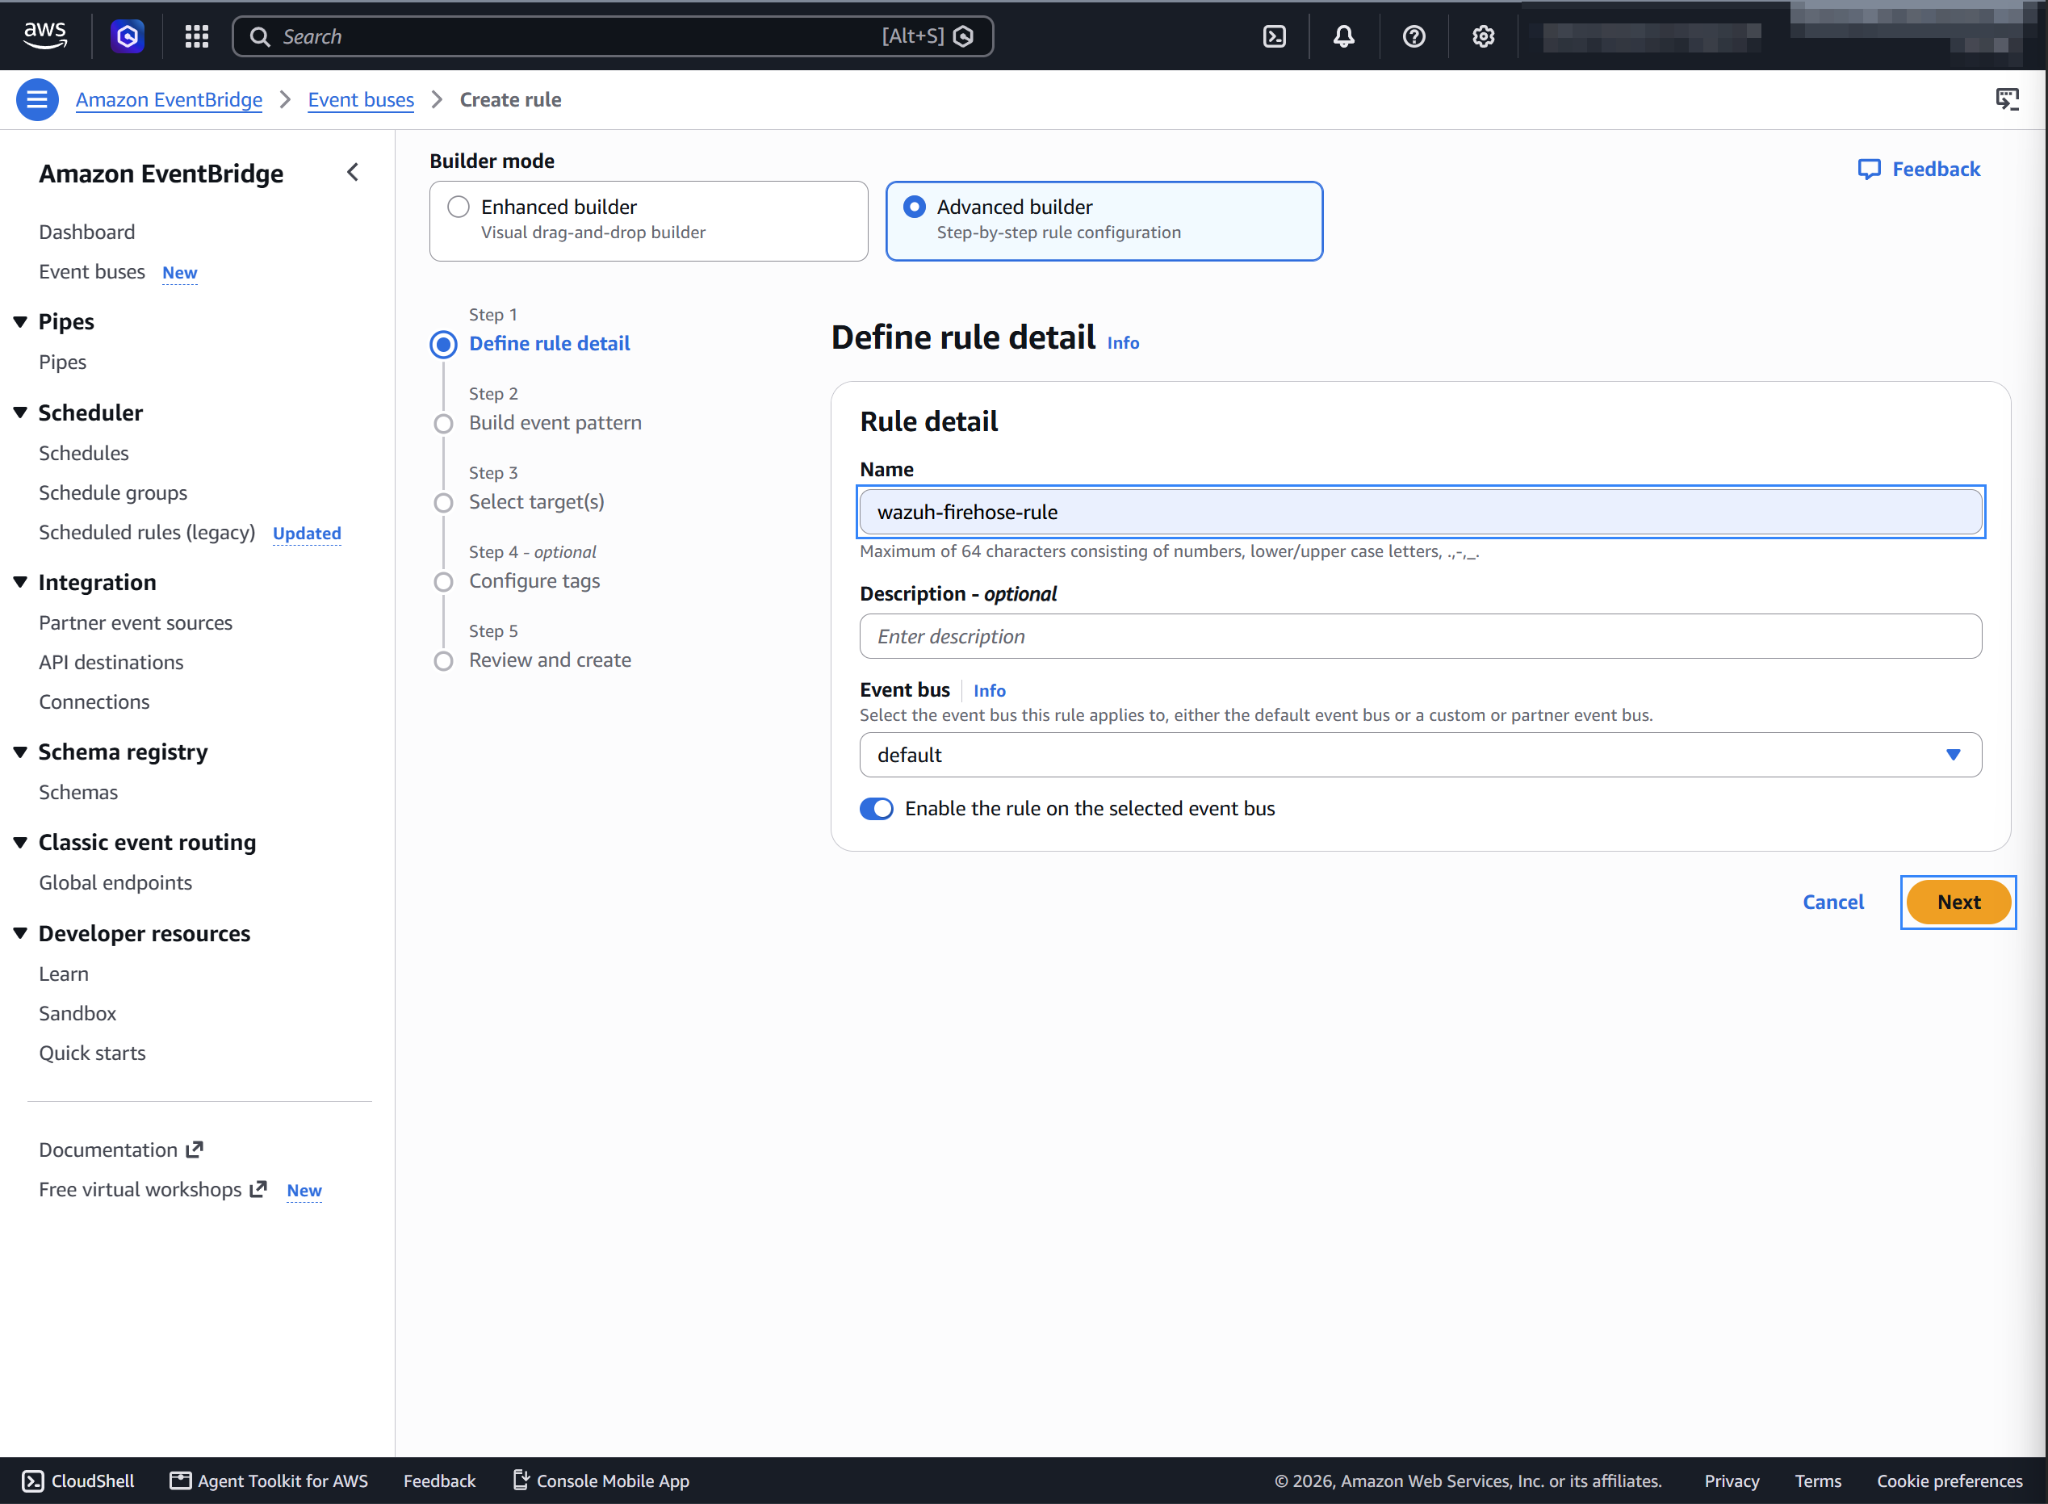
Select Advanced builder, assign a name to the EventBridge rule, and click Next.
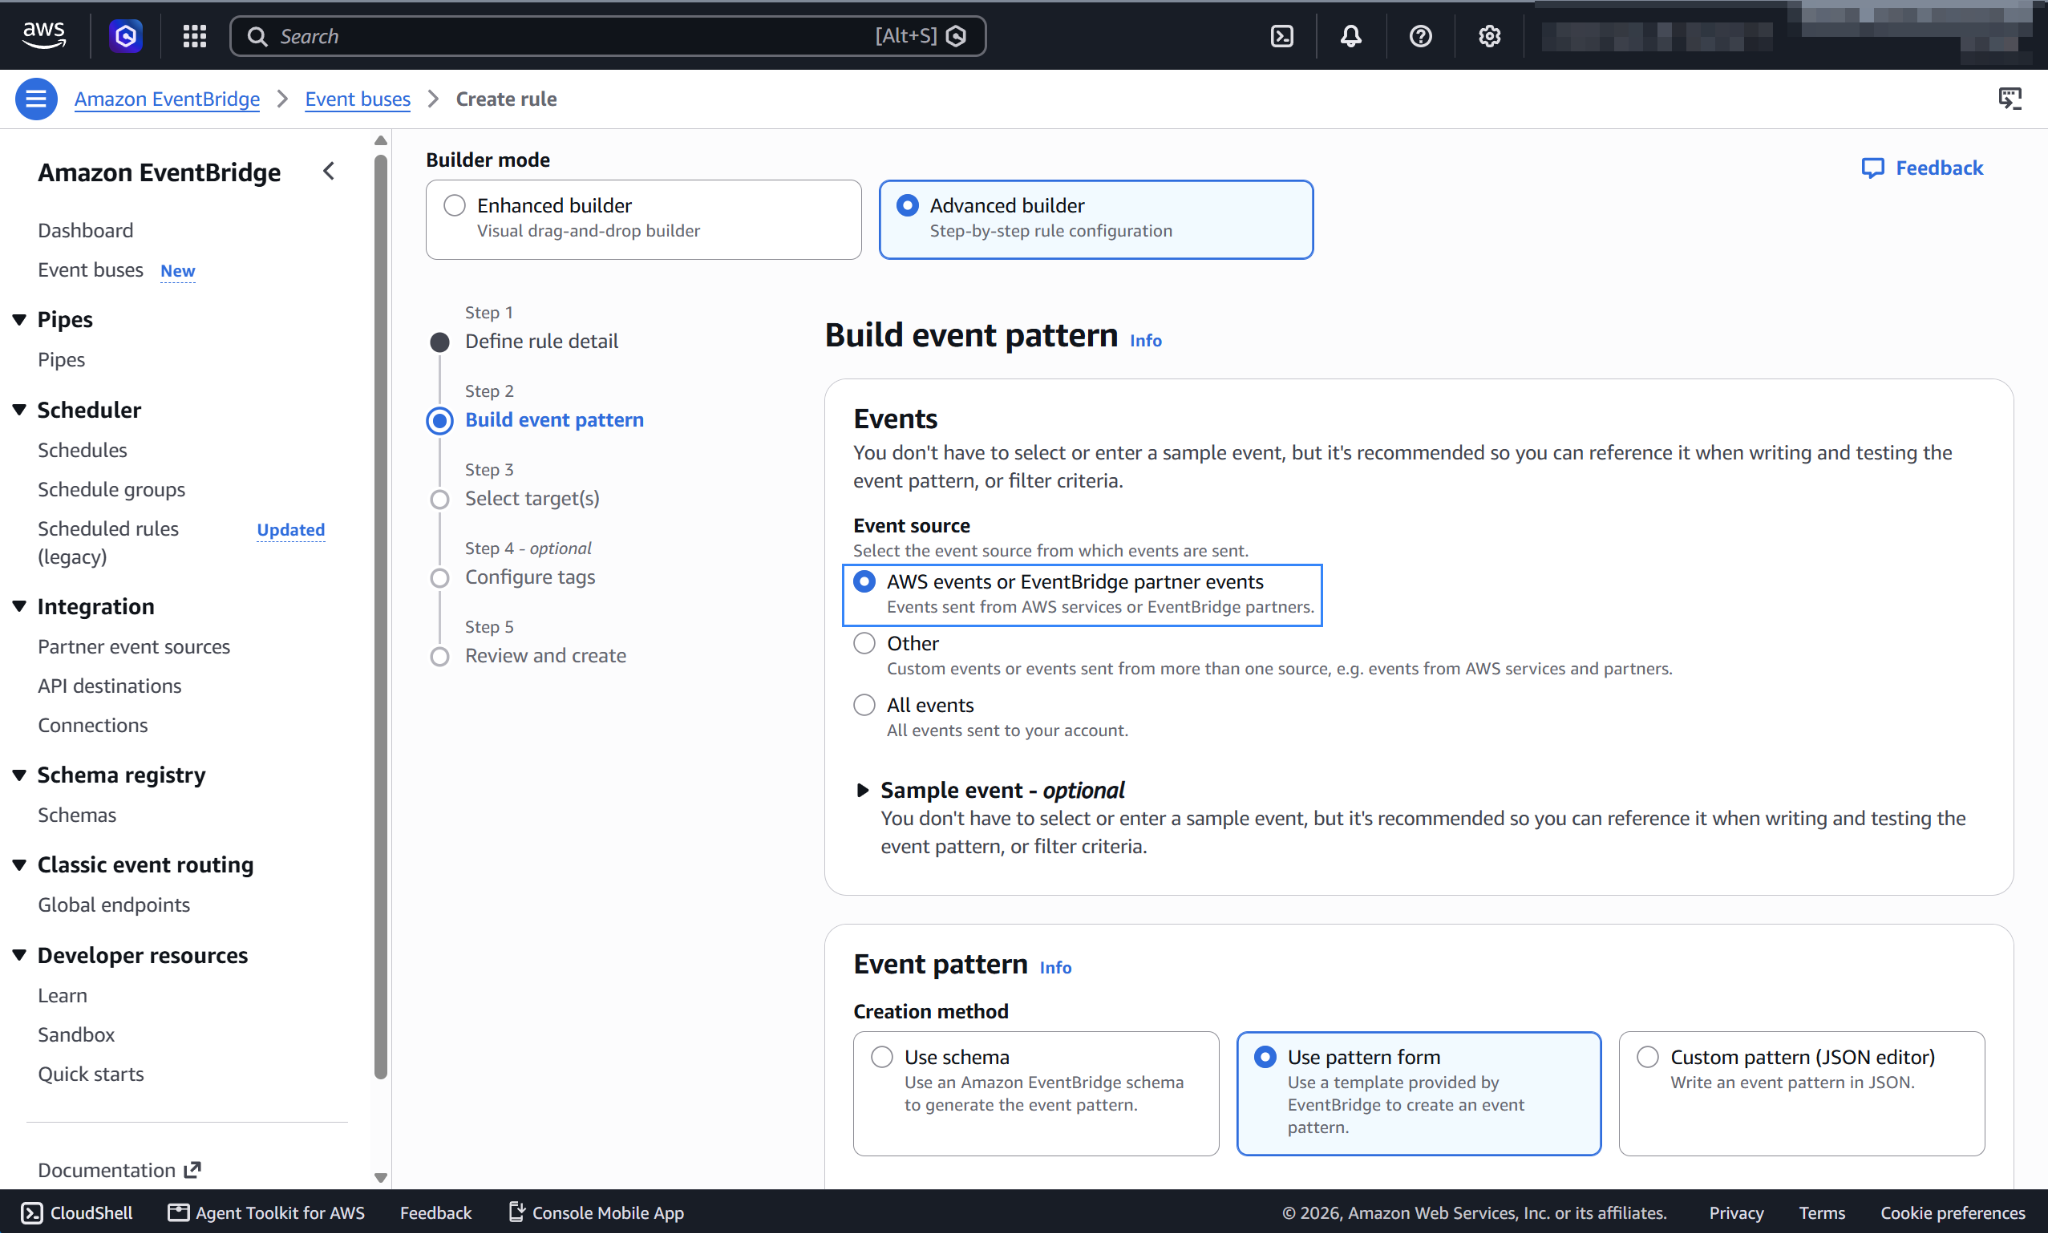
In the Build event pattern section, choose AWS events or EventBridge partner events as Event source.
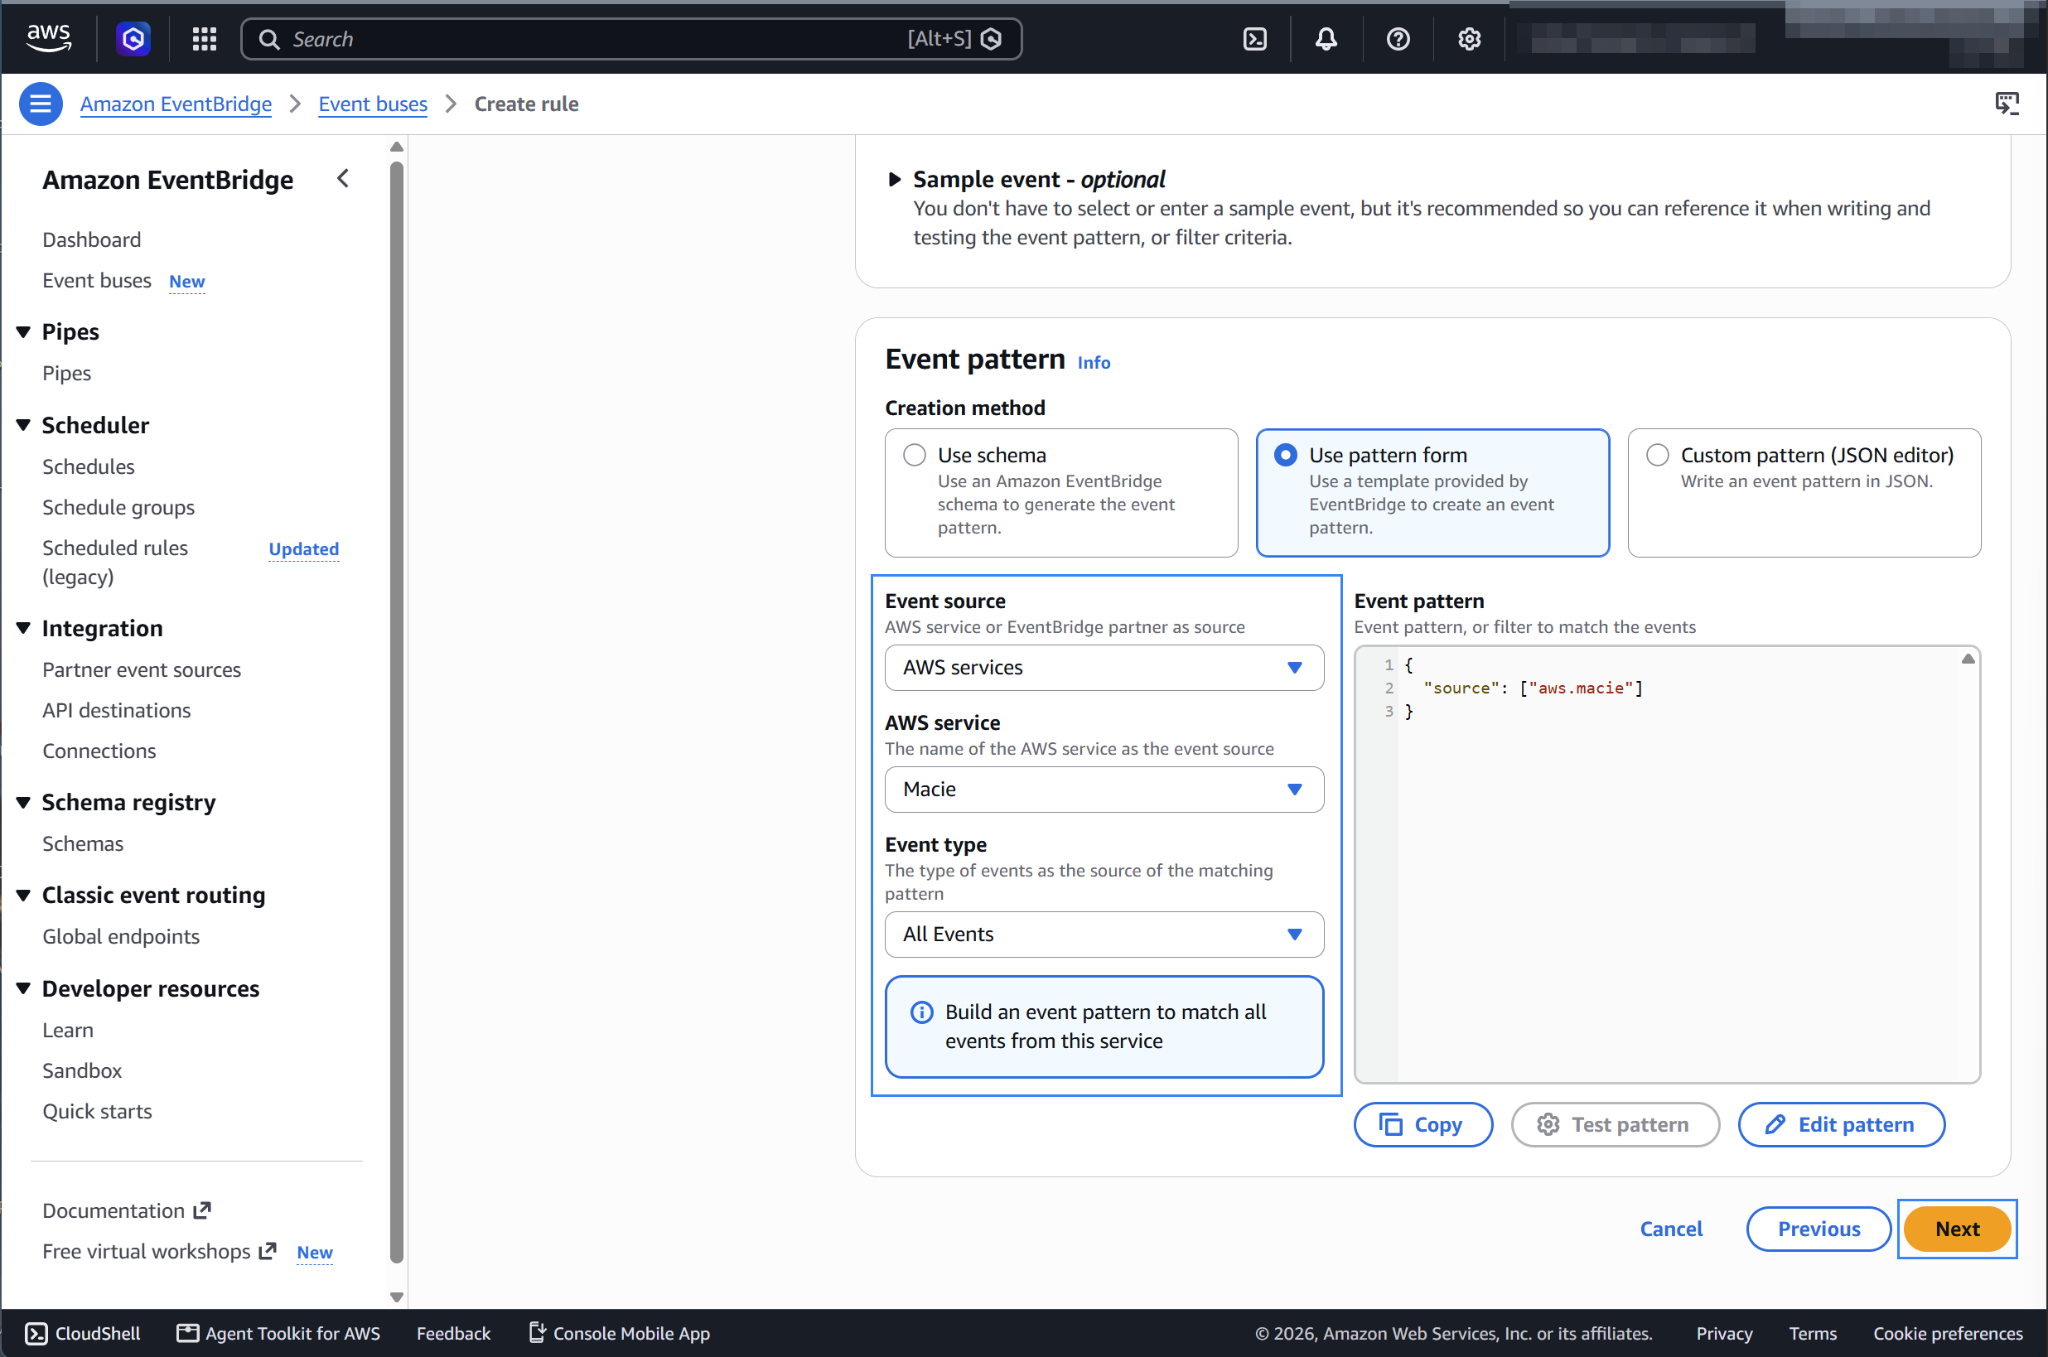
In the Event pattern section, choose AWS services as Event source, Macie as AWS service, and All Events as Event type. Click Next to apply the configuration.
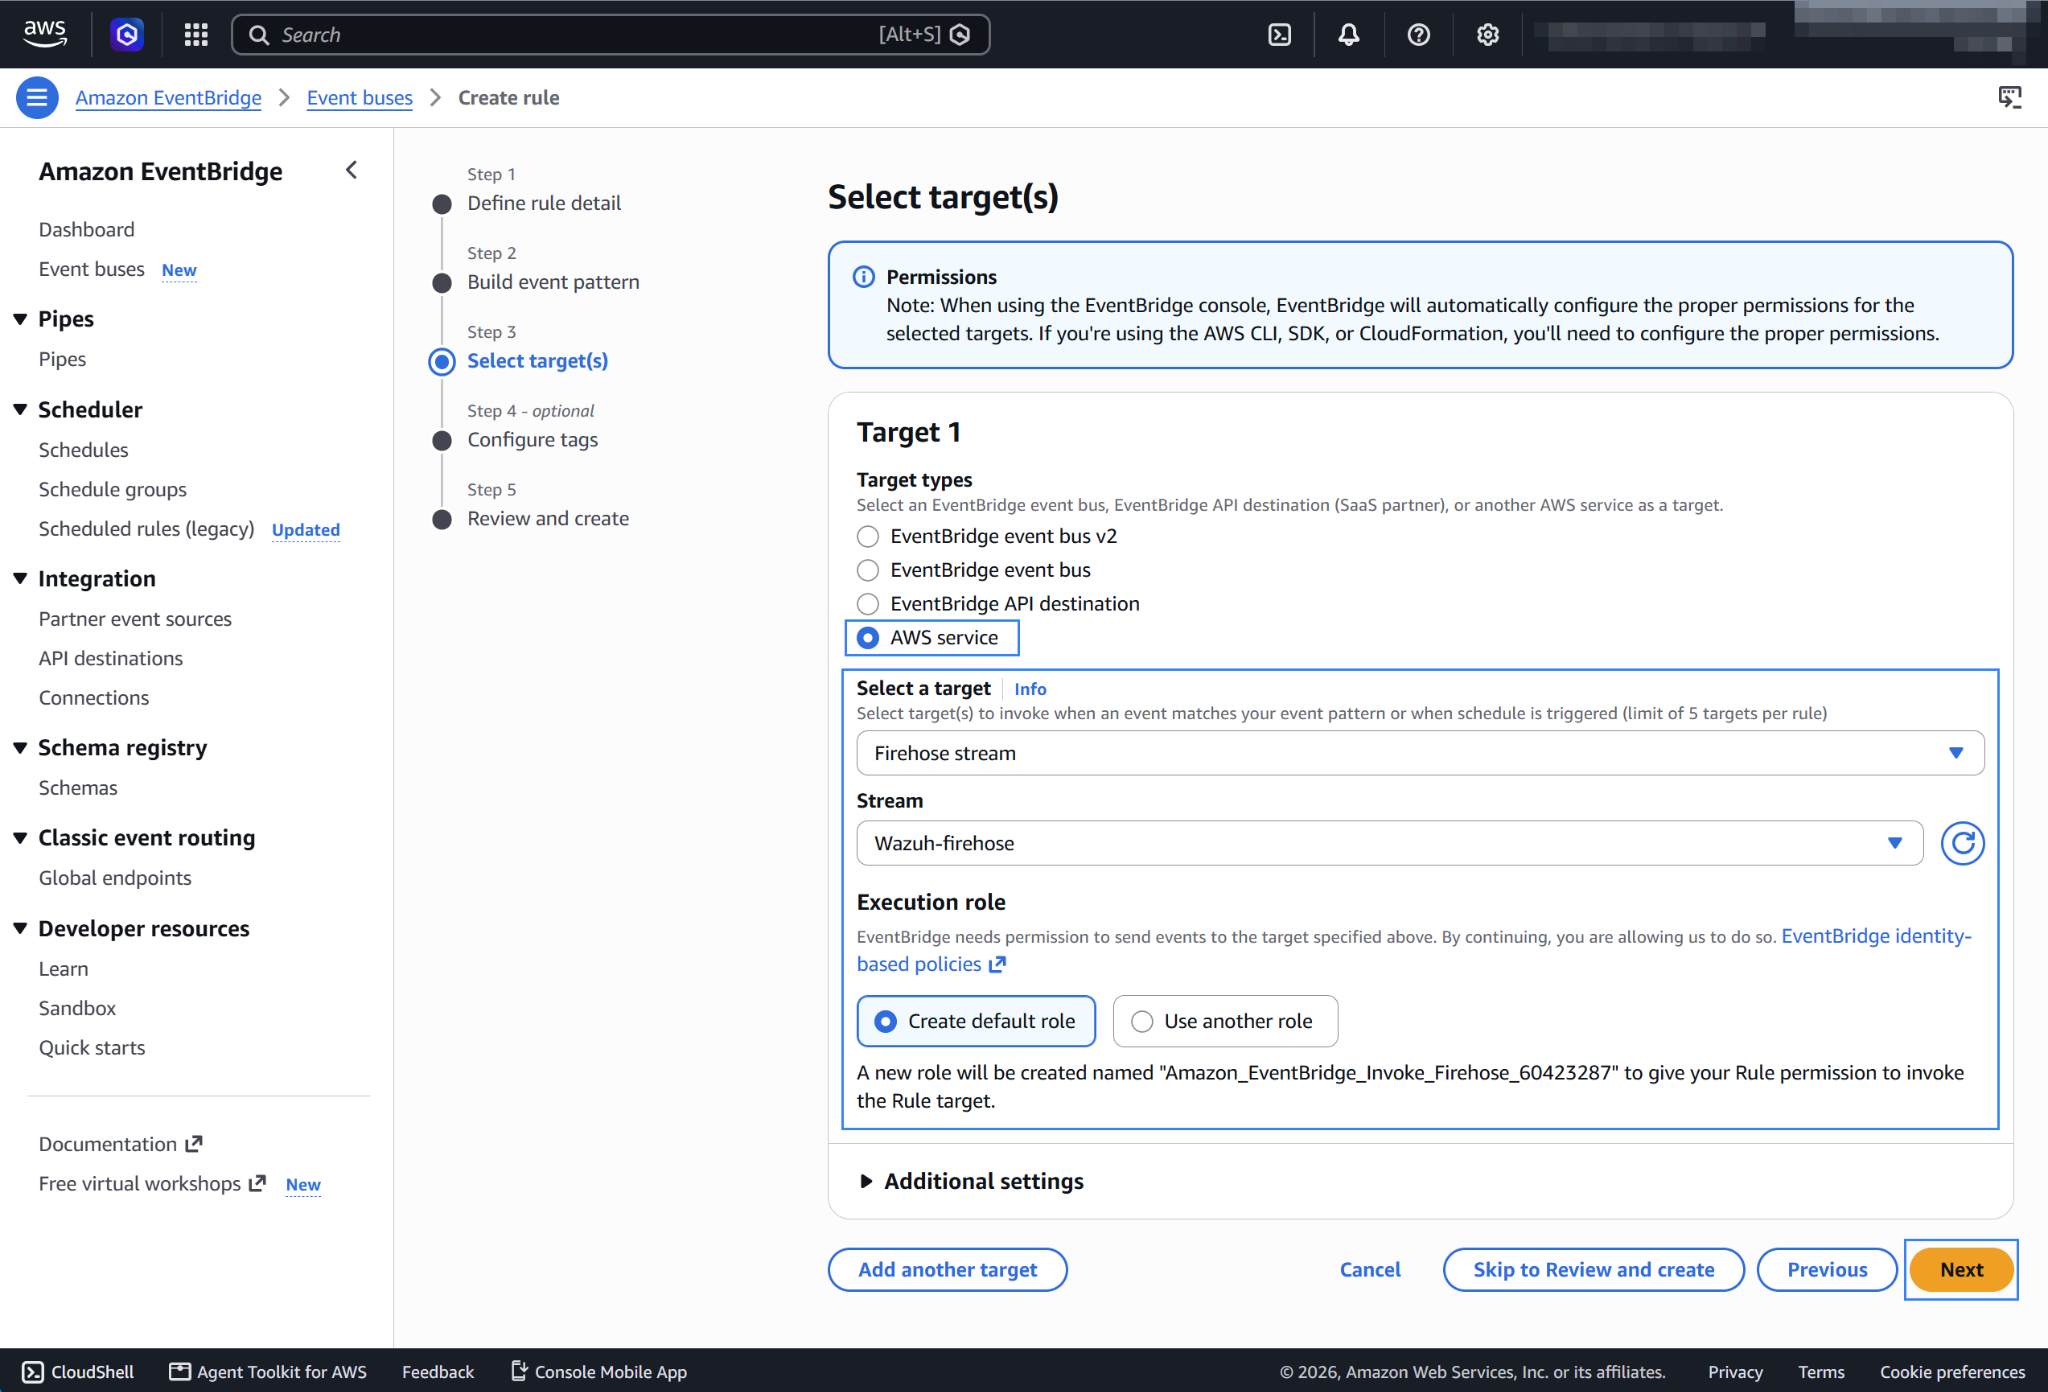
Under Select a target, choose Firehose stream and select the stream created previously. Also, create a new role to access the delivery stream. Click Next to apply the configuration.
Review the configuration and click Create rule.
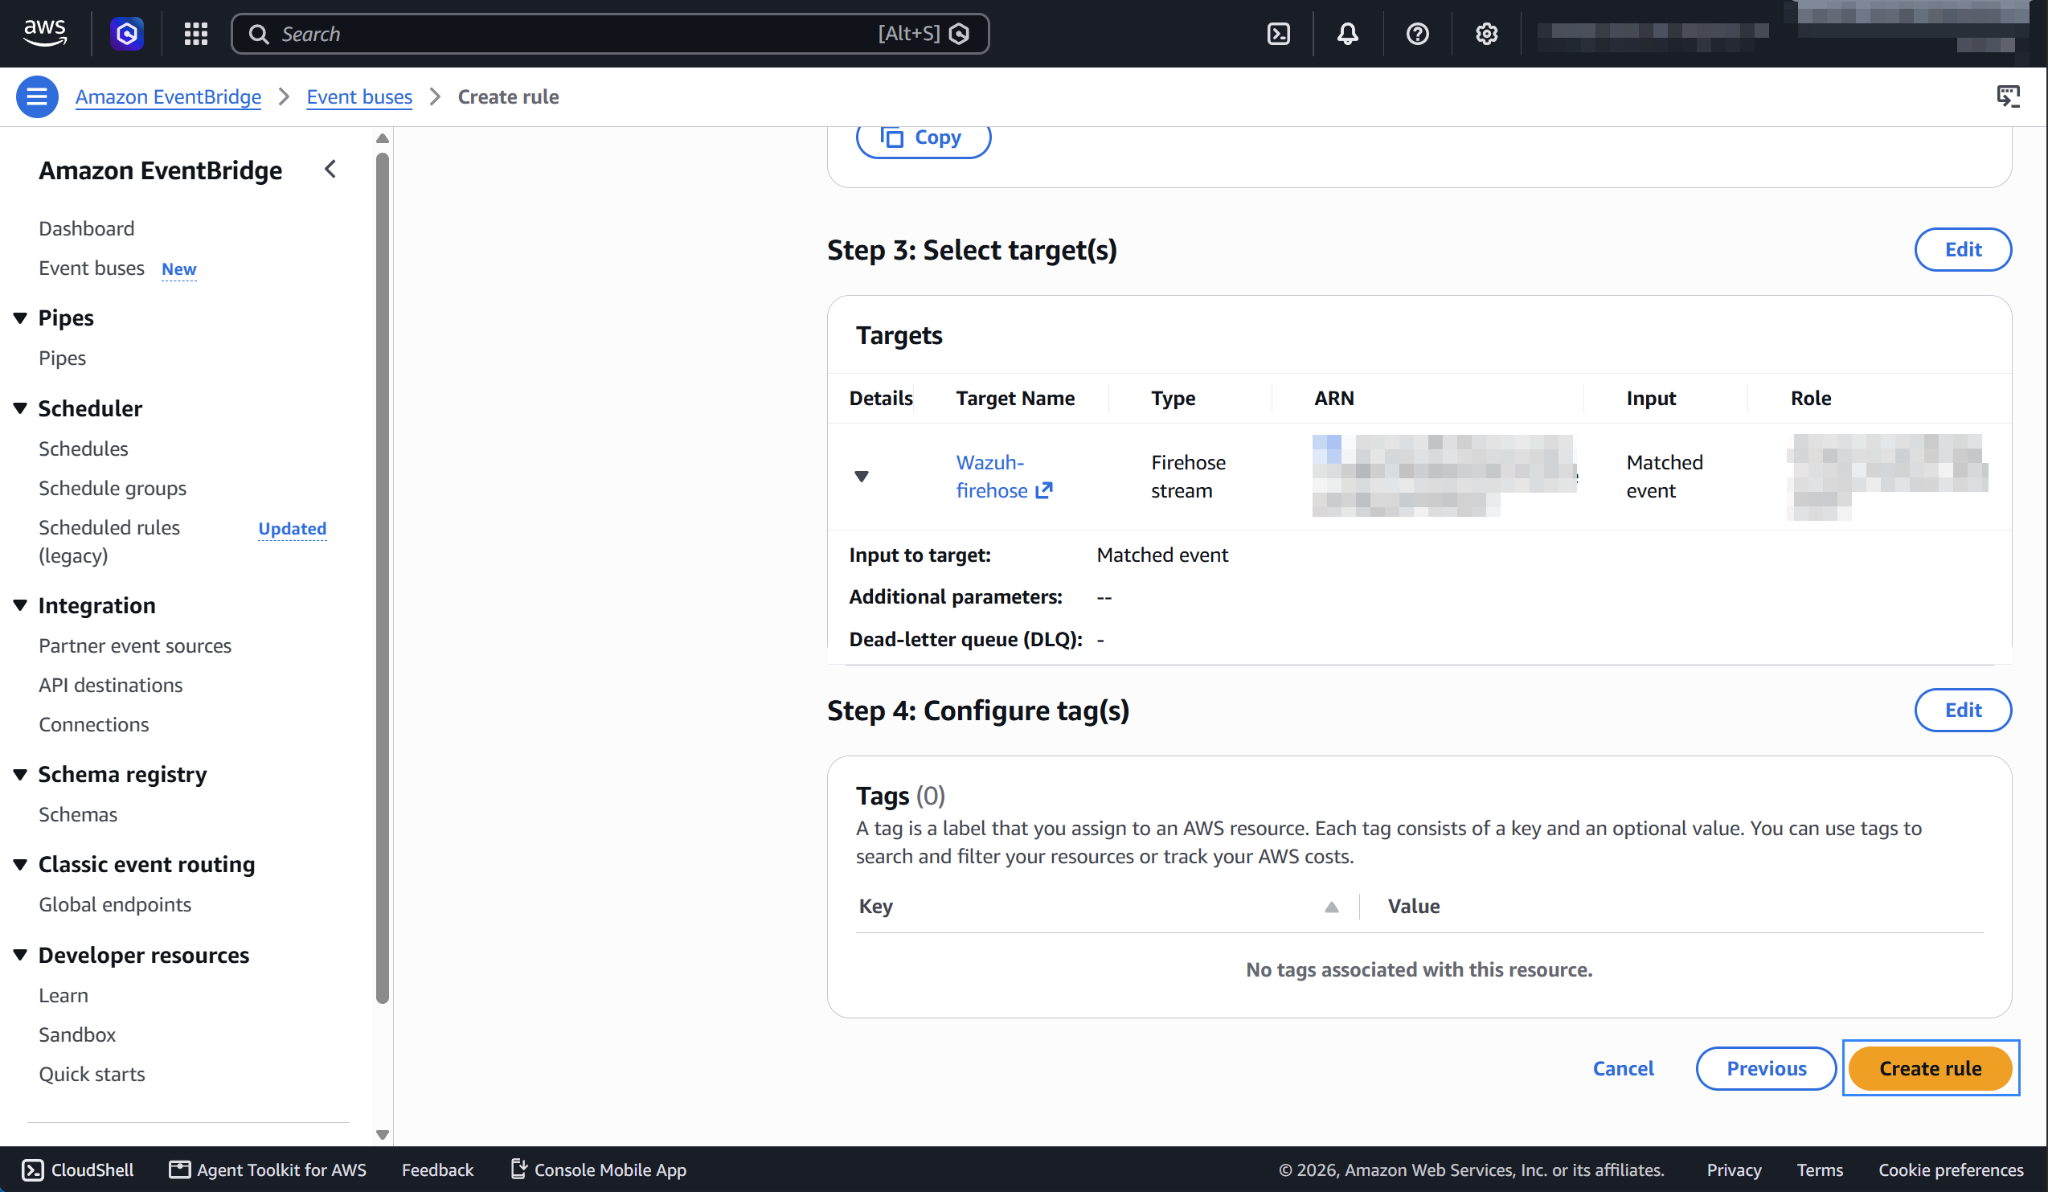
After you create the rule, EventBridge sends each Macie event to the specified S3 bucket. Make sure you enable the Macie service, as described in the next section; otherwise, you won't get any data.
Amazon Macie configuration
On your AWS console, search for
maciein the search bar and click Amazon Macie from the results.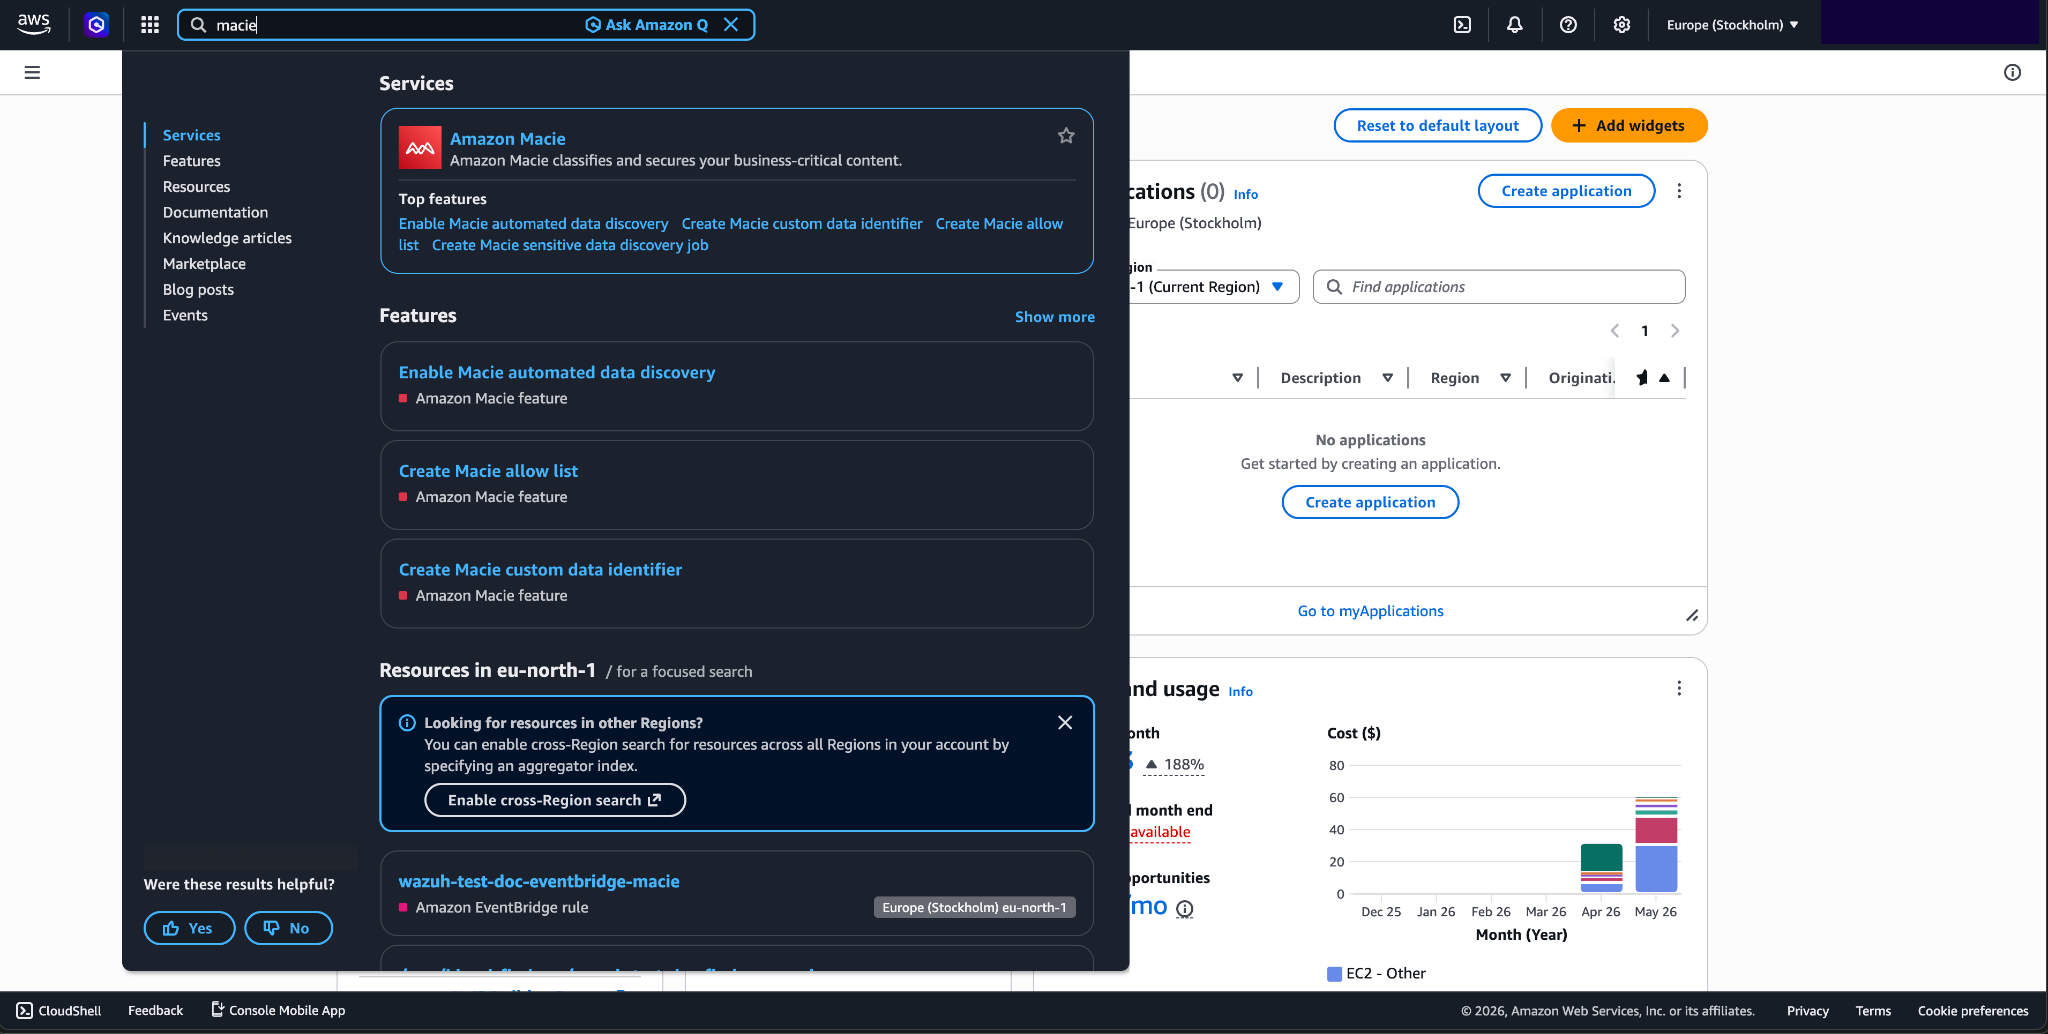
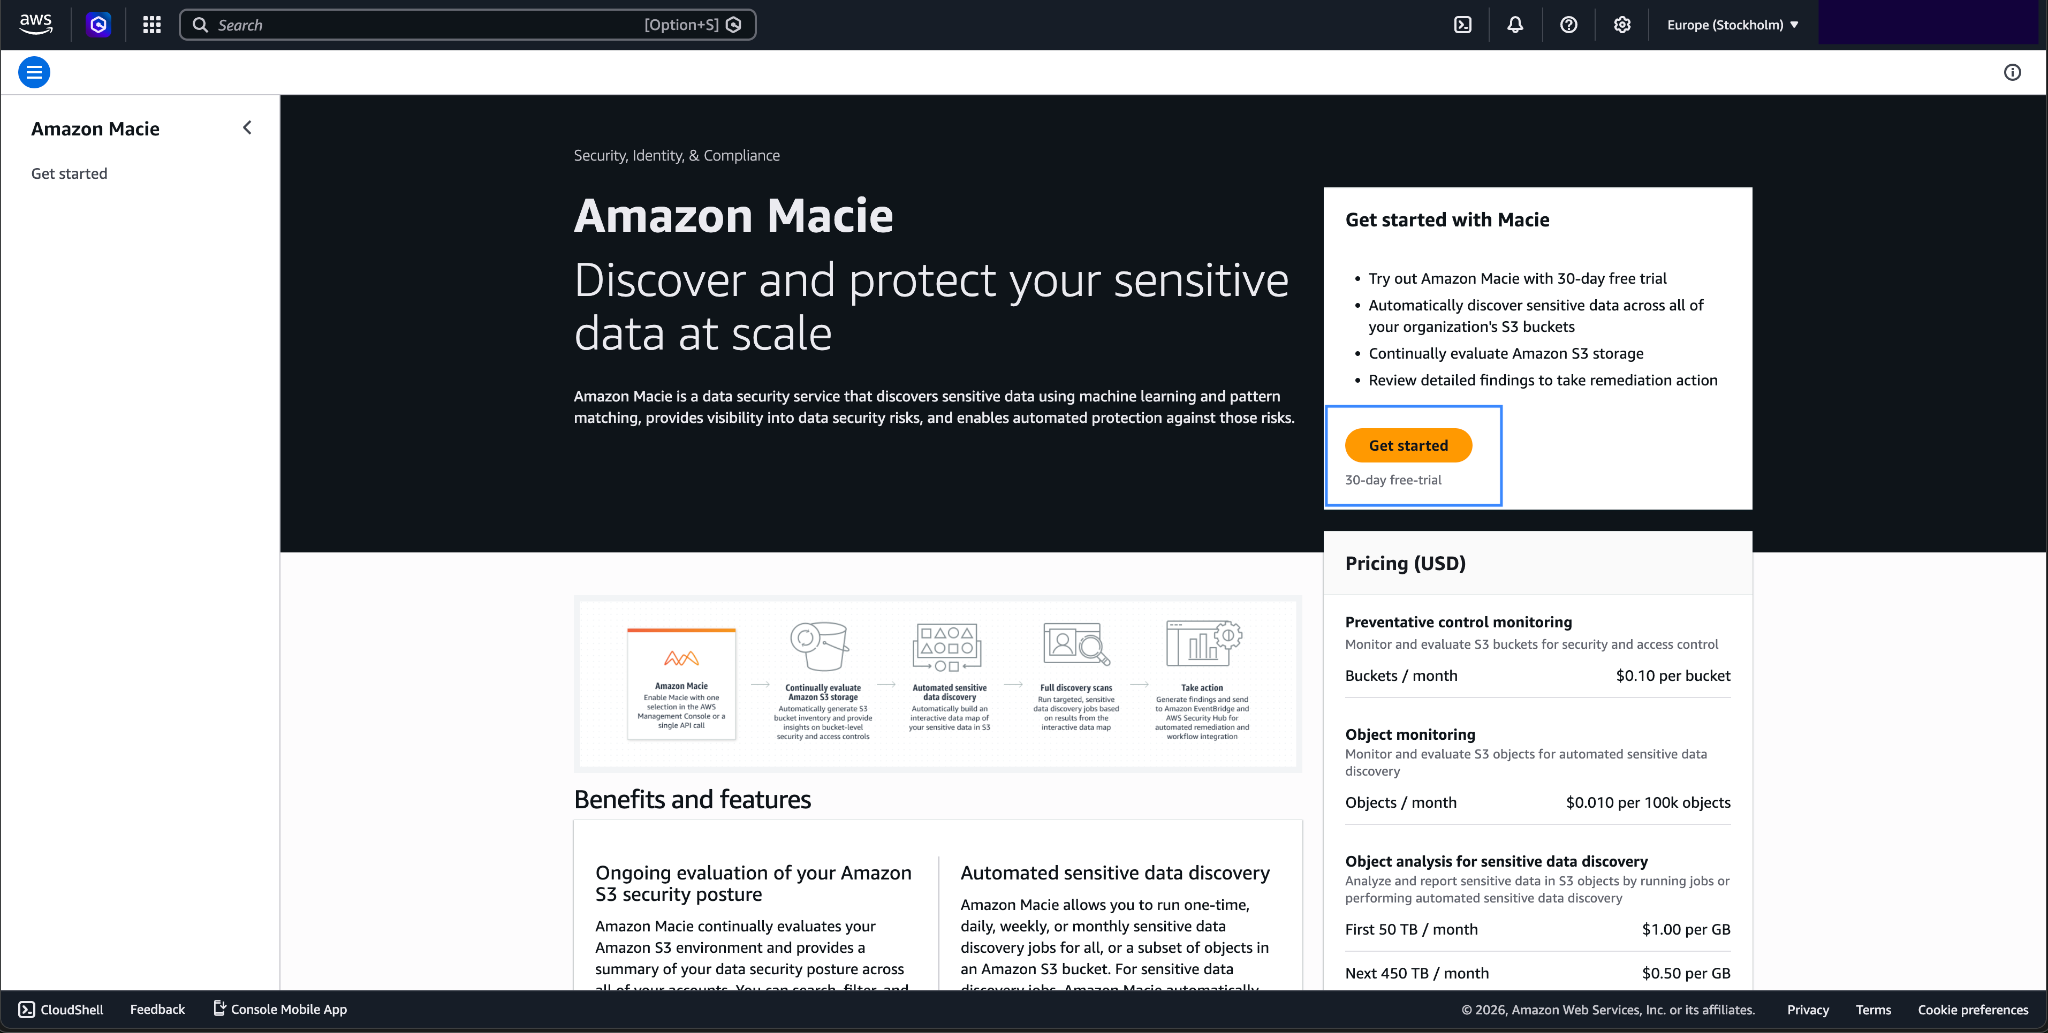
If you're setting up Macie for the first time, click Get started to proceed.
Click Enable Macie to enable the service.
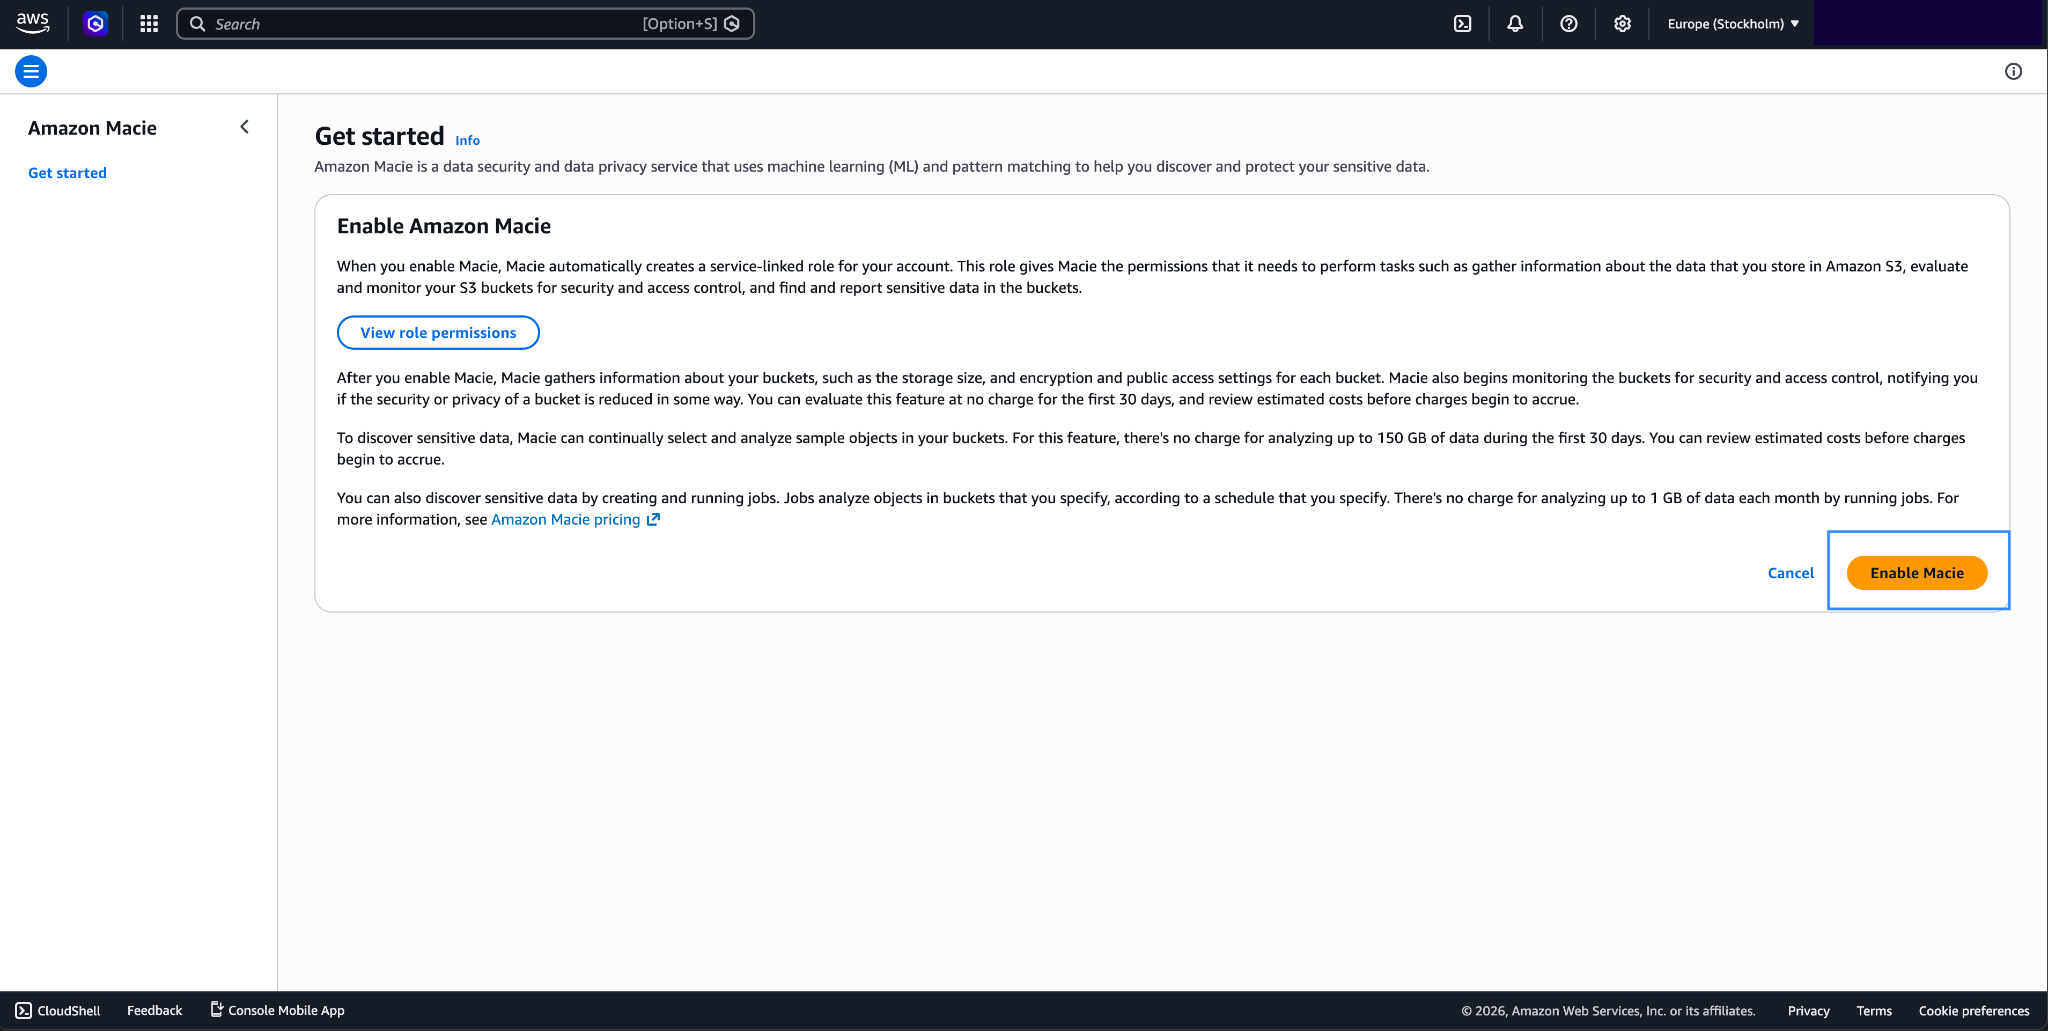
After you enable it, Macie inventories your S3 buckets and evaluates their security and access controls. It analyzes the objects in them only through sensitive data discovery jobs or automated sensitive data discovery. Check the official AWS documentation to learn more about the service.
Create a sensitive data discovery job to generate sensitive data findings. In the Macie navigation pane, select Jobs and click Create job.
Choose Select specific buckets, select the bucket you want to monitor, and follow the wizard to create the job.
In the navigation pane, under Settings, select Automated sensitive data discovery. It's enabled by default for new Macie accounts. If it's disabled, click Enable. Automated discovery samples objects across your buckets, so its first findings can take up to 48 hours.
Macie publishes new findings to Amazon EventBridge, and the EventBridge rule forwards them to the S3 bucket.
Policy configuration
Follow the creating an AWS policy guide to create a policy using the Amazon Web Services console.
The policies below follow the principle of least privilege, so they give the AWS IAM user only the minimum permissions it needs.
To allow an AWS user to use the Wazuh module for AWS with read-only permissions, it must have a policy like the following attached:
{
    "Version": "2012-10-17",
    "Statement": [
        {
            "Sid": "VisualEditor0",
            "Effect": "Allow",
            "Action": [
                "s3:GetObject",
                "s3:ListBucket"
            ],
            "Resource": [
                "arn:aws:s3:::<WAZUH_AWS_BUCKET>/*",
                "arn:aws:s3:::<WAZUH_AWS_BUCKET>"
            ]
        }
    ]
}
To delete the log files after Wazuh collects them, use the following policy instead:
{
    "Version": "2012-10-17",
    "Statement": [
        {
            "Sid": "VisualEditor0",
            "Effect": "Allow",
            "Action": [
                "s3:GetObject",
                "s3:ListBucket",
                "s3:DeleteObject"
            ],
            "Resource": [
                "arn:aws:s3:::<WAZUH_AWS_BUCKET>/*",
                "arn:aws:s3:::<WAZUH_AWS_BUCKET>"
            ]
        }
    ]
}
Note
<WAZUH_AWS_BUCKET> is a placeholder. Replace it with the actual name of the bucket from which you want to retrieve logs.
Wazuh deletes the log files from the bucket only if you set remove_from_bucket to yes in the bucket configuration. This option is off by default and isn't in the sample configuration, so you need the second policy only if you turn it on.
After creating a policy, you can attach it directly to a user or to a group to which the user belongs. In attaching a policy to an IAM user group, you see how to attach a policy to a group. More information on using other methods is available in the AWS documentation.
Configure Wazuh to process Amazon Macie logs
Make sure that the AWS integrations are enabled on the Wazuh dashboard, as described in Enable AWS integration on the Wazuh dashboard.
Add the following Wazuh module for AWS configuration to the
/var/ossec/etc/ossec.conffile on the Wazuh agent. Replace<WAZUH_AWS_BUCKET>with the name of the S3 bucket. Set the path value to the Firehose stream prefix you entered earlier. If the file already has a<wodle name="aws-s3">block, add only the<bucket>section to it:<wodle name="aws-s3"> <disabled>no</disabled> <interval>10m</interval> <run_on_start>yes</run_on_start> <skip_on_error>yes</skip_on_error> <bucket type="custom"> <name><WAZUH_AWS_BUCKET></name> <path>macie</path> <aws_profile>default</aws_profile> </bucket> </wodle>
Note
This example uses the
aws_profileauthentication parameter. Check the Configure AWS credentials section to learn more about the different authentication options and how to use them.Check the Wazuh module for AWS reference manual to learn more about each setting.
Save the changes and restart the Wazuh agent service to apply the changes:
# systemctl restart wazuh-agent
Macie use case
Amazon S3 (Simple Storage Service) provides secure and reliable storage capacity in the cloud. We recommend that you monitor this service to detect misconfigurations and sensitive data leakage.
The following use case shows Wazuh findings for Amazon Macie.
Sensitive data disclosure in S3 bucket
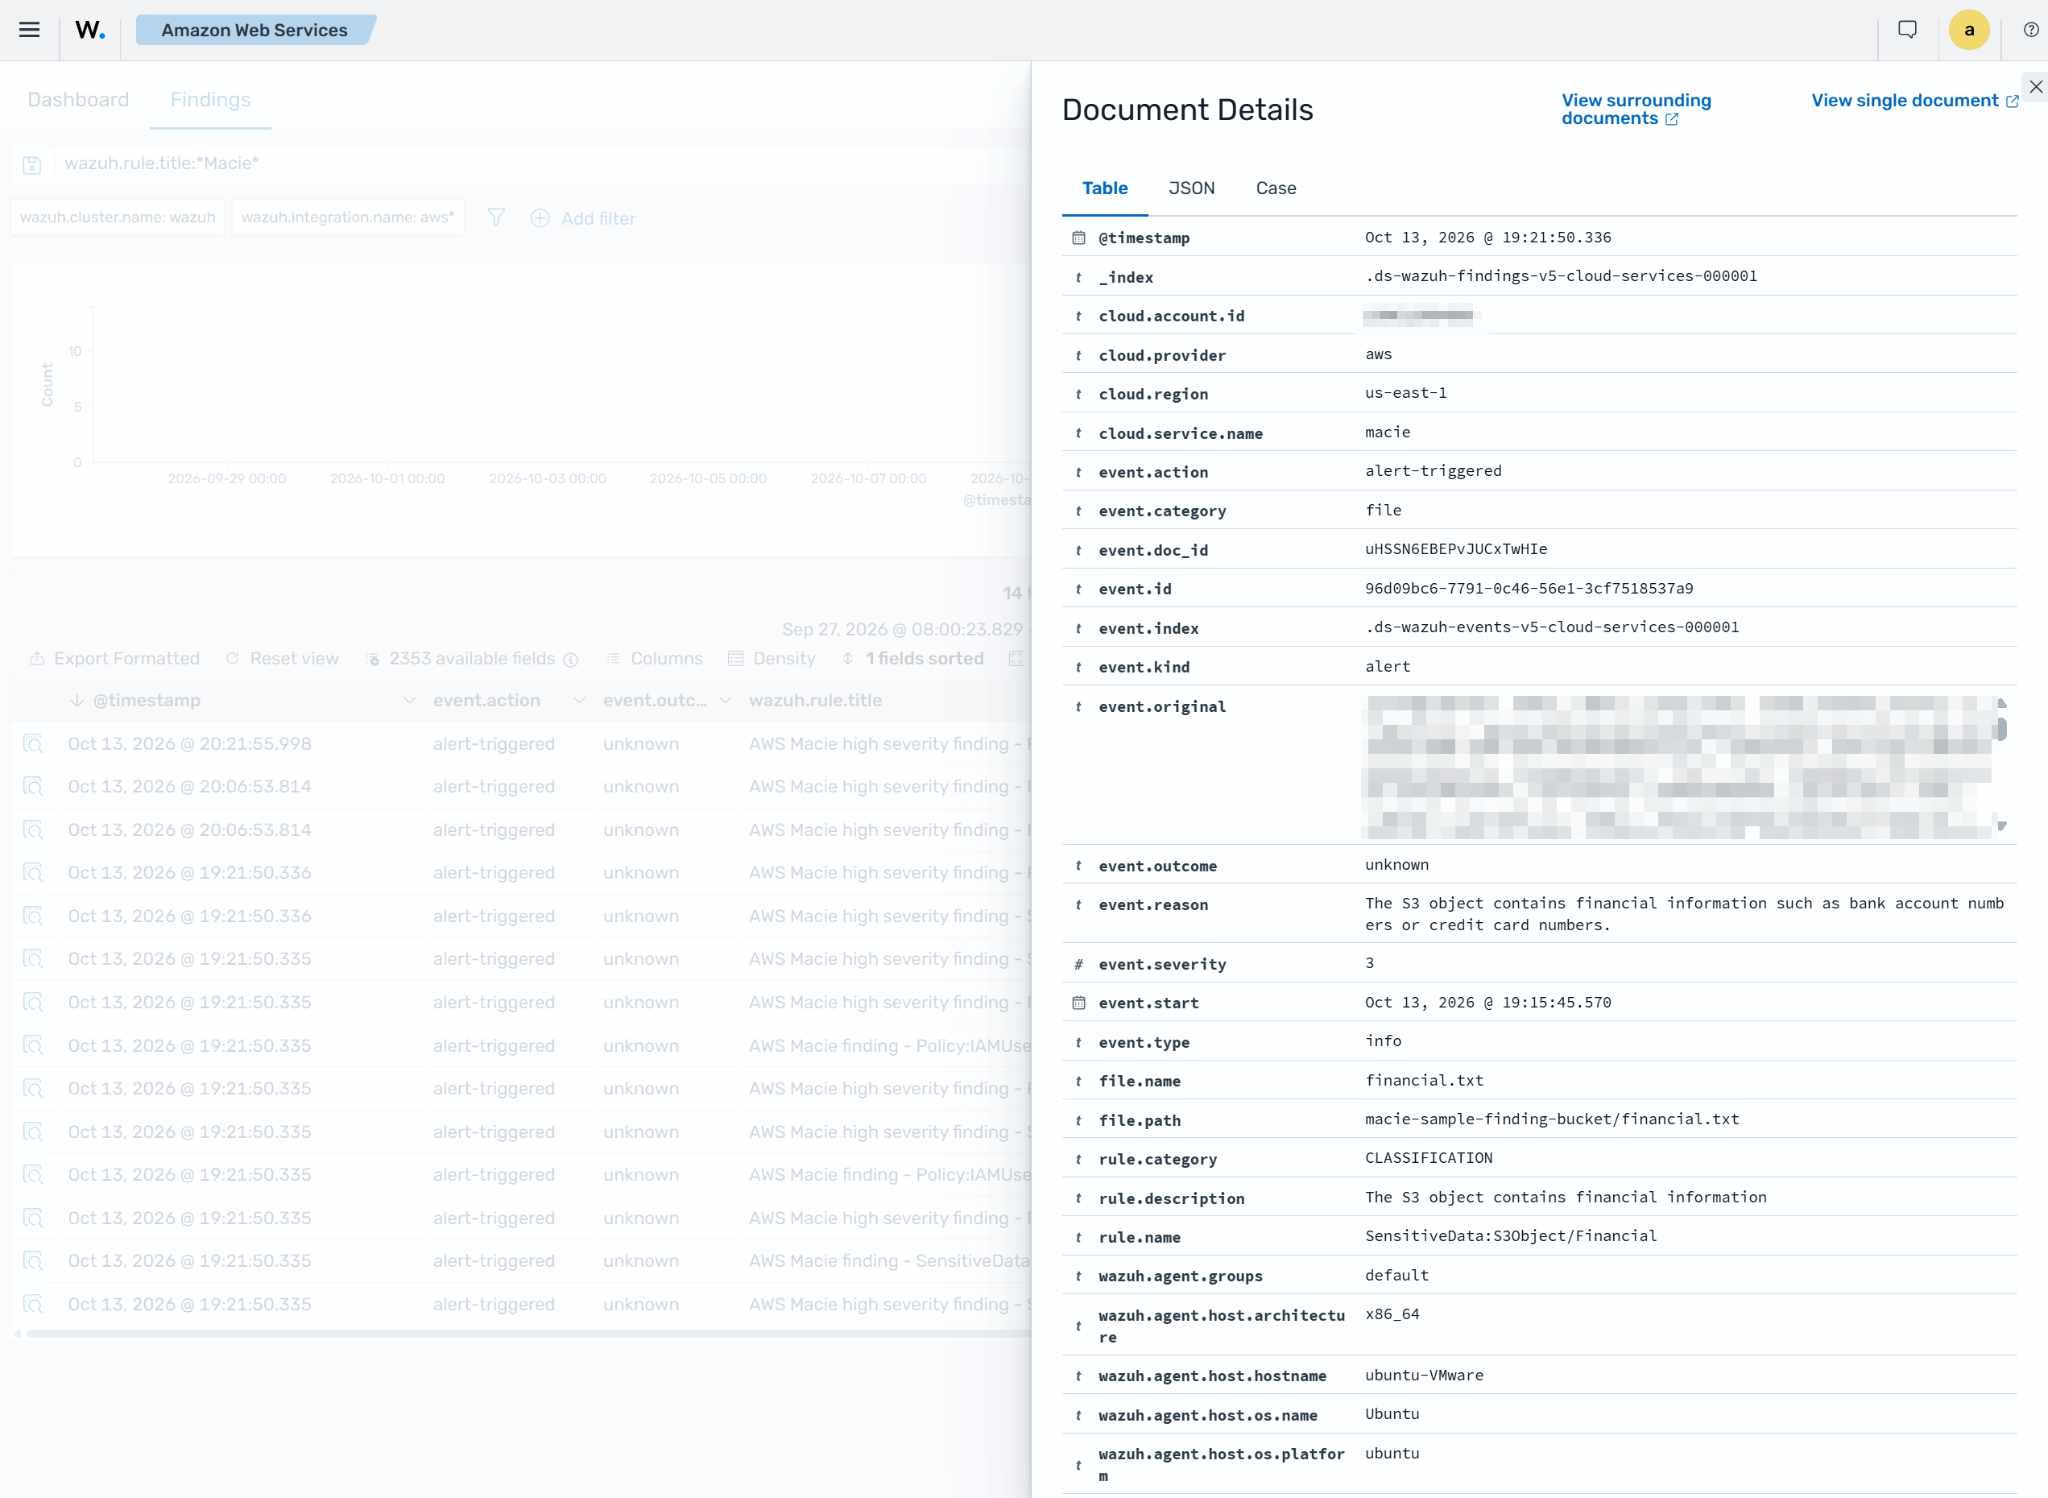
When Macie finds sensitive data, such as financial information, credentials, or personal information, in an S3 bucket, it generates sensitive data findings. Each finding title ends with its Macie finding type, for example, AWS Macie high severity finding - SensitiveData:S3Object/Multiple. Low and medium severity findings are titled AWS Macie finding, followed by the type.
To see them, go to Amazon Web Services > Findings and filter by wazuh.rule.title:*Macie*.
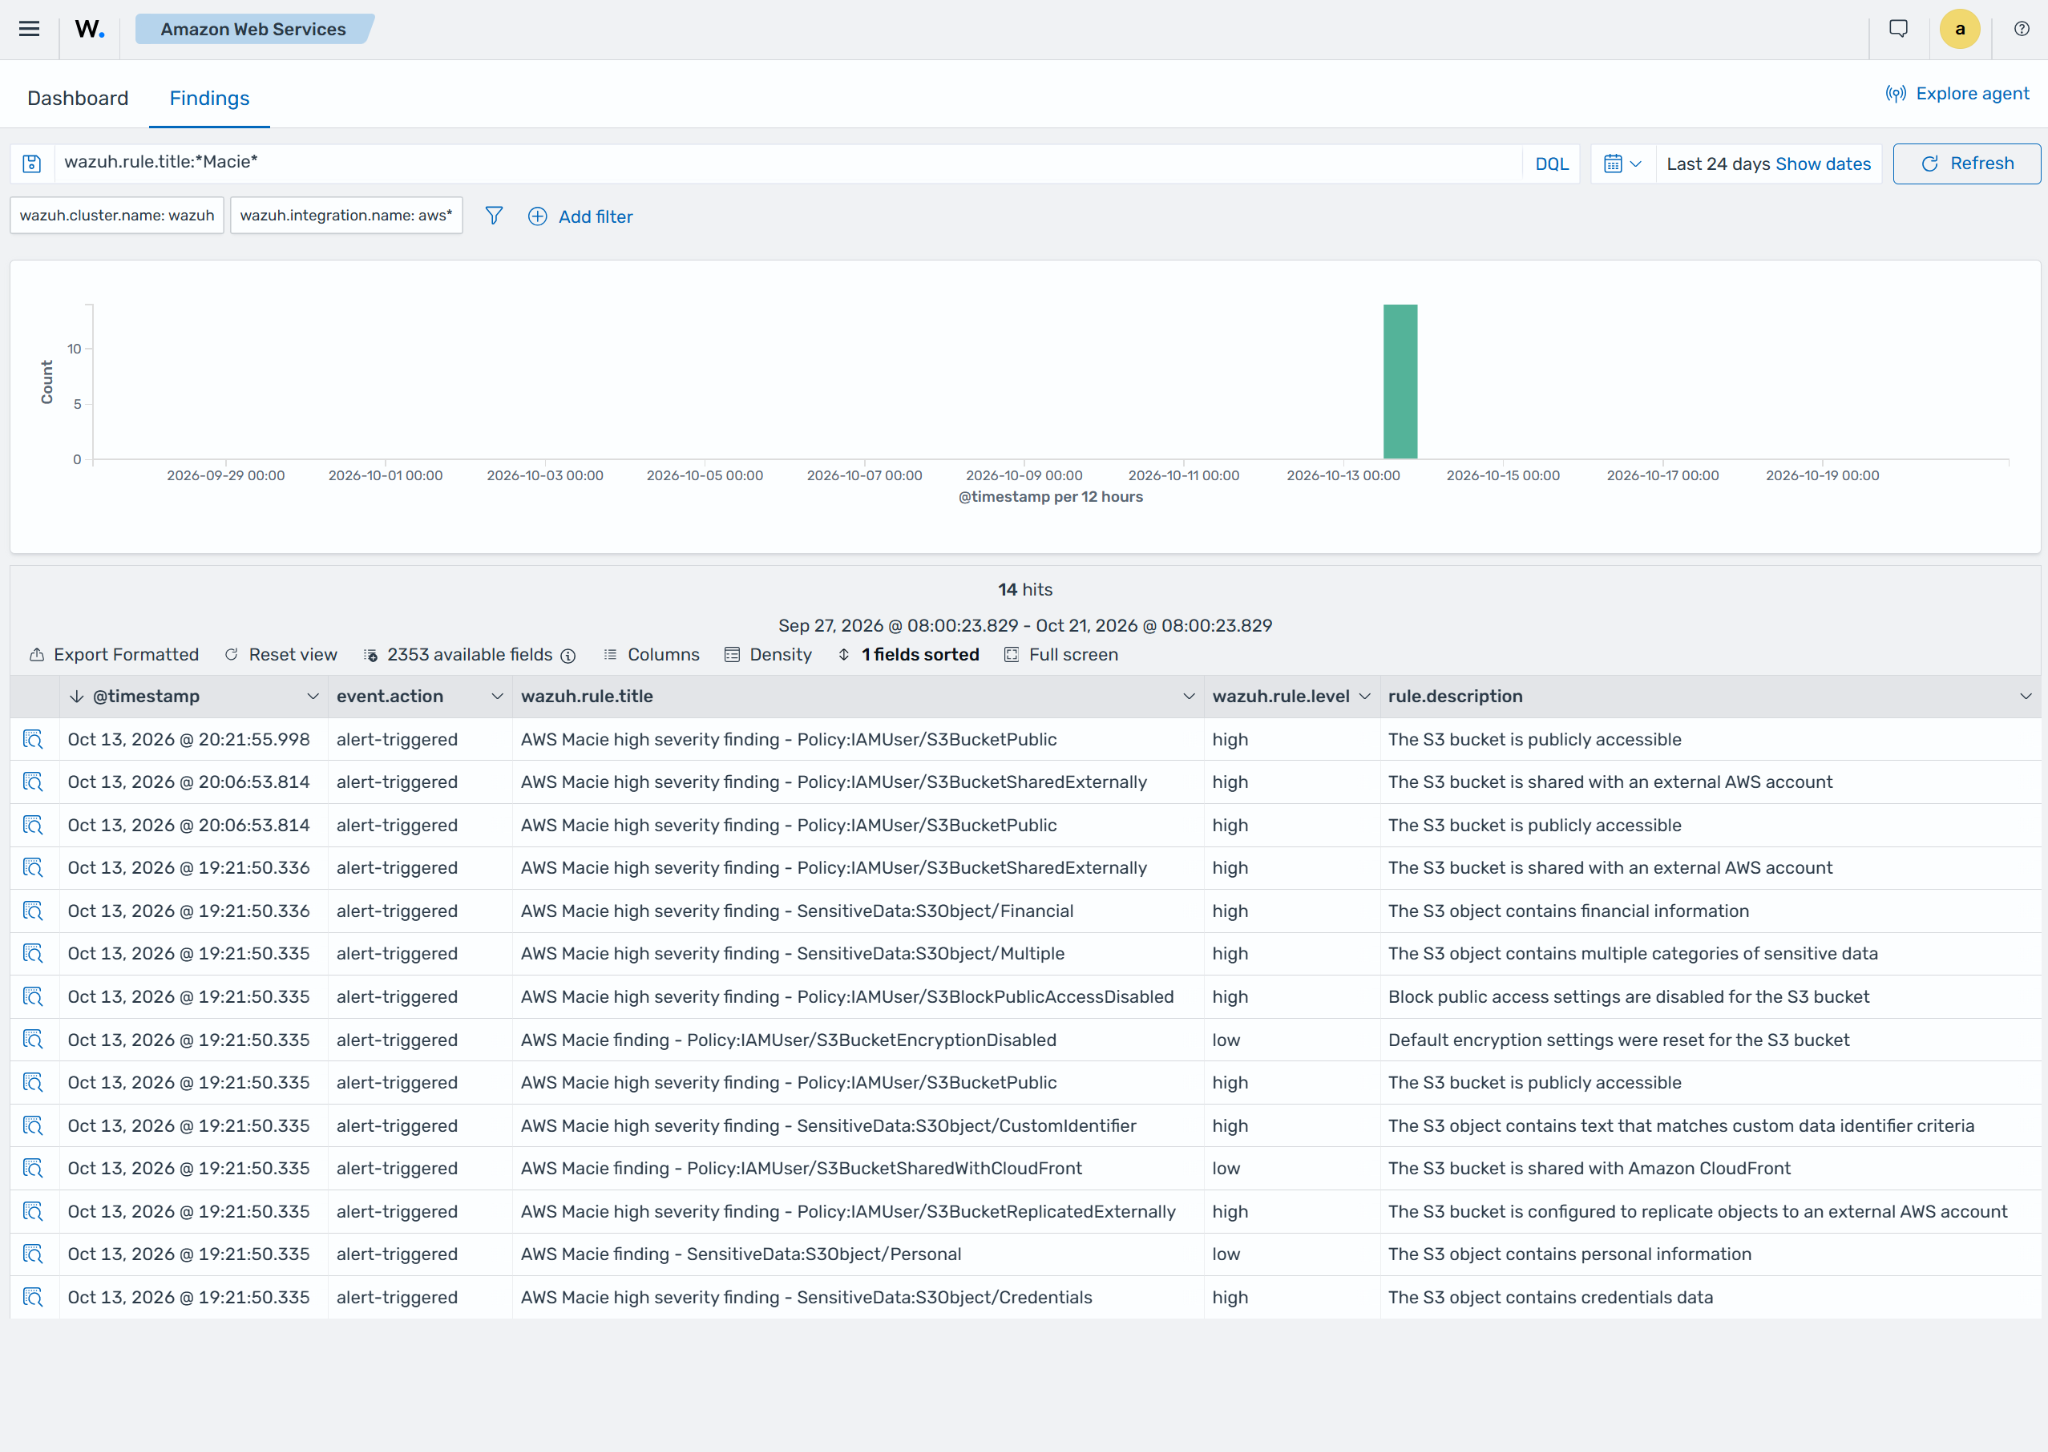
You can expand a finding to see more information, including its description and details about the affected S3 bucket.