Wazuh indexer
Wazuh 5.x introduces changes to the Wazuh indexer cluster configuration, security settings, and index management. Deploy a new Wazuh indexer and recreate the supported configuration and security settings from the Wazuh 4.x deployment.
You can recreate the following Wazuh indexer configuration and security settings in Wazuh 5.x:
Cluster and node configuration
TLS certificates
Security configuration
Internal users
Roles and role mappings
External authentication providers, including LDAP, Active Directory, SAML, JWT, Kerberos, and client-certificate authentication
You can migrate Wazuh index data from the existing Wazuh 4.x indexer to the Wazuh 5.x indexer using snapshots. The migration requires a snapshot repository that is accessible to the source and destination Wazuh indexer clusters. The following sections describe how to recreate the Wazuh indexer configuration and security settings and migrate the required index data.
Wazuh indexer configuration
Wazuh indexer 5.x stores its configuration under /etc/wazuh-indexer/. The following configuration files and directories are commonly reviewed during the migration.
Path |
Purpose |
|---|---|
|
Main cluster and node configuration |
|
JVM heap and garbage collection settings |
|
Logging configuration |
|
Transport and HTTP TLS certificates |
|
Security plugin configuration |
Note
Do not copy configuration files from a 4.x deployment directly into a 5.x deployment. Use the 4.x configuration as a reference and recreate the required settings manually in the corresponding 5.x files.
Migrate the Wazuh indexer configuration
Perform the following steps on every Wazuh indexer node of the new Wazuh 5.x cluster.
Stop the Wazuh indexer service:
# systemctl stop wazuh-indexer
Review the Wazuh 4.x configuration and recreate the required settings manually in the corresponding Wazuh 5.x files.
Update or remove the Wazuh 4.x settings that changed in Wazuh 5.x:
Setting
Wazuh 5.x change
compatibility.override_main_response_versionRemoved. The Wazuh indexer doesn't start if
opensearch.ymlcontains this setting.opensearch_performance_analyzer.*,plugins.anomaly_detection.*,plugins.asynchronous_search.*,plugins.ml_commons.*,plugins.query.datasources.*,plugins.neural_search.*,knn.*Removed. Wazuh indexer 5.x doesn't include the related plugins. Also remove the settings of the
opensearch-observabilityplugin (observability and notebooks), which Wazuh indexer 5.x no longer includes.cluster.initial_master_nodesRenamed to
cluster.initial_cluster_manager_nodes, which the Wazuh 5.xopensearch.ymlalready sets. Copy the node list to the new setting and don't add the old one.plugins.security.ssl.transport.enforce_hostname_verification,plugins.security.ssl.transport.resolve_hostnameRenamed to
transport.ssl.enforce_hostname_verificationandtransport.ssl.resolve_hostname, which the Wazuh 5.xopensearch.ymlalready sets. Don't add the Wazuh 4.x settings: the Wazuh indexer doesn't start ifopensearch.ymldefines both the old and the new name of a setting.transport.ssl.enforce_hostname_verificationistruein Wazuh 5.x (it wasfalsein Wazuh 4.x), so each node certificate must include the node address in its subject alternative names.transport.ssl.resolve_hostnameremainsfalse.plugins.security.authcz.admin_dn,plugins.security.nodes_dnThe distinguished name (DN) attribute order differs. Keep the values that the Wazuh 5.x package generated. If you keep the Wazuh 4.x certificates, set them to the subjects of those certificates.
plugins.security.ssl.*certificate pathsThe Wazuh 5.x package names the node certificate
indexer.pemandindexer-key.pem. To keep the Wazuh 4.x certificates, copy them to/etc/wazuh-indexer/certs/asindexer.pem,indexer-key.pem,admin.pem,admin-key.pem, androot-ca.pem, so the Wazuh 5.x paths stay valid. To keep the certificates that the Wazuh 5.x package issued, don't change the paths.Multi-tenancy settings
Disabled by default in Wazuh 5.x.
plugins.security.ssl.http.enabled_ciphers,plugins.security.ssl.http.enabled_protocolsNot set in Wazuh 5.x, which uses the OpenSearch defaults. The Wazuh 4.x installation assistant restricted them to TLS 1.2 and four cipher suites. Copy them only if your security policy requires a restricted list.
plugins.security.system_indices.indicesThe Wazuh 5.x list drops the indices of the removed plugins and adds
.wazuh-internal-state. Keep the Wazuh 5.x values.Review any custom JVM and logging configuration before you apply it to the Wazuh 5.x deployment. Copy only individual non-default lines into the Wazuh 5.x
jvm.optionsandlog4j2.propertiesfiles instead of replacing them.Edit the security configuration files as described in the Wazuh indexer security configuration section. Apply the configuration after you start the Wazuh indexer service on every node, as described in Apply the security configuration.
Start the Wazuh indexer service:
# systemctl start wazuh-indexer
After the Wazuh indexer service is running on every node and you have applied the security configuration, verify that the nodes have joined the cluster.
$ curl -k -u <USERNAME>:<PASSWORD> \
  https://<WAZUH_INDEXER_IP>:9200/_cat/nodes?v
Where:
<USERNAME>: is the username of a Wazuh indexer user with permissions to query the cluster.<PASSWORD>: is the password of the specified Wazuh indexer user.<WAZUH_INDEXER_IP>: is the IP address or hostname of a Wazuh indexer node in the Wazuh 5.x cluster. In an all-in-one deployment, use127.0.0.1.
Note
Retrieve the generated
WAZUH_INDEXER_ADMIN_PASSWORDfrom/etc/wazuh-indexer/export/credentials.envon the Wazuh indexer node. To print only the value, rungrep '^WAZUH_INDEXER_ADMIN_PASSWORD=' /etc/wazuh-indexer/export/credentials.env | cut -d= -f2-on the Wazuh indexer node.
Wazuh indexer security configuration
The Wazuh indexer security configuration controls authentication, authorization, user management, and access permissions.
During the migration, review the existing Wazuh 4.x security configuration and recreate the required users, roles, role mappings, authentication providers, and security settings manually in the corresponding Wazuh 5.x files.
The security configuration is stored under /etc/wazuh-indexer/opensearch-security/.
File |
Purpose |
|---|---|
|
Authentication and authorization configuration |
|
Internal user accounts |
|
Role definitions |
|
Role mappings |
|
Permission groups |
|
Dashboard tenants |
|
Allowed node certificate identities |
|
When enabled, limits every user except the super admin to the listed REST API endpoints and methods |
|
Audit logging configuration |
Note
Before migrating the security settings, export the active Wazuh 4.x security configuration. The files on disk might not reflect the active configuration because the effective security configuration is stored in the Wazuh indexer security index.
Run the following commands on a Wazuh 4.x indexer node to export the active security configuration:
# install -d -o wazuh-indexer -g wazuh-indexer <BACKUP_DIRECTORY>
# /usr/share/wazuh-indexer/bin/indexer-security-init.sh --options "-backup <BACKUP_DIRECTORY> -icl -nhnv"
Replace <BACKUP_DIRECTORY> with the directory that stores the exported files, for example /var/tmp/security-backup. Use the exported internal_users.yml, roles.yml, and roles_mapping.yml files as the reference for the Wazuh 5.x security configuration.
Before applying the recreated security configuration, verify that the recreated roles reference valid permissions and that the role mappings reference users and roles defined in the Wazuh 5.x security configuration. Replace Wazuh 4.x index patterns in recreated roles, such as wazuh-alerts-*, with the Wazuh 5.x index patterns, such as wazuh-events-v5-*, wazuh-findings-v5-*, and wazuh-states-*. Keep the Wazuh 5.x permission names. Users with roles that reference Wazuh 4.x index patterns can log in, but the Wazuh dashboard doesn't display their data. Refer to the user administration documentation for more information.
Apply the security configuration
After you recreate the required security configuration, apply the changes to the Wazuh indexer. Make the same changes to the files in /etc/wazuh-indexer/opensearch-security/ on every Wazuh indexer node.
Restart the Wazuh indexer service on every node:
# systemctl restart wazuh-indexer
Apply the security configuration. Run the script once, from a single node whose files contain all the changes, after the Wazuh indexer service is running on every node. The Wazuh indexer stores the security configuration in its security index, so the change reaches every node:
# /usr/share/wazuh-indexer/bin/indexer-security-init.shWarning
Running
indexer-security-init.shloads the security configuration from/etc/wazuh-indexer/opensearch-security/into the Wazuh indexer security index. This can overwrite security settings previously configured through the Wazuh dashboard or security API. Ensure that the configuration files contain the security settings you want to retain before running the script. Running the script later from a node whose files lack the recreated users, roles, or role mappings removes them from the whole cluster, and the affected users can no longer log in. Keep the files in/etc/wazuh-indexer/opensearch-security/identical on every node.Verify that authentication works. Log in to the Wazuh dashboard and confirm that users can authenticate and access the resources their assigned roles permit. Also verify each external authentication backend, such as LDAP or SAML, against every Wazuh indexer node before you point production traffic at the Wazuh 5.x cluster.
Indexer data migration
You can migrate Wazuh indices from the Wazuh 4.x indexer to the Wazuh 5.x indexer using snapshots. The migration requires a snapshot repository that is accessible to both the source and destination Wazuh indexer clusters. When restored on the destination Wazuh indexer, the indices retain their indexed data and original timestamps.
The restored indices remain separate from the Wazuh 5.x indices and data streams created for new data. You can create an index pattern for the restored indices to search and analyze historical data from the Discover page on the Wazuh dashboard.
Note
Restored indices retain their Wazuh 4.x mappings and remain separate from the Wazuh 5.x data schema. Wazuh 5.x does not write new data to the restored indices.
The following sections describe the steps required to migrate Wazuh indices from the Wazuh 4.x indexer to the Wazuh 5.x indexer.
Note
Index data migration to Wazuh 5.x requires the source deployment to run Wazuh 4.4.0 or later due to snapshot compatibility requirements. Indices created before Wazuh 4.4.0 can't be restored, even if the deployment was later upgraded to Wazuh 4.4.0 or later.
Set up a snapshot repository on Wazuh 4.x
On the Wazuh 4.x dashboard, perform the following steps:
Click the ☰ menu, navigate to Indexer management > Snapshot Management > Repositories, and select Create repository to create a new snapshot repository.
Enter a Repository name, such as
wazuh-4x-migration, select the repository type Shared file system, enter the repository Location/mnt/snapshots, and select Add to register the new repository.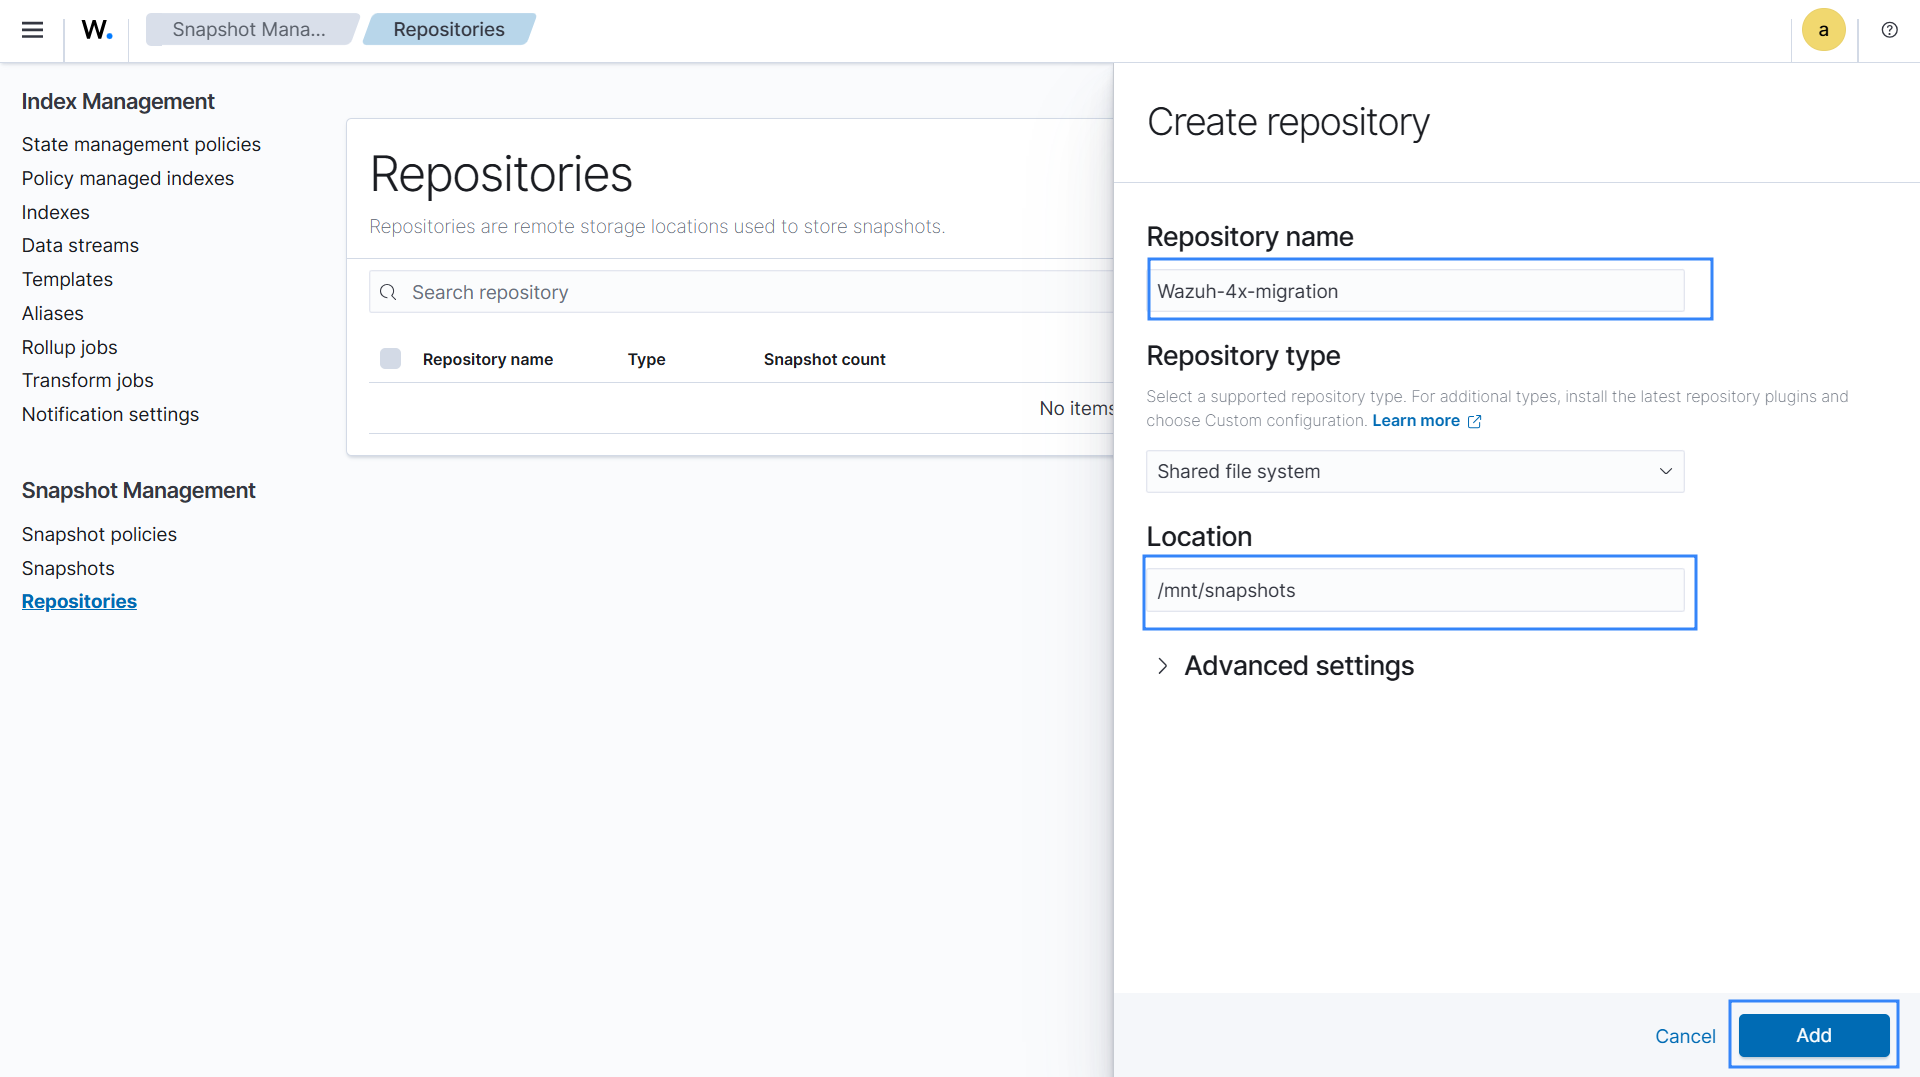
Take a snapshot of the Wazuh 4.x indices
On the Wazuh 4.x dashboard, perform the following steps:
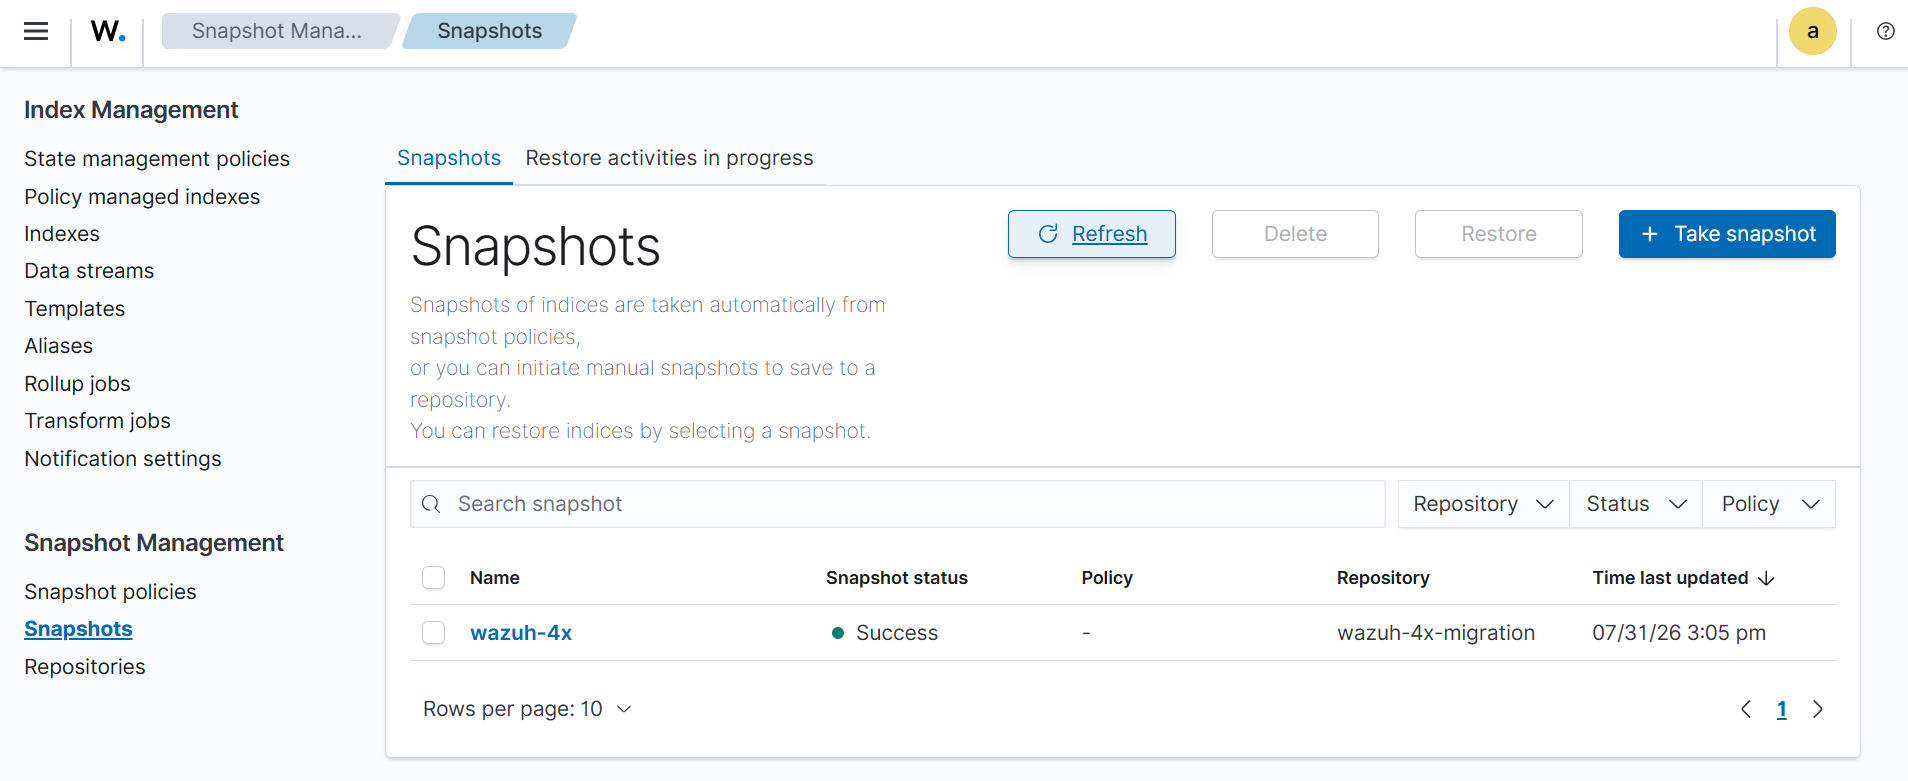
Click the ☰ menu, navigate to Indexer management > Snapshot Management > Snapshots.
Select Take snapshot and enter a Snapshot name.
Select the Wazuh data indices that you want to migrate from the list. The Wazuh 4.x dashboard ignores index patterns that you type in this field and includes every index in the snapshot.
Warning
Do not include system indices or the cluster state in the migration snapshot. The snapshot is intended to transfer Wazuh 4.x historical data to the new Wazuh 5.x deployment, not the Wazuh 4.x indexer configuration. Before you restore the snapshot, verify that it contains only the Wazuh data indices you selected.
Select the repository you created earlier to store the snapshots.
Ensure Include cluster state in snapshots is not selected in the Advanced options to prevent the snapshot from including cluster-level configuration.
Click Add to create a new snapshot. The snapshot files are saved in the repository location
/mnt/snapshots.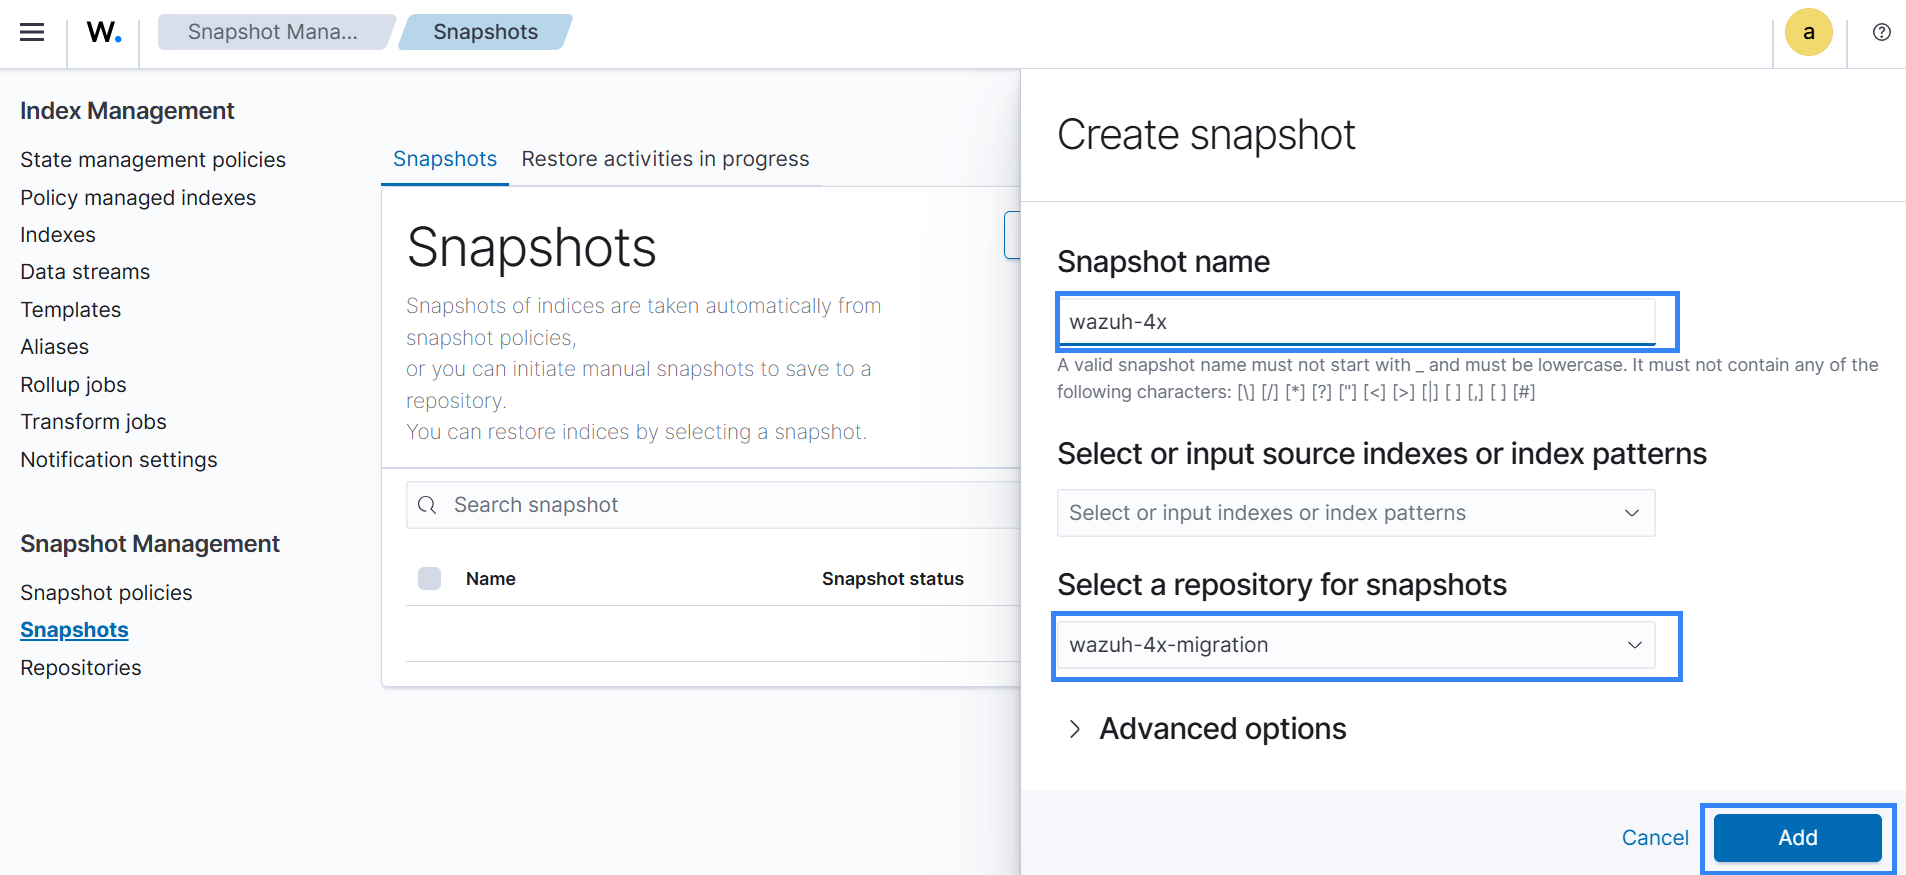
Set up a snapshot repository on Wazuh 5.x
Run the command below on the Wazuh 5.x indexer node to set up a read-only snapshot repository:
# curl -k -X PUT \
  --cert /etc/wazuh-indexer/certs/admin.pem \
  --key /etc/wazuh-indexer/certs/admin-key.pem \
  "https://<WAZUH_INDEXER_IP>:9200/_snapshot/wazuh-4x-migration" \
  -H "Content-Type: application/json" \
  -d '{
    "type": "fs",
    "settings": {
      "location": "/mnt/snapshots",
      "readonly": true
    }
  }'
The command output looks similar to this:
{"acknowledged":true}
Replace <WAZUH_INDEXER_IP> with the IP address of the Wazuh 5.x indexer. In an all-in-one deployment, use 127.0.0.1 because the Wazuh indexer listens on the loopback address.
Restore the snapshot on Wazuh 5.x
Perform the following steps on the Wazuh 5.x deployment.
On the Wazuh dashboard, navigate to Indexer management > Snapshot Management > Snapshots. The snapshot created on the Wazuh 4.x deployment is available to the Wazuh 5.x deployment through the shared
/mnt/snapshotsrepository. Select the migration snapshot, then click Restore.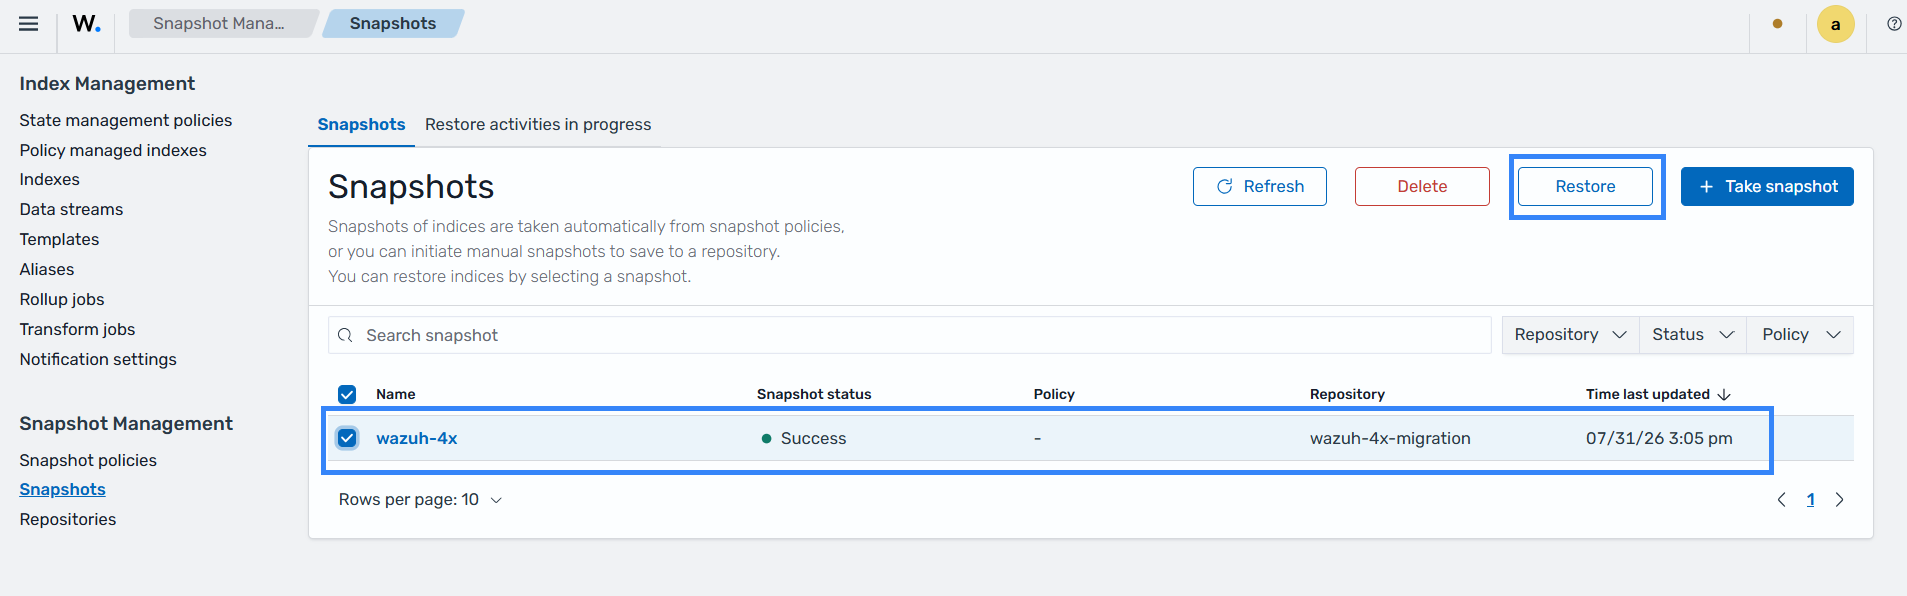
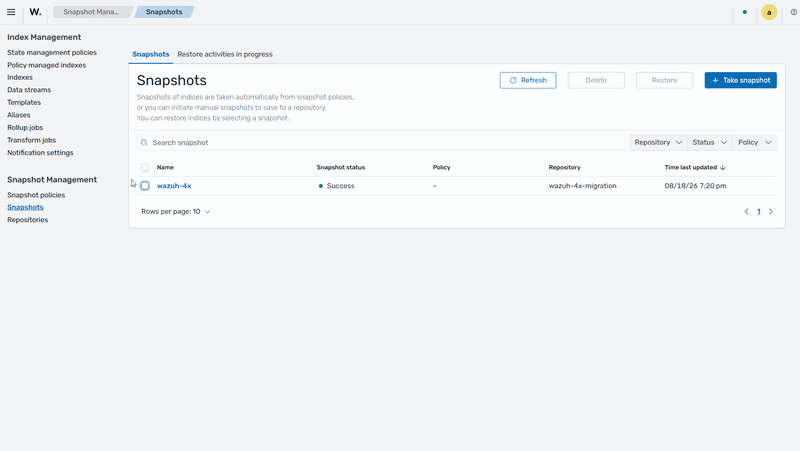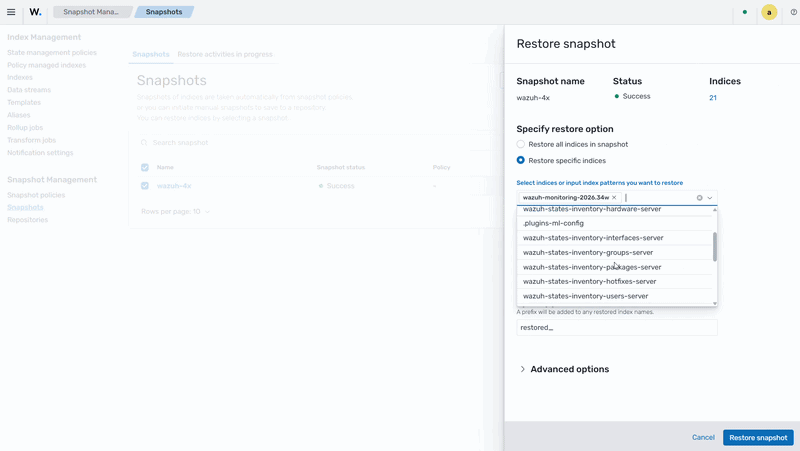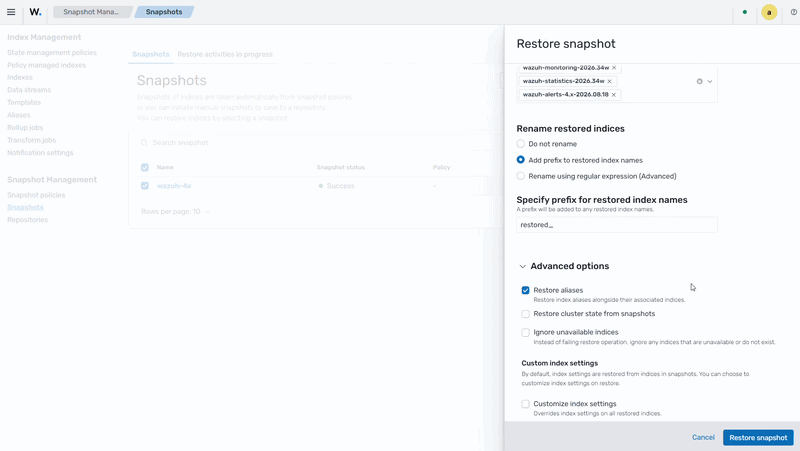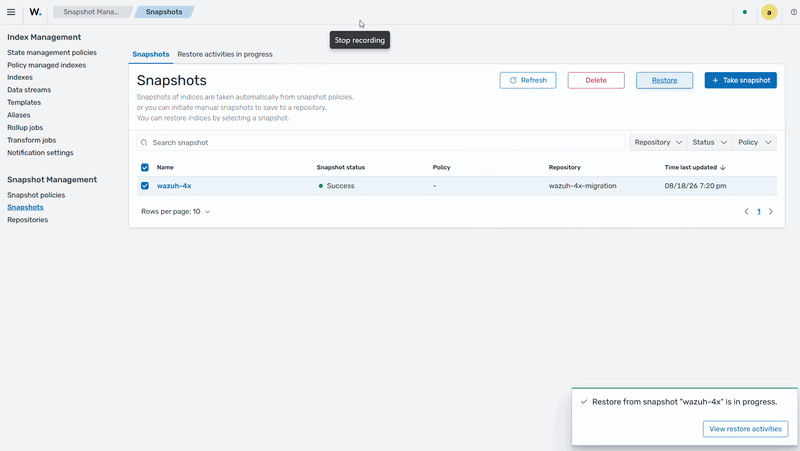
Click Restore snapshot.
Note
You can choose to restore specific indices or rename the indices. In the image above, we add the prefix
restored_to the restored index names.Warning
Do not restore system indices or the global cluster state into the Wazuh 5.x deployment (for example,
.kibana*,.opendistro*).Navigate to Indexer management > Indexes on the Wazuh dashboard, and filter with the prefix
restored_to view the restored indices.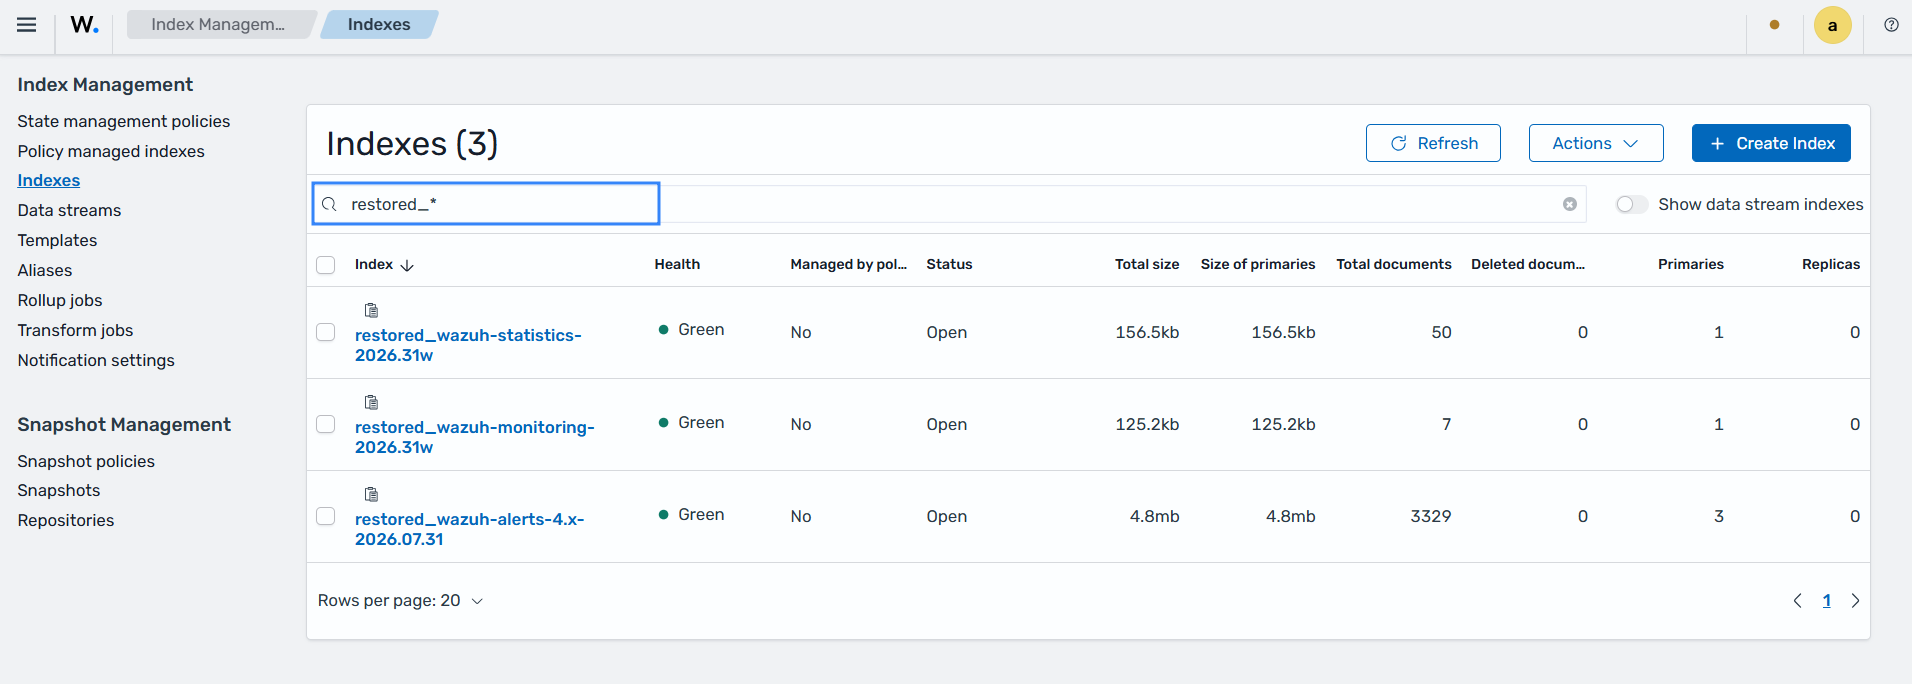
Create an index pattern to retrieve the indices' data. On the Wazuh dashboard, navigate to Dashboards Management > Index patterns, then click Create index pattern.
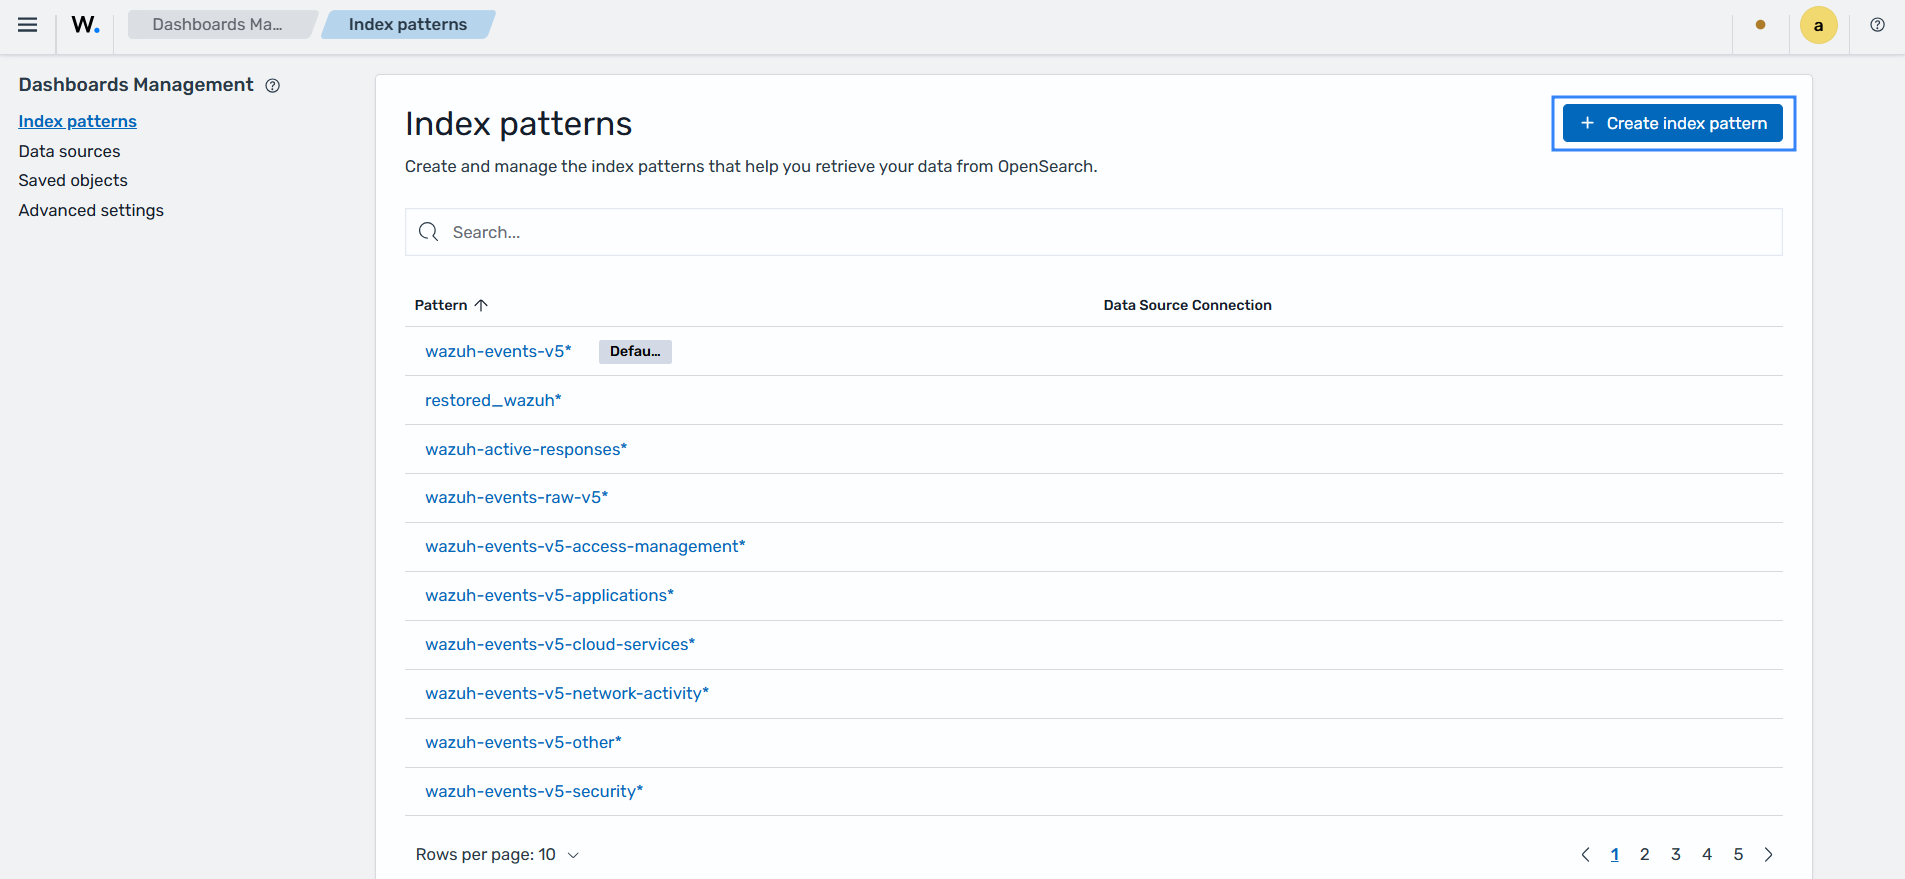
Set the Index pattern name, then click Next step. In the image below, the index pattern name is
restored_wazuh*. Enterrestored_wazuhas the name, because the dashboard adds the trailing*itself.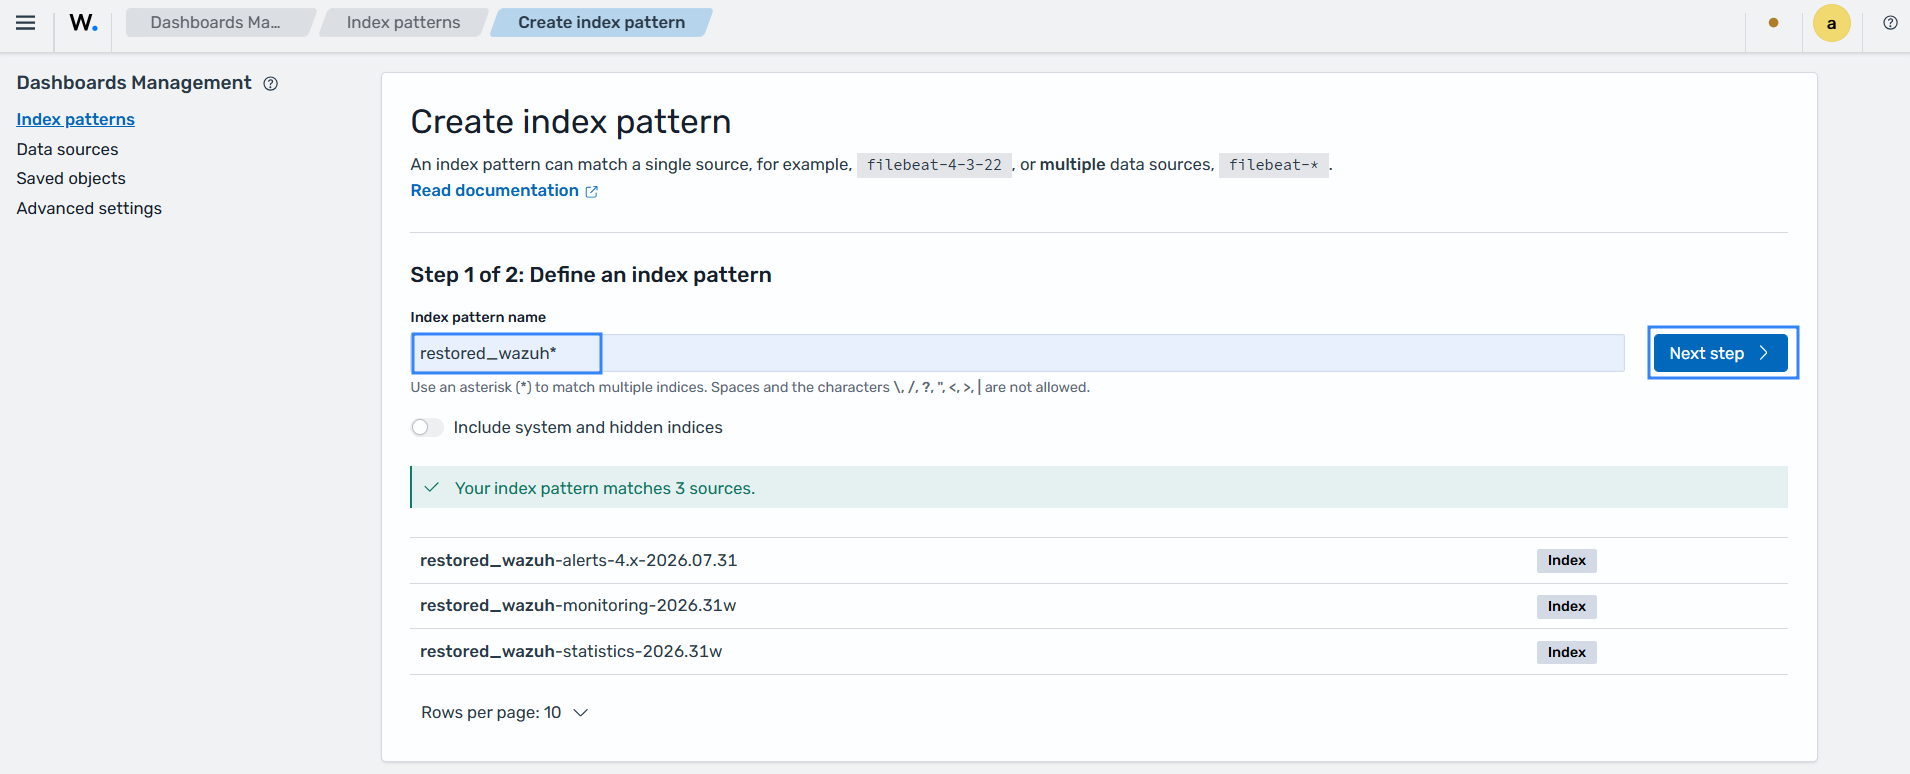
Set the Time field. From the drop-down menu, select timestamp, then click Create index pattern.
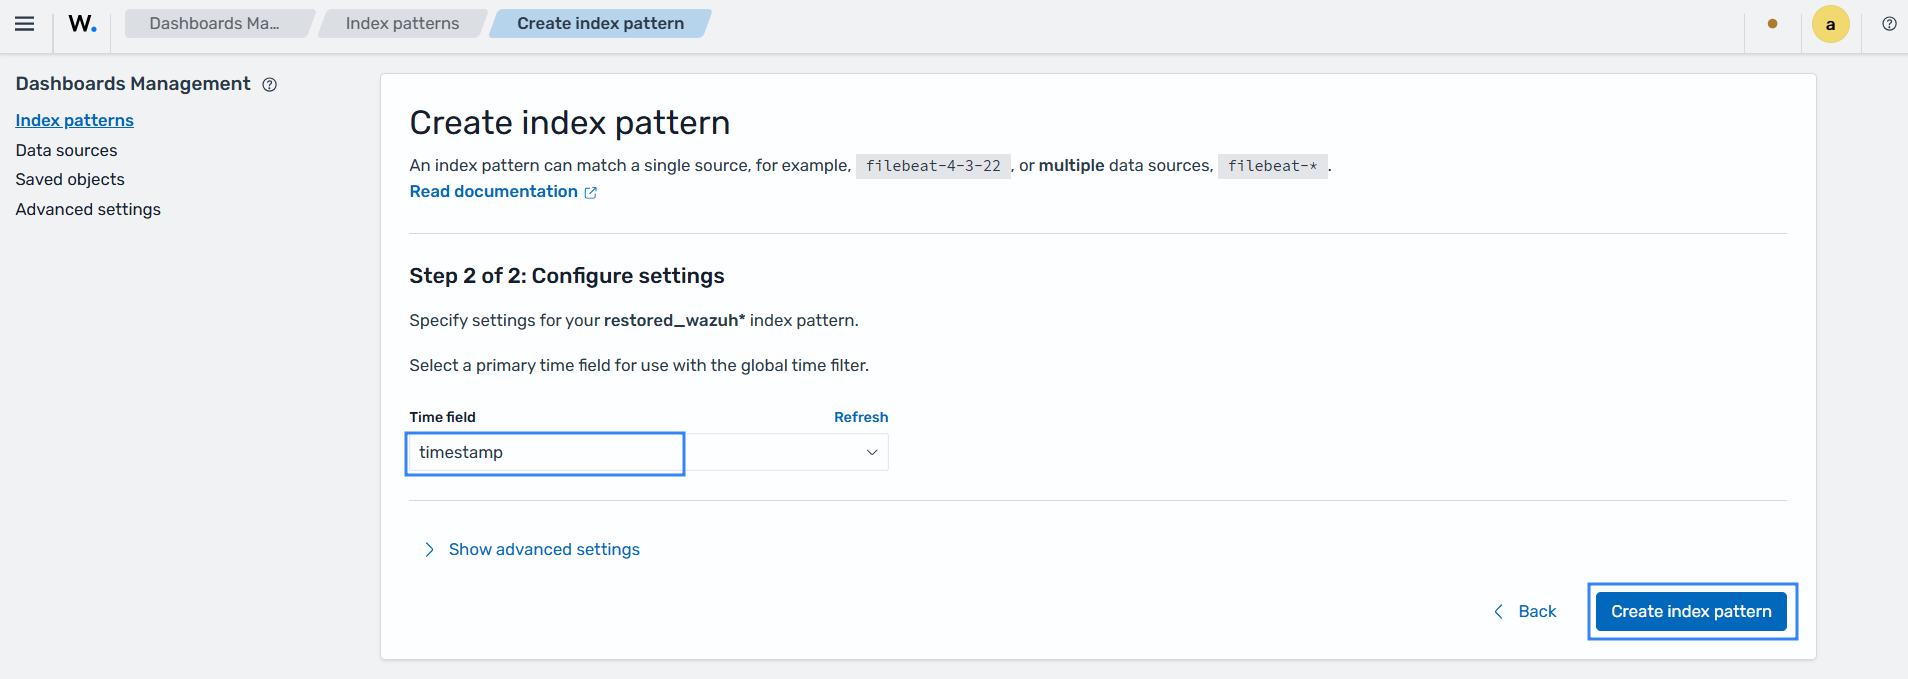
Click the ☰ menu, navigate to Discover on the Wazuh dashboard to verify that the migrated indices are available. Select the Index pattern (
restored_wazuh*) created in the previous step to view the migrated index data.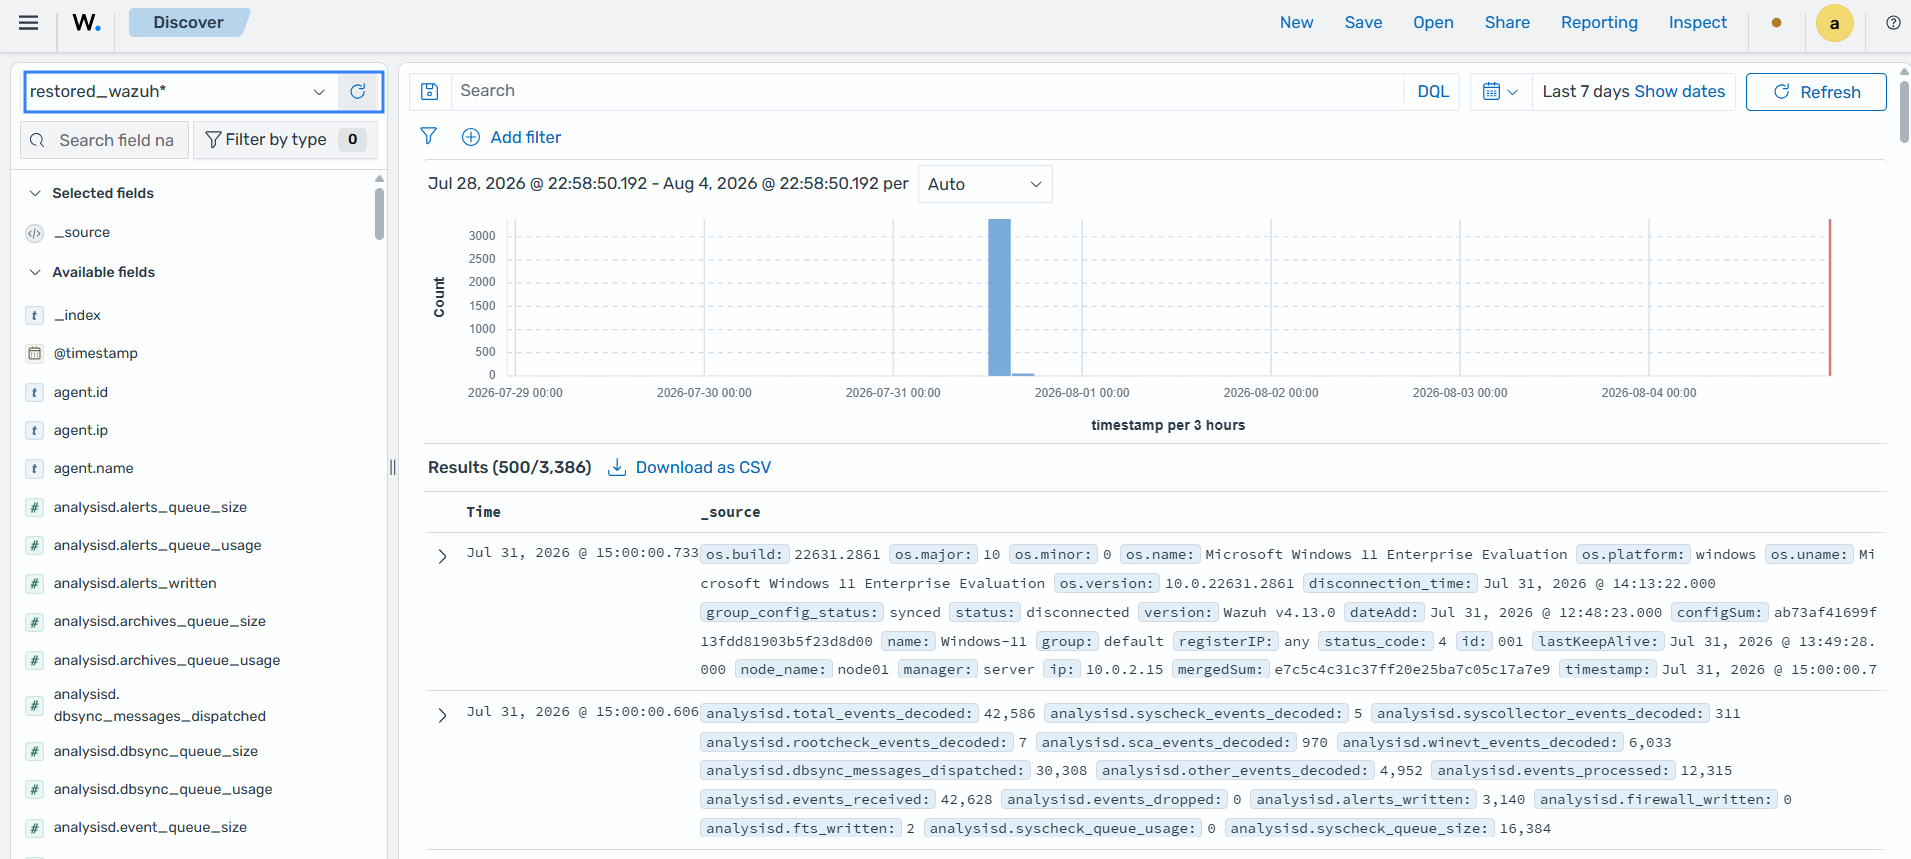
From the Discover page, you can explore and search the migrated index data using the Wazuh dashboard.