HIPAA § 164.308(a)(6)(ii) - Response and reporting
The HIPAA § 164.308(a)(6)(ii) requirement states, "Identify and respond to suspected or known security incidents; mitigate, to the extent practicable, harmful effects of security incidents that are known to the covered entity or business associate; and document security incidents and their outcomes."
This requirement mandates identifying suspected or known security incidents, responding to them, mitigating their potential impact, and documenting the incidents and their outcomes.
Wazuh helps meet this requirement by providing several security monitoring and incident response modules. One of these modules is the Wazuh Active Response module, which automates response actions when security findings meet configured conditions. Wazuh Active Response can execute predefined or custom scripts on monitored endpoints to mitigate detected threats. For example, it can block malicious IP addresses, terminate malicious processes, or perform other configured response actions when a security finding triggers an active response.
Use case: Block a known malicious actor
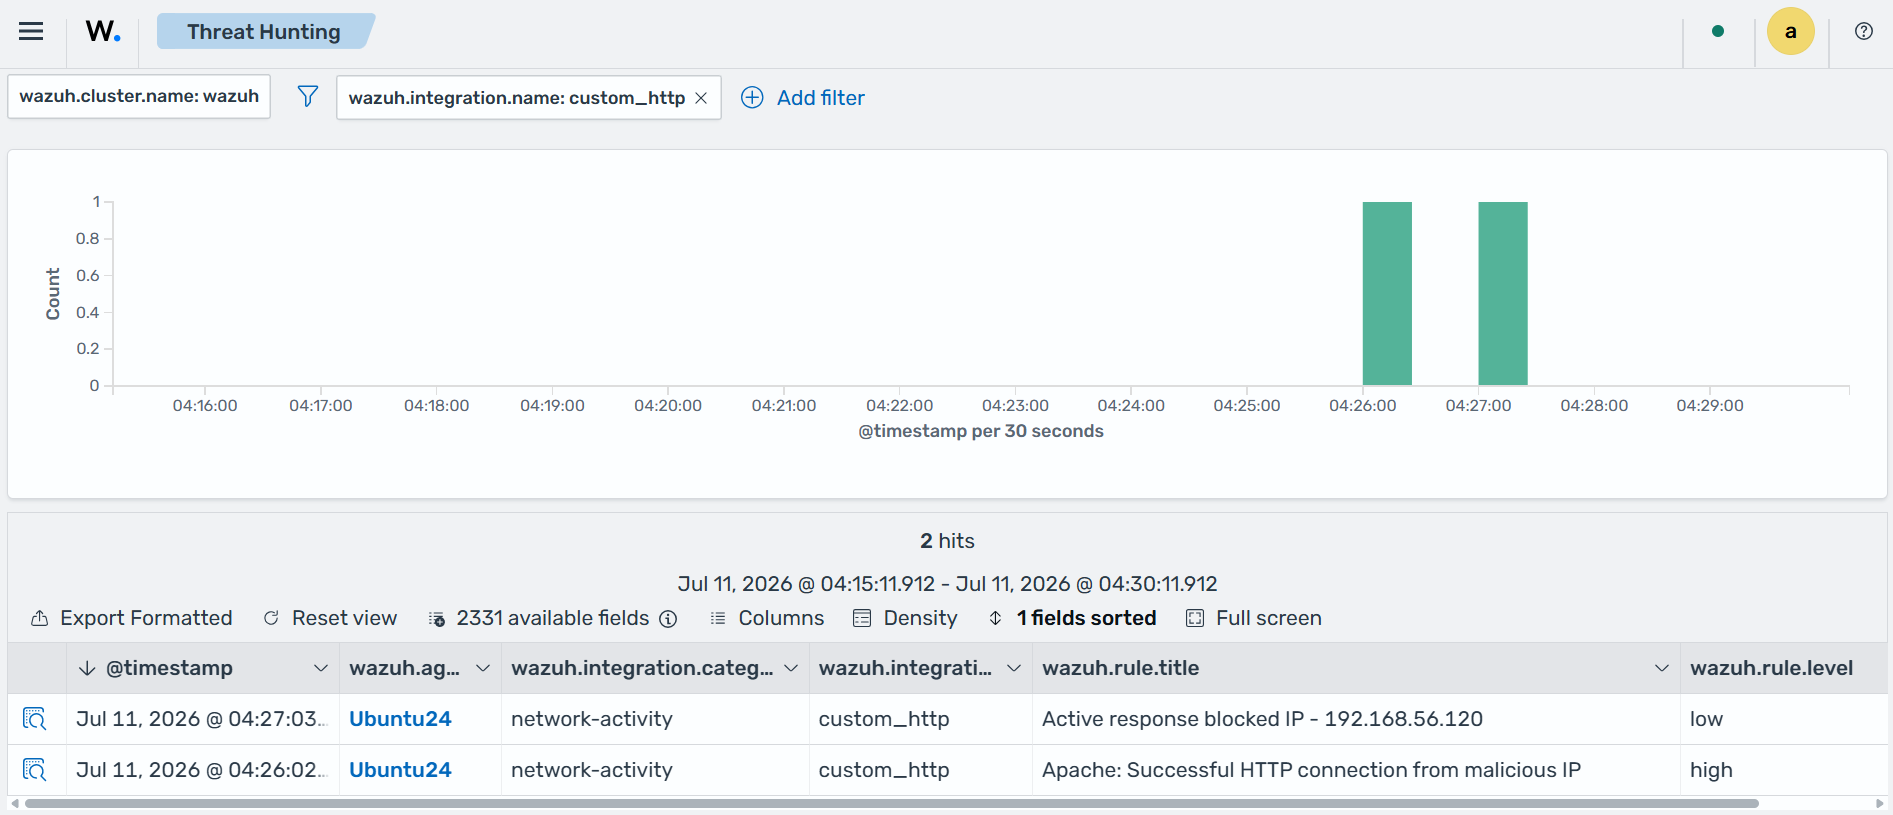
In this example, the Wazuh Active Response module blocks malicious IP addresses from accessing web resources on a web server monitored by a Wazuh agent. See Blocking a known malicious actor for more information.