HIPAA § 164.312(b) - Audit controls
The HIPAA § 164.312(b) requirement states, "A covered entity or business associate must, in accordance with § 164.306, implement hardware, software, and/or procedural mechanisms that record and examine activity in information systems that contain or use electronic protected health information."
This requirement mandates logging activity on systems containing health data, including authentication events, failures, and file read, write, or modification actions.
Wazuh helps meet this requirement by providing capabilities to record and examine activity in information systems that contain or use electronic protected health information (ePHI). An example is log data analysis. The Wazuh Logcollector module collects events from monitored endpoints and applications, including systems that store or process ePHI. Wazuh agents forward these events to the Wazuh manager, where the normalization engine processes them. The Wazuh manager then sends the normalized data to the Wazuh indexer for rule matching and indexing. This enables organizations to analyze activity involving systems that contain or use ePHI and support the review of audit information. See the data analysis section for more information.
Use case: Collecting and analyzing logs across multiple endpoints
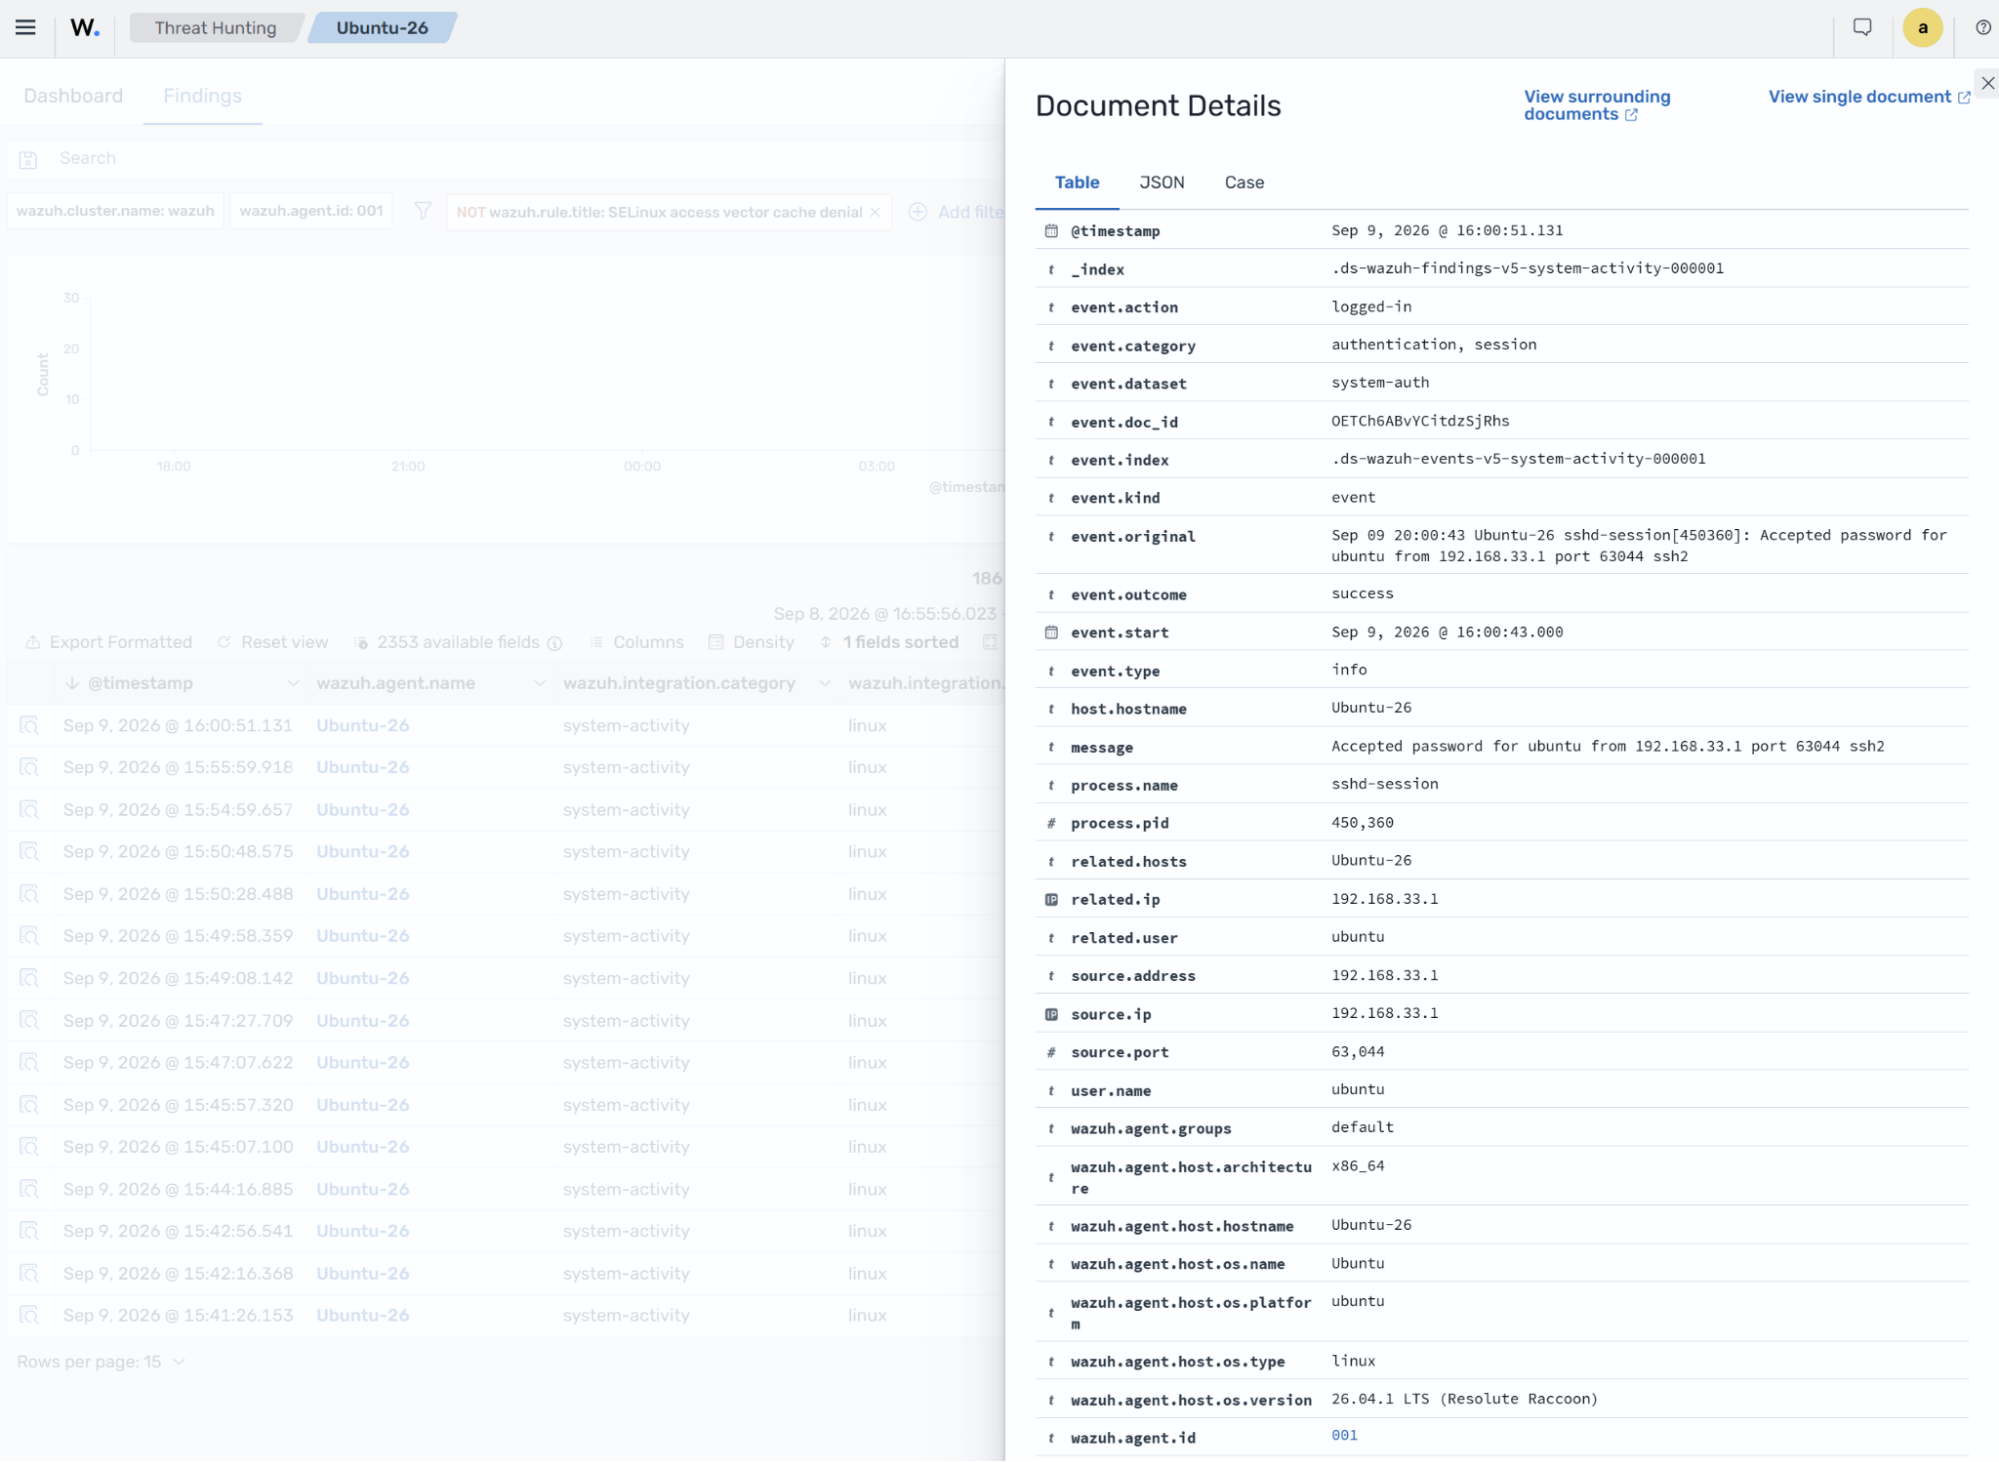
The use case below shows how log data analysis can detect specific events on monitored endpoints.
Wazuh dashboard
Click Threat Hunting from the Wazuh dashboard:
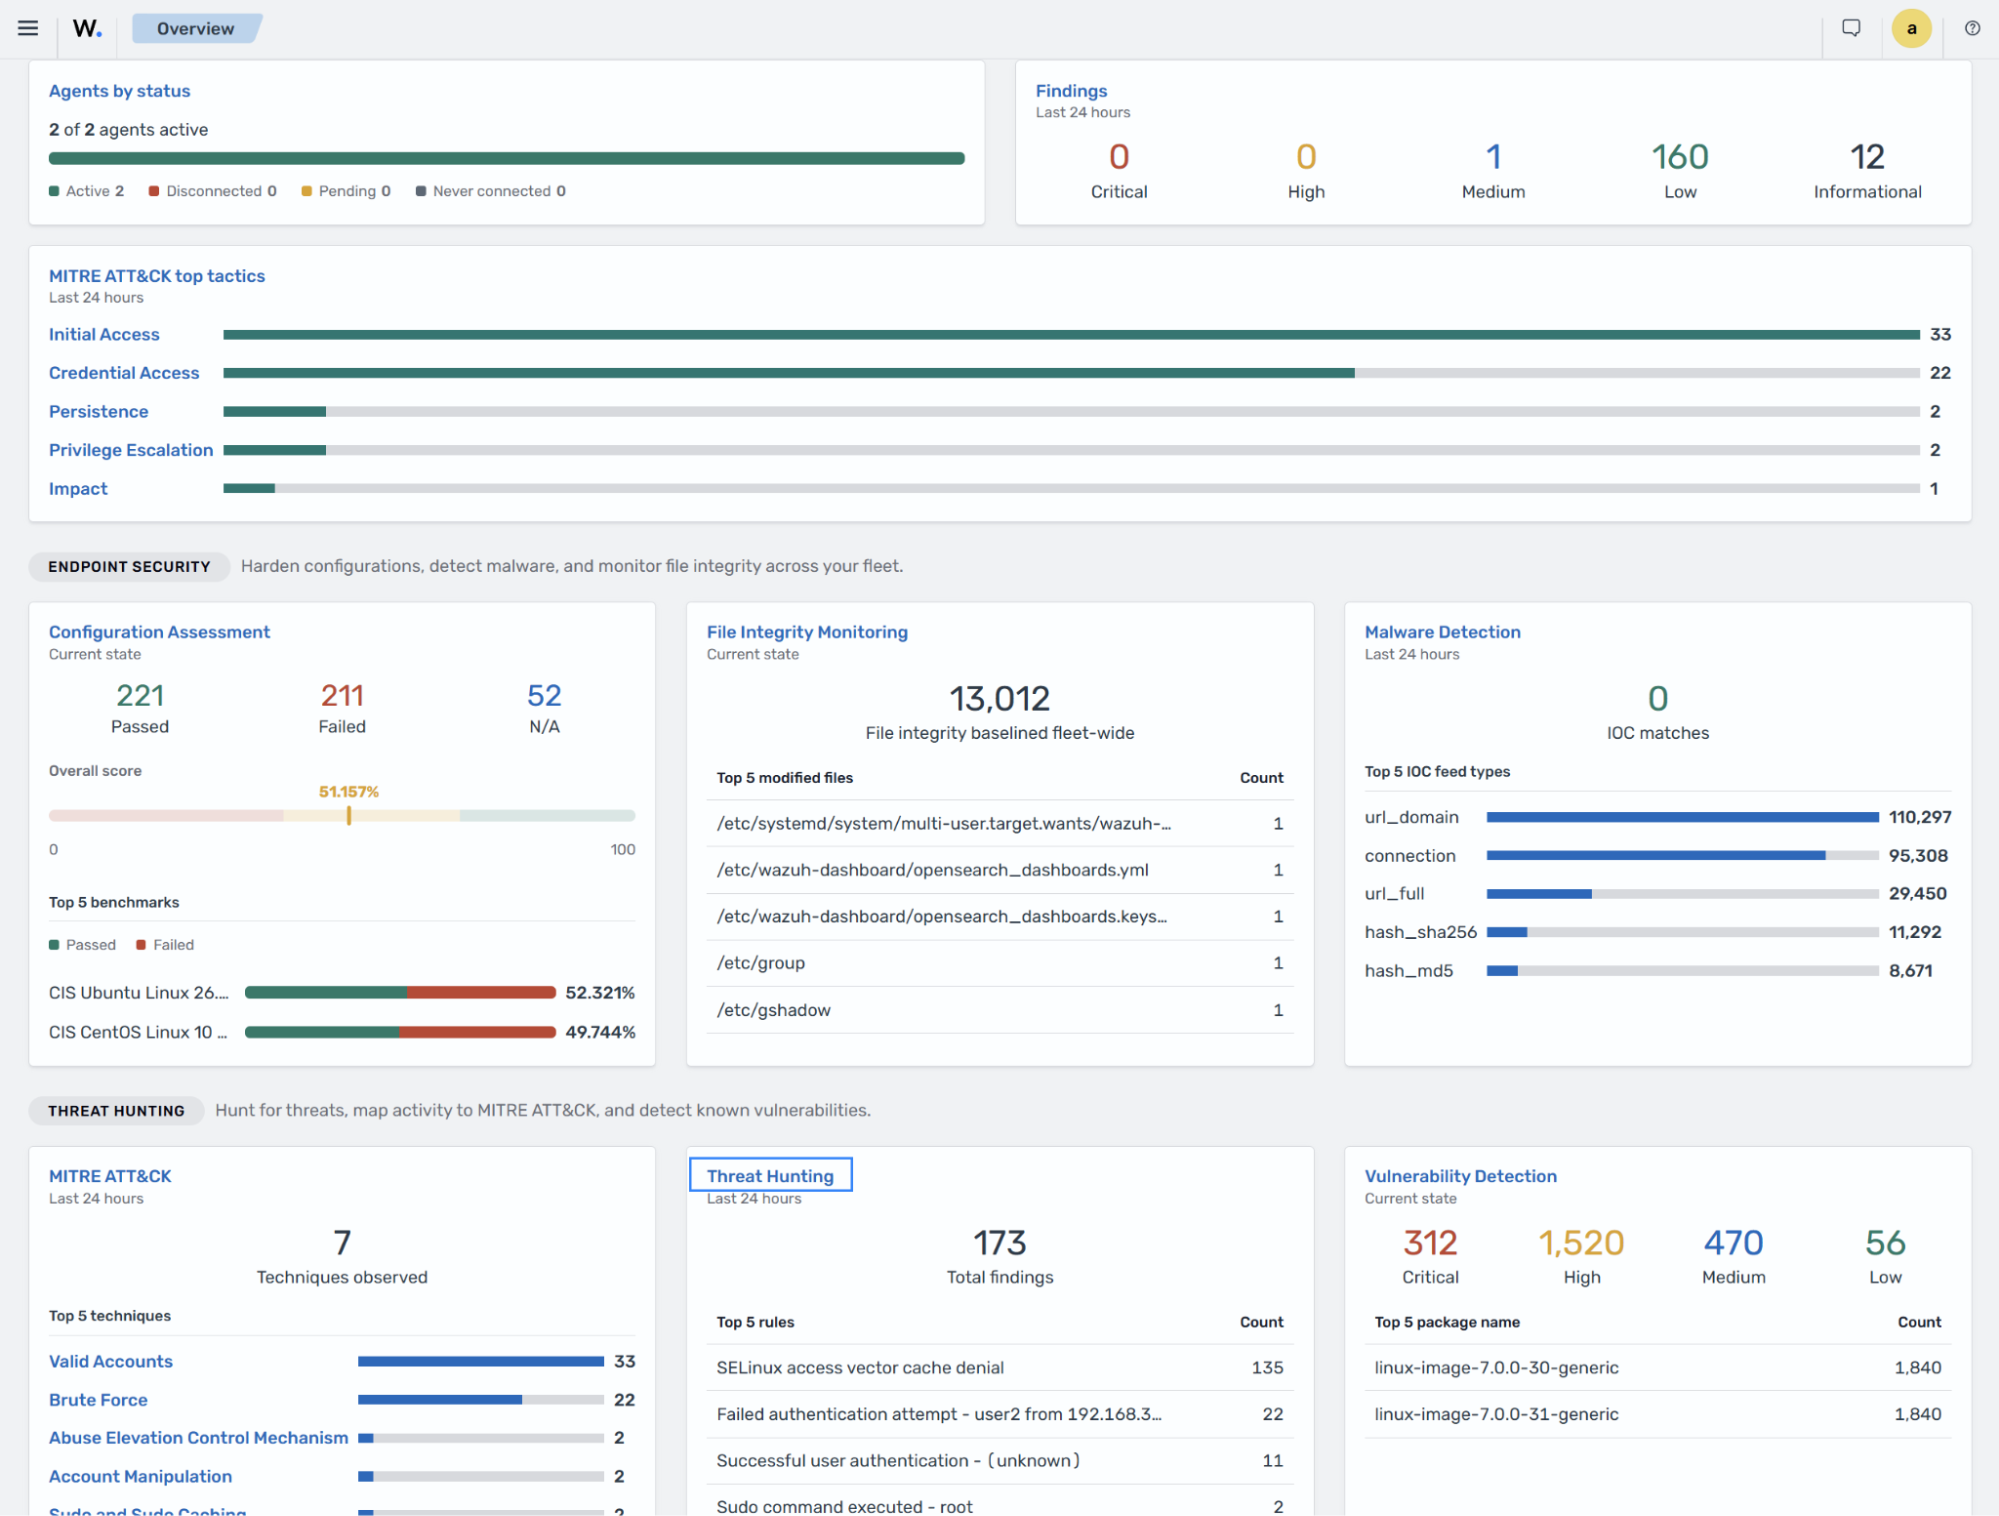
The image below shows the Wazuh Threat Hunting dashboard. The Threat Hunting dashboard provides an overview of security findings, agent activity, integrations, detection rules, and associated MITRE ATT&CK techniques.

Navigate to the Findings section and click on a finding to view details. In this example, the image shows the details of an authentication finding.