Using Wazuh for HIPAA compliance
The Health Insurance Portability and Accountability Act (HIPAA) establishes standards to protect health information and improve healthcare efficiency. Technology can impact healthcare data privacy and security, so HIPAA creates federal protections for individually identifiable health information held by covered entities and business associates. Part 164, Subpart C (Security Standards for the Protection of Electronic Protected Health Information), provides standards for transmitting, handling, storing, and safeguarding electronic protected health information.
Wazuh supports HIPAA compliance by performing log data analysis, configuration assessment, malware detection, file integrity monitoring, vulnerability detection, and active response.
Note
These rules and control mappings are indicative and do not by themselves certify compliance. See Regulatory compliance for more details.
Follow these steps to view the HIPAA-related data on the Wazuh dashboard:
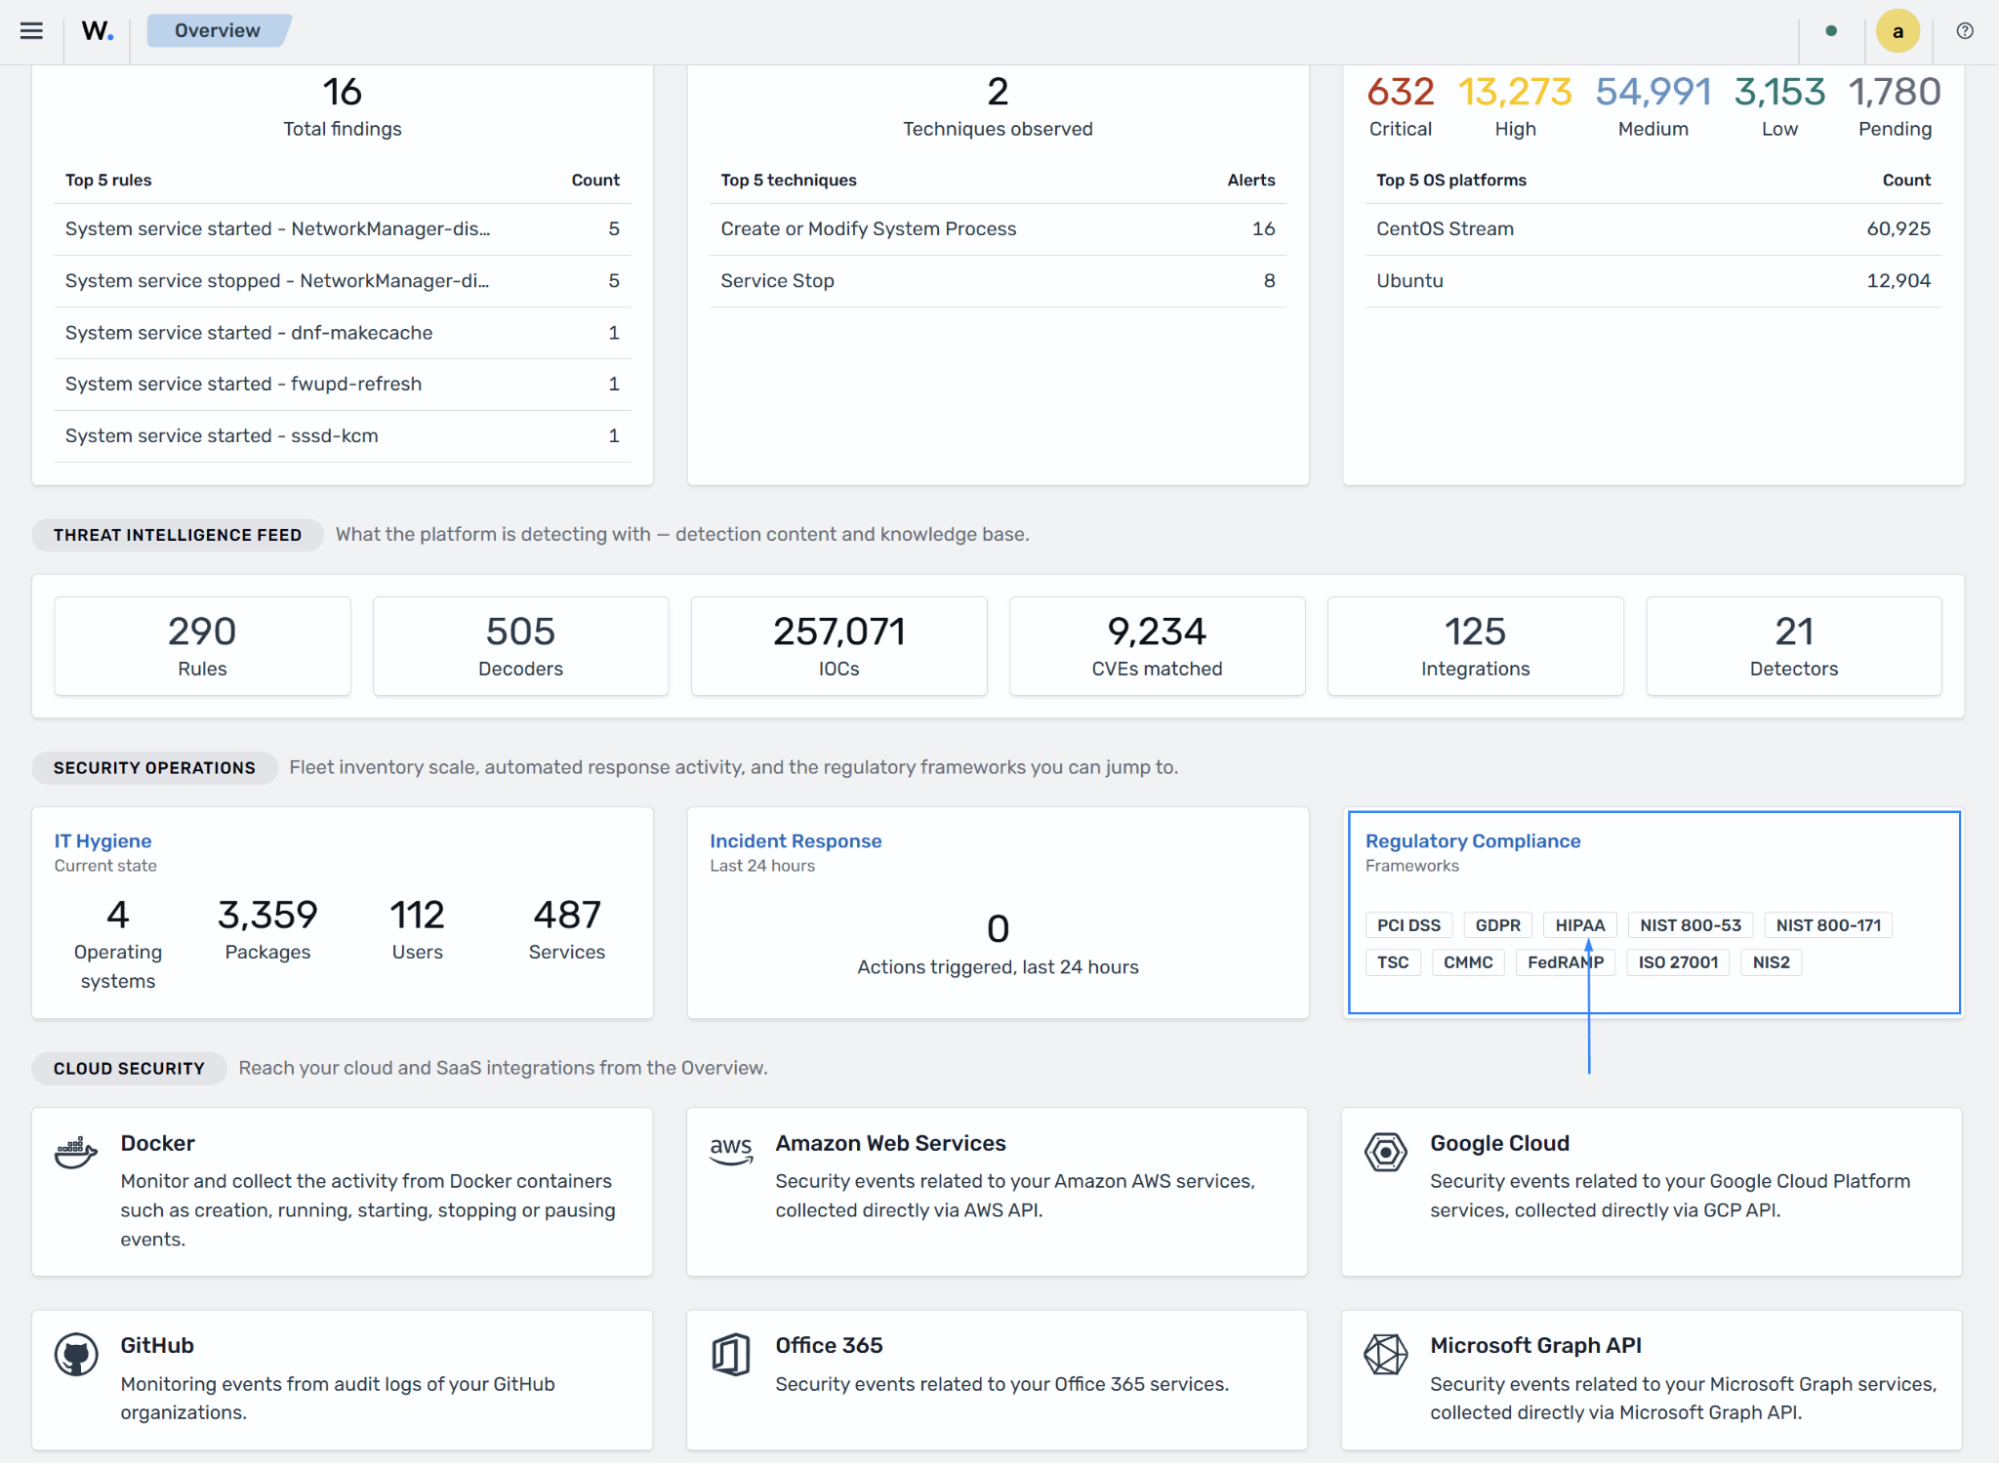
Navigate to Regulatory Compliance from the Wazuh Overview dashboard, then click HIPAA.
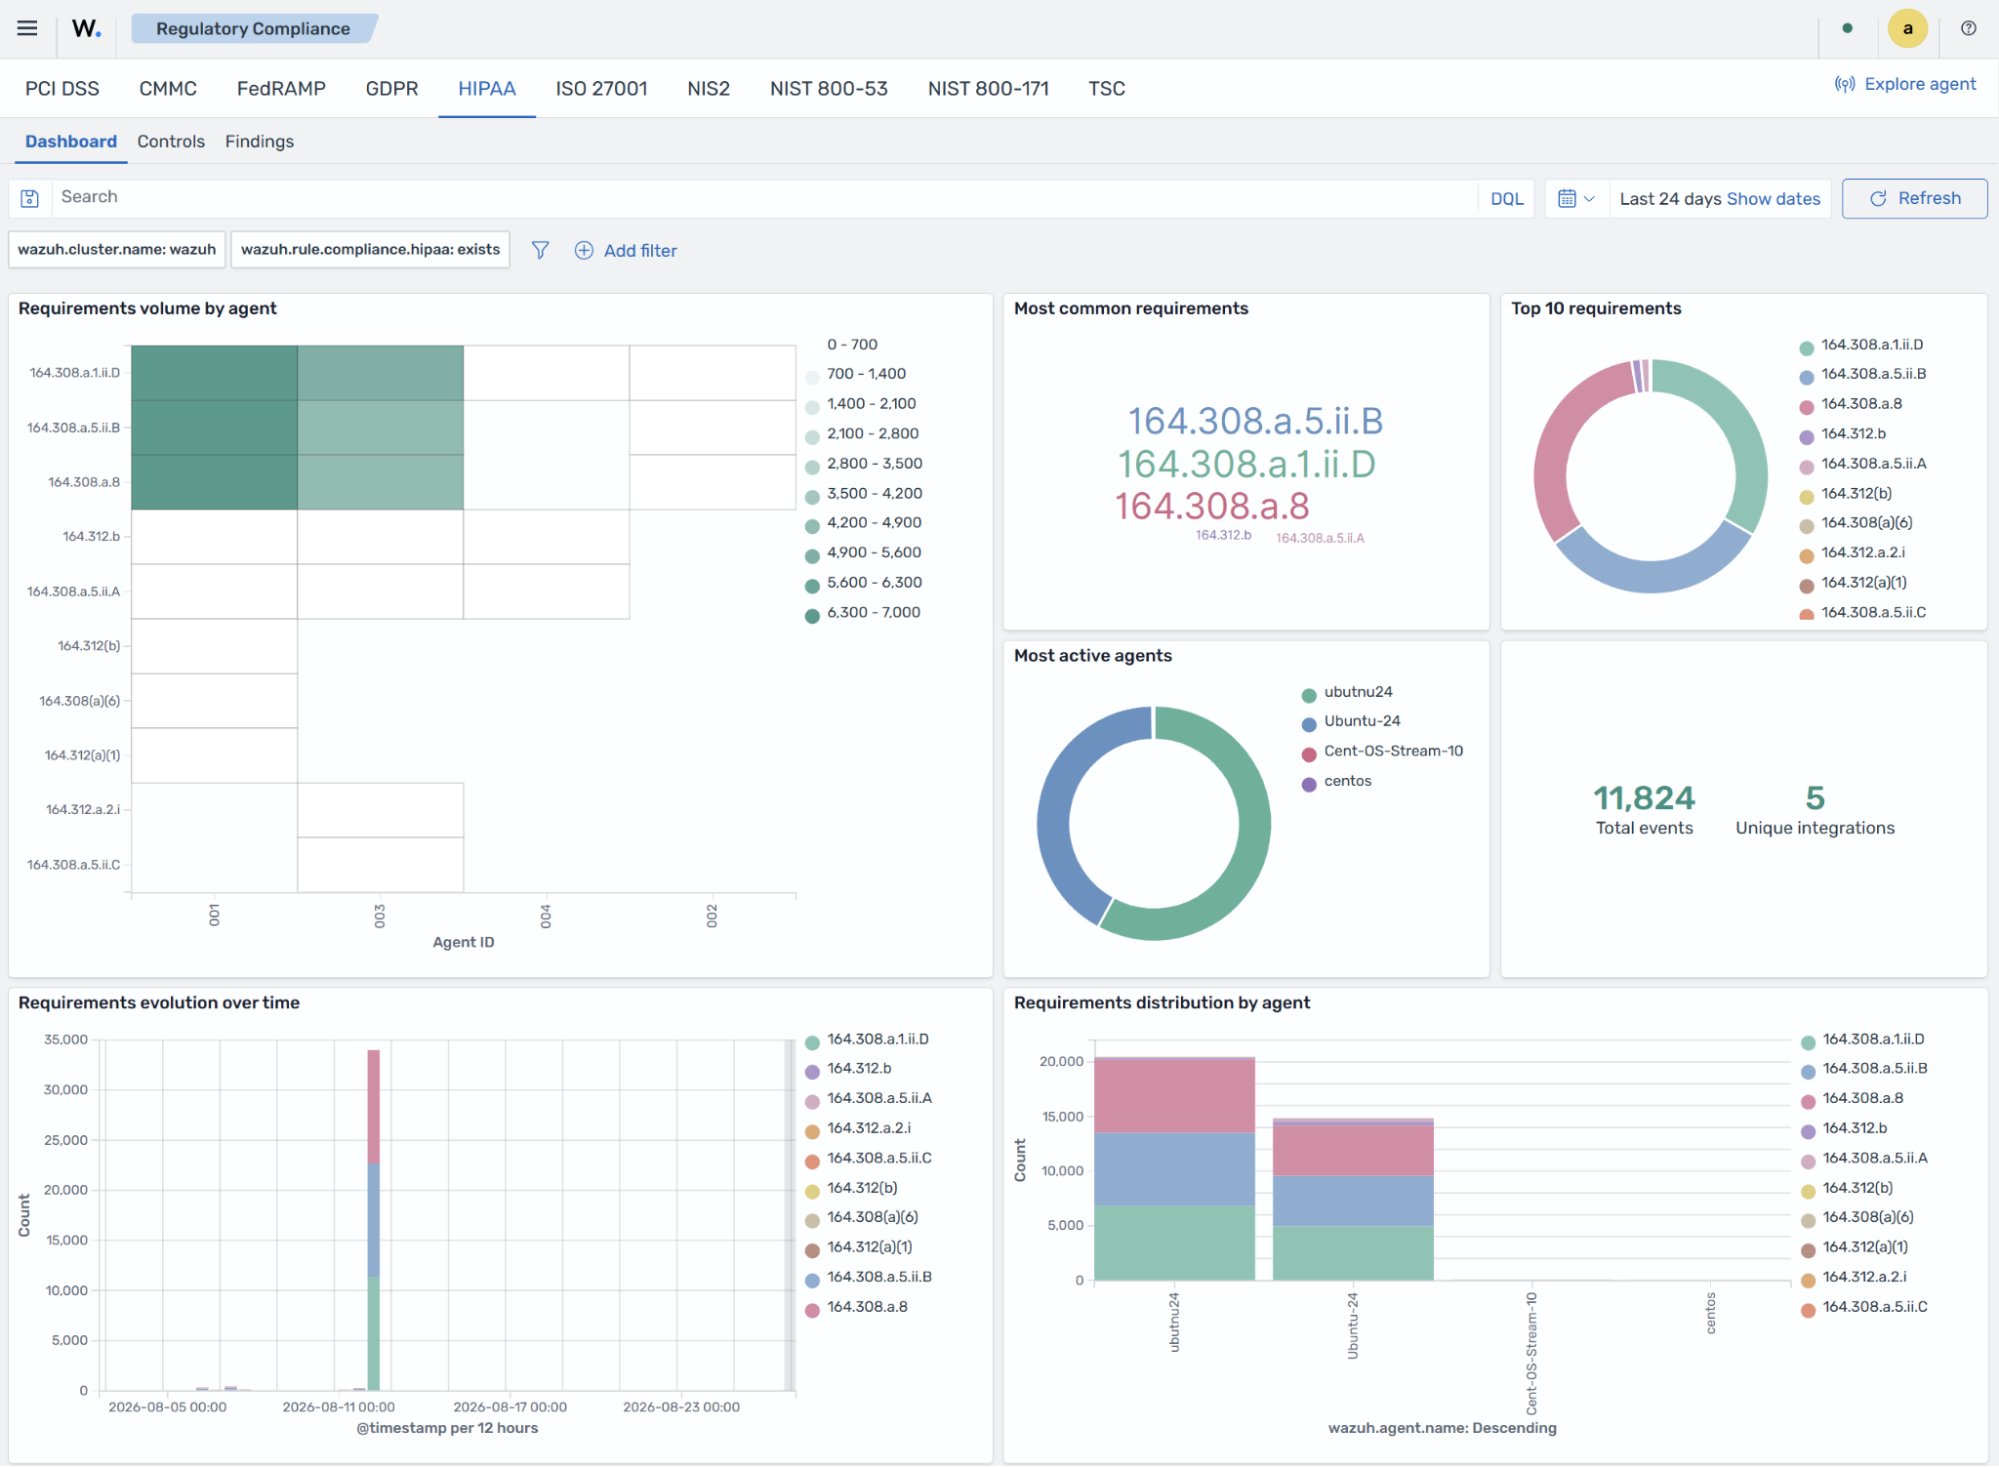
Click Dashboard to view requirement volume by agent, top requirements, active agents, and how HIPAA requirements change over time.
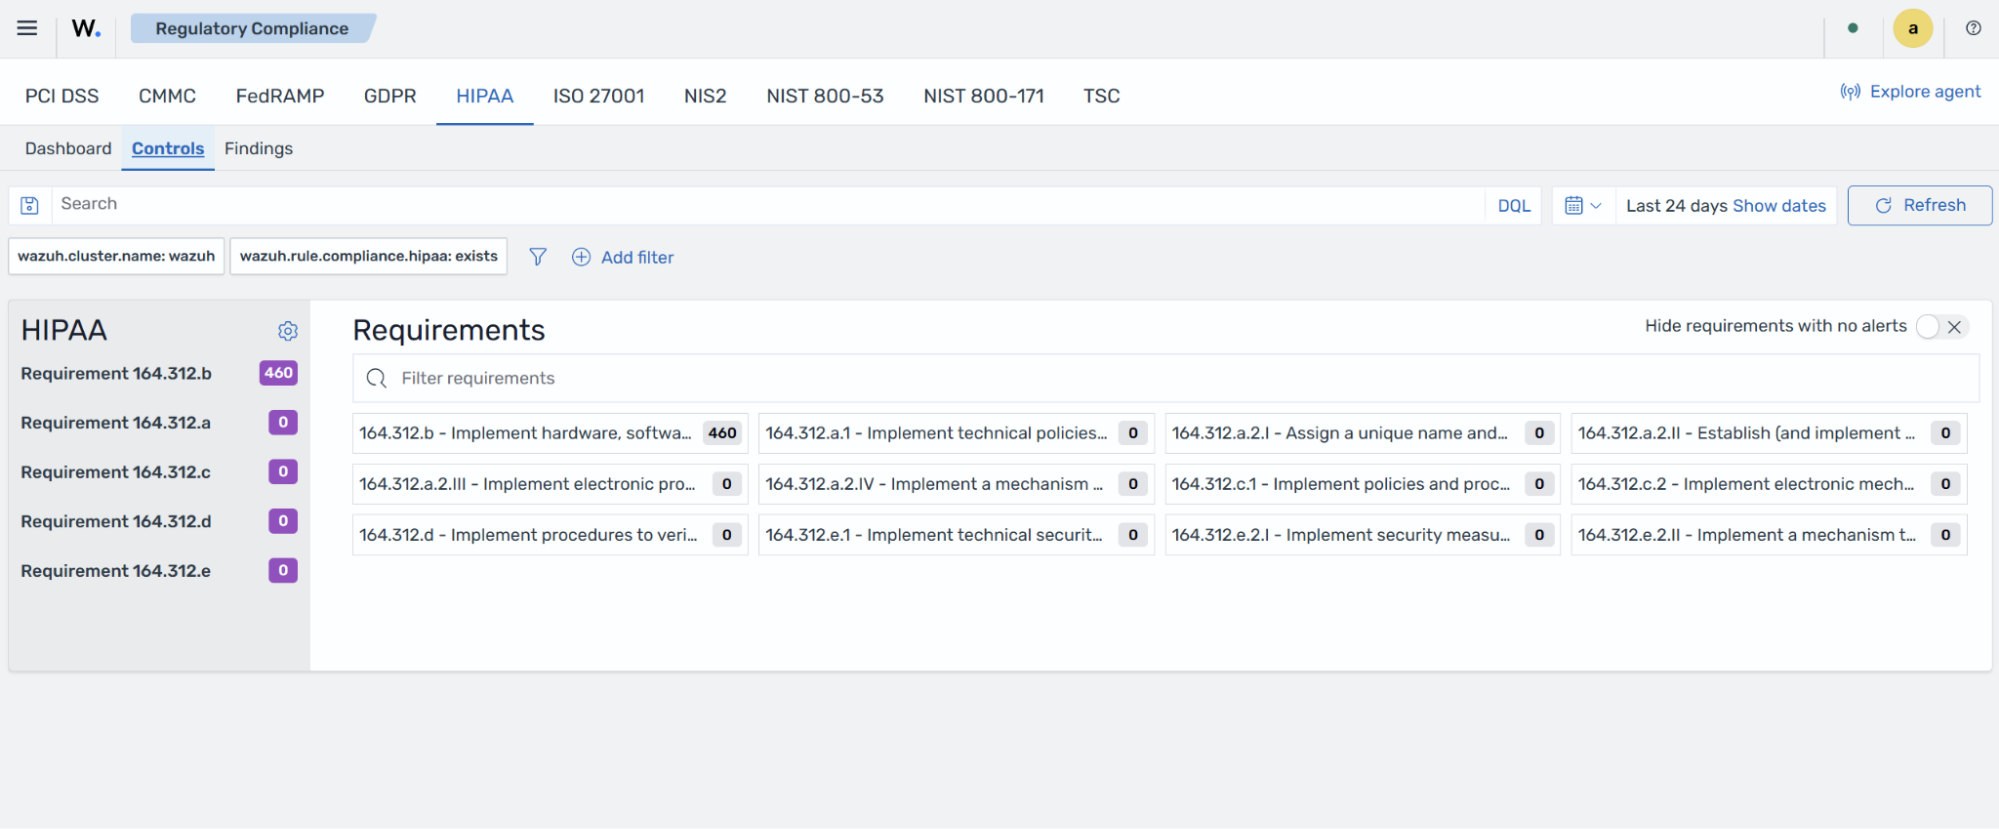
Switch to the Controls tab to view the HIPAA requirements breakdown.
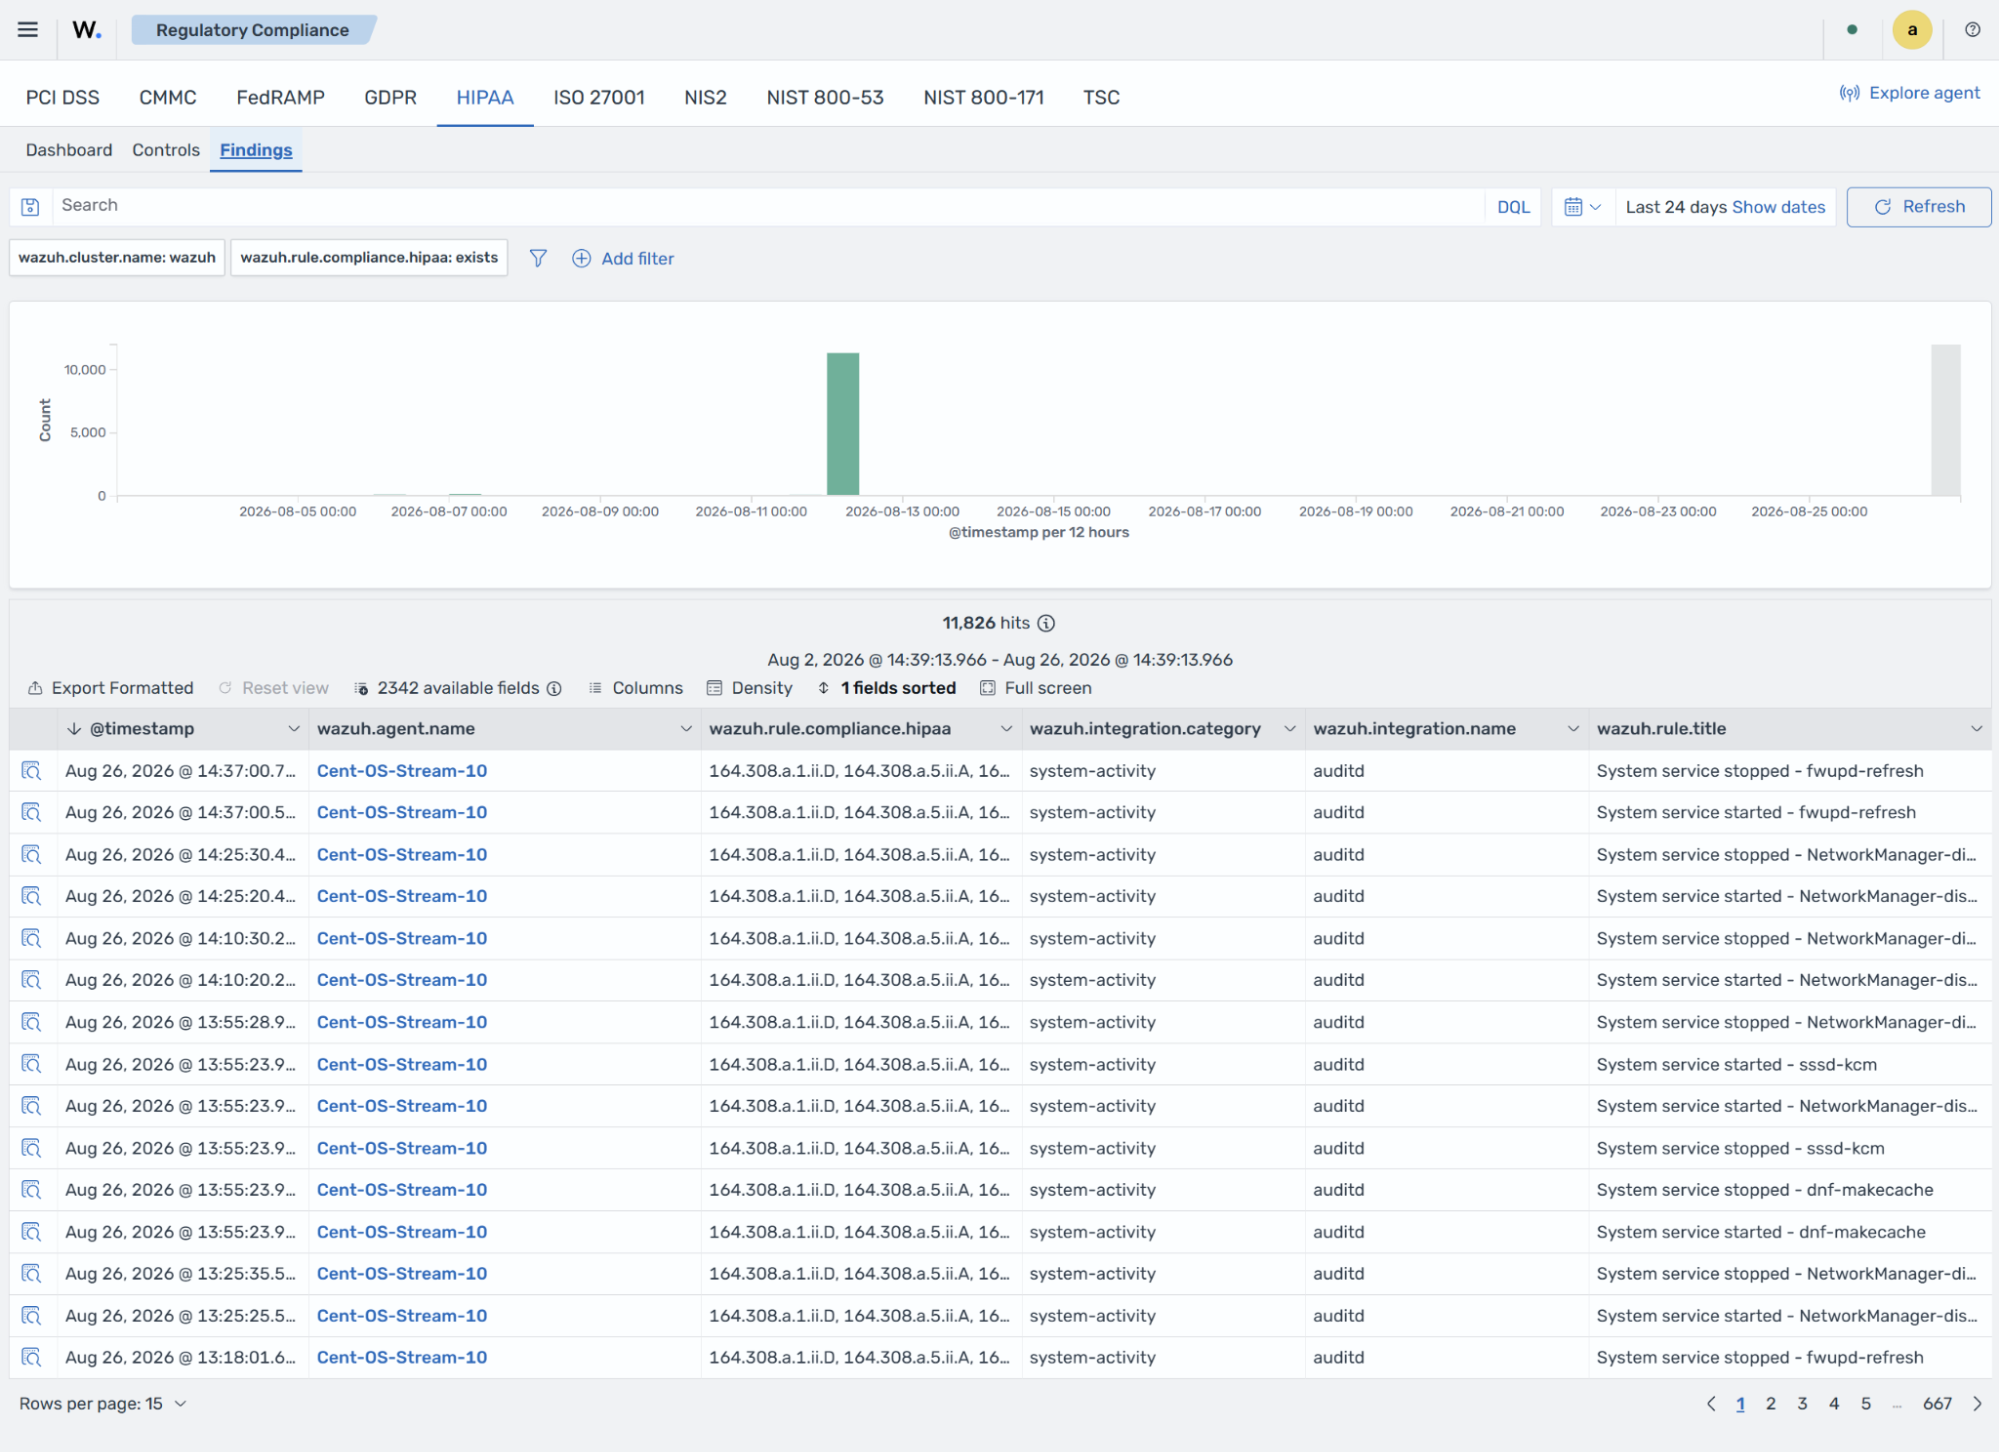
Switch to the Findings tab to see HIPAA findings generated within your environment regardless of the log source.
Wazuh has standard policies that include decoders, Key-Value Databases (KVDBs), and rules that detect attacks, system errors, security misconfigurations, and policy violations. By default, these rules map to the associated HIPAA requirements. In Wazuh 5.0, rules use the Sigma format. You can map a custom rule to one or more HIPAA requirements. To do this, add the requirement to the hipaa list under the compliance field of the rule. For example:
compliance:
  hipaa:
    - 164.308.a.1.ii.D
    - 164.308.a.3
    - 164.312.d
See the compliance section for more information about configuring compliance mappings for Wazuh rules.
The Wazuh for HIPAA guide (PDF) maps HIPAA compliance requirements to the Wazuh capabilities and modules that help address them. You can find examples of technical requirements that Wazuh supports in the following sections:
- HIPAA § 164.308(a)(1)(ii)(A) - Risk analysis
- HIPAA § 164.308(a)(5)(ii)(B) - Protection from malicious software
- HIPAA § 164.308(a)(6)(ii) - Response and reporting
- HIPAA § 164.308(a)(8) - Evaluation
- HIPAA § 164.312(a)(2)(iii) - Automatic logoff
- HIPAA § 164.312(b) - Audit controls
- HIPAA § 164.312(c)(2) - Mechanism to authenticate electronic protected health information
- HIPAA § 164.312(d) - Person or entity authentication