Amazon Inspector
Amazon Inspector is an automated vulnerability management service that continually scans Amazon EC2 instances, container images in Amazon ECR, and AWS Lambda functions for software vulnerabilities and unintended network exposure. It produces detailed security findings prioritized by severity, which you can review in the Amazon Inspector console or through its API.
Note
The Wazuh module for AWS collects findings from Amazon Inspector only. Amazon Inspector Classic isn't supported.
AWS configuration
Learn how to configure the Amazon Inspector integration in Wazuh.
Amazon Inspector configuration
Open the Amazon Inspector page in the AWS Management Console.
Click Get Started to access the dashboard.
Configure your scanning preferences under General settings:
Enable EC2 scanning
Enable ECR scanning
Enable Lambda function scanning
Note
For detailed instructions on configuring scanning preferences, see the Amazon Inspector documentation.
Policy configuration
Follow the creating an AWS policy guide to create a policy using the Amazon Web Services console.
Take into account that the policies below follow the principle of least privilege to ensure that only the minimum permissions are provided to the AWS IAM user.
To allow an AWS user to use the Wazuh module for AWS with read-only permissions, it must have a policy like the following attached:
{
    "Version": "2012-10-17",
    "Statement": [
        {
            "Sid": "VisualEditor0",
            "Effect": "Allow",
            "Action": [
                "inspector2:ListFindings"
            ],
            "Resource": "*"
        }
    ]
}
After creating a policy, you can attach it directly to a user or to a group to which the user belongs. In attaching a policy to an IAM user group, you see how to attach a policy to a group. More information on how to use other methods is available in the AWS documentation.
Configure Wazuh to process Amazon Inspector logs
Access the Wazuh configuration in Server management > Settings using the Wazuh dashboard or by manually editing the
/var/ossec/etc/ossec.conffile in the Wazuh server or agent.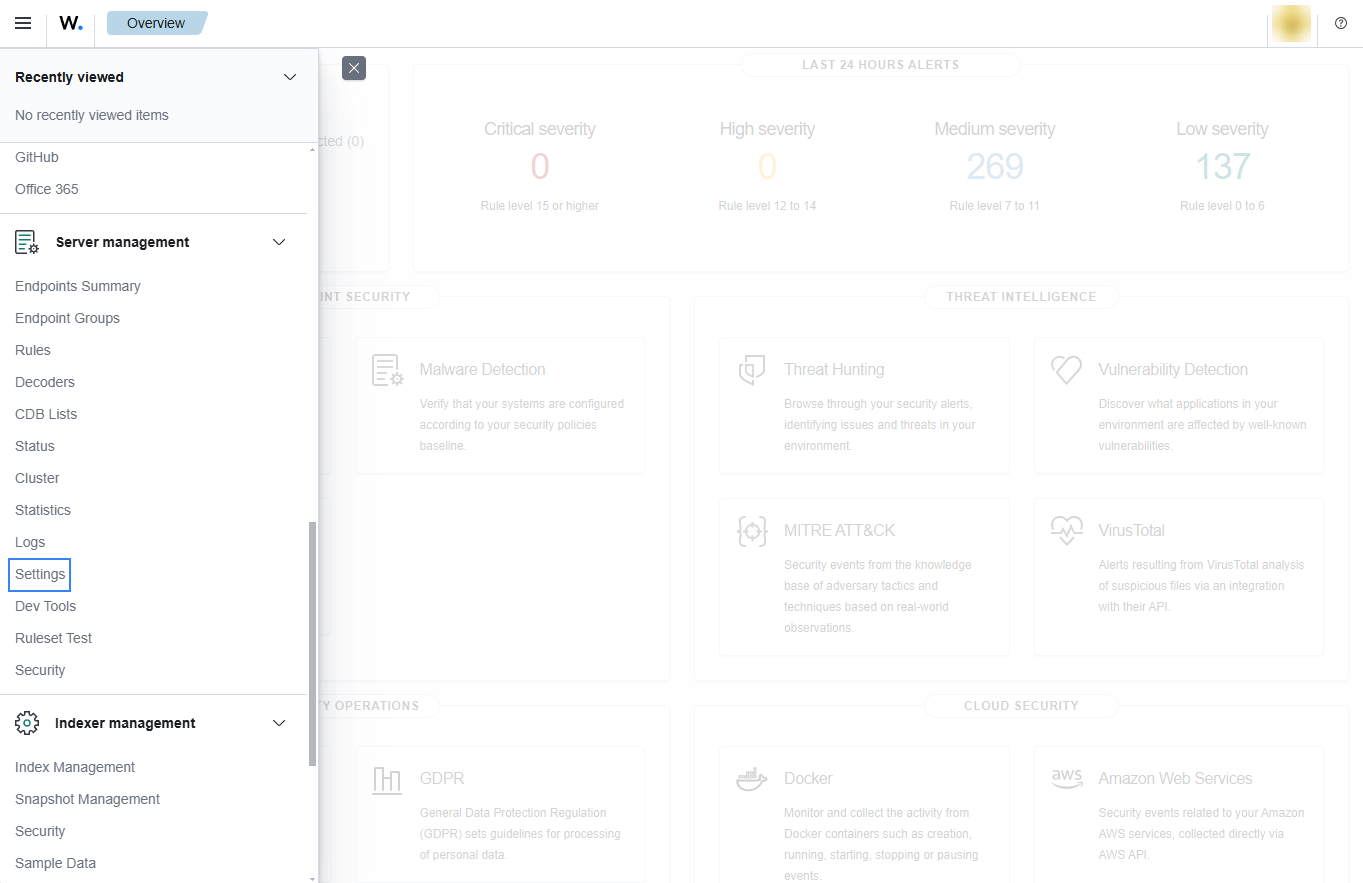
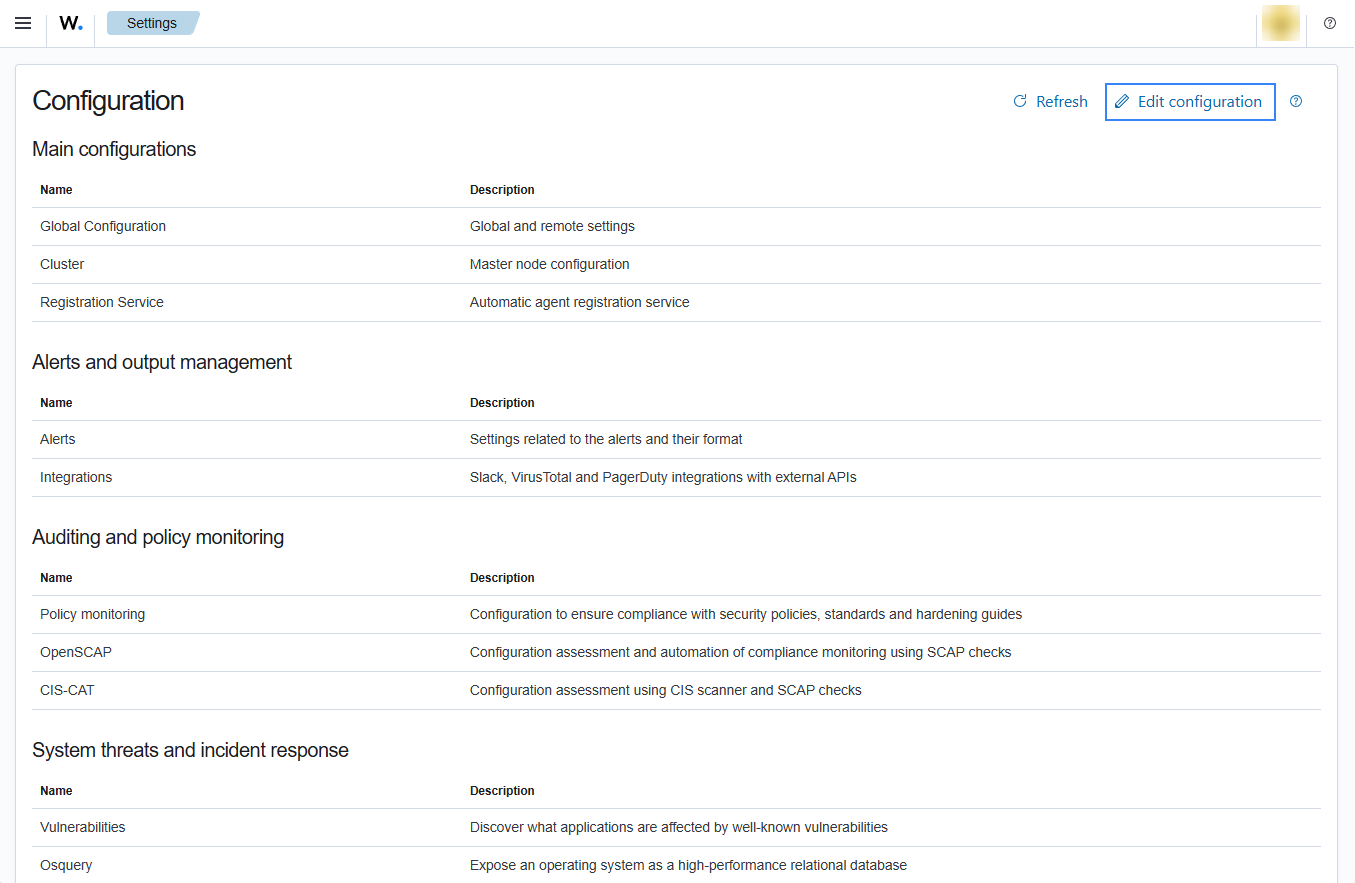
Add the following Wazuh module for AWS configuration block to enable the integration with Amazon Inspector:
<wodle name="aws-s3">
  <disabled>no</disabled>
  <interval>10m</interval>
  <run_on_start>no</run_on_start>
  <skip_on_error>no</skip_on_error>
  <service type="inspector">
    <aws_profile>default</aws_profile>
    <regions>us-east-1,us-east-2</regions>
  </service>
</wodle>
You must specify at least a region. You can add multiple comma-separated regions.
Note
Amazon Inspector findings have
aws.sourceset toinspector2.Save the changes and restart Wazuh to apply the changes. The service can be manually restarted using the following command outside the Wazuh dashboard:
Wazuh manager:
# systemctl restart wazuh-manager
Wazuh agent:
# systemctl restart wazuh-agent